
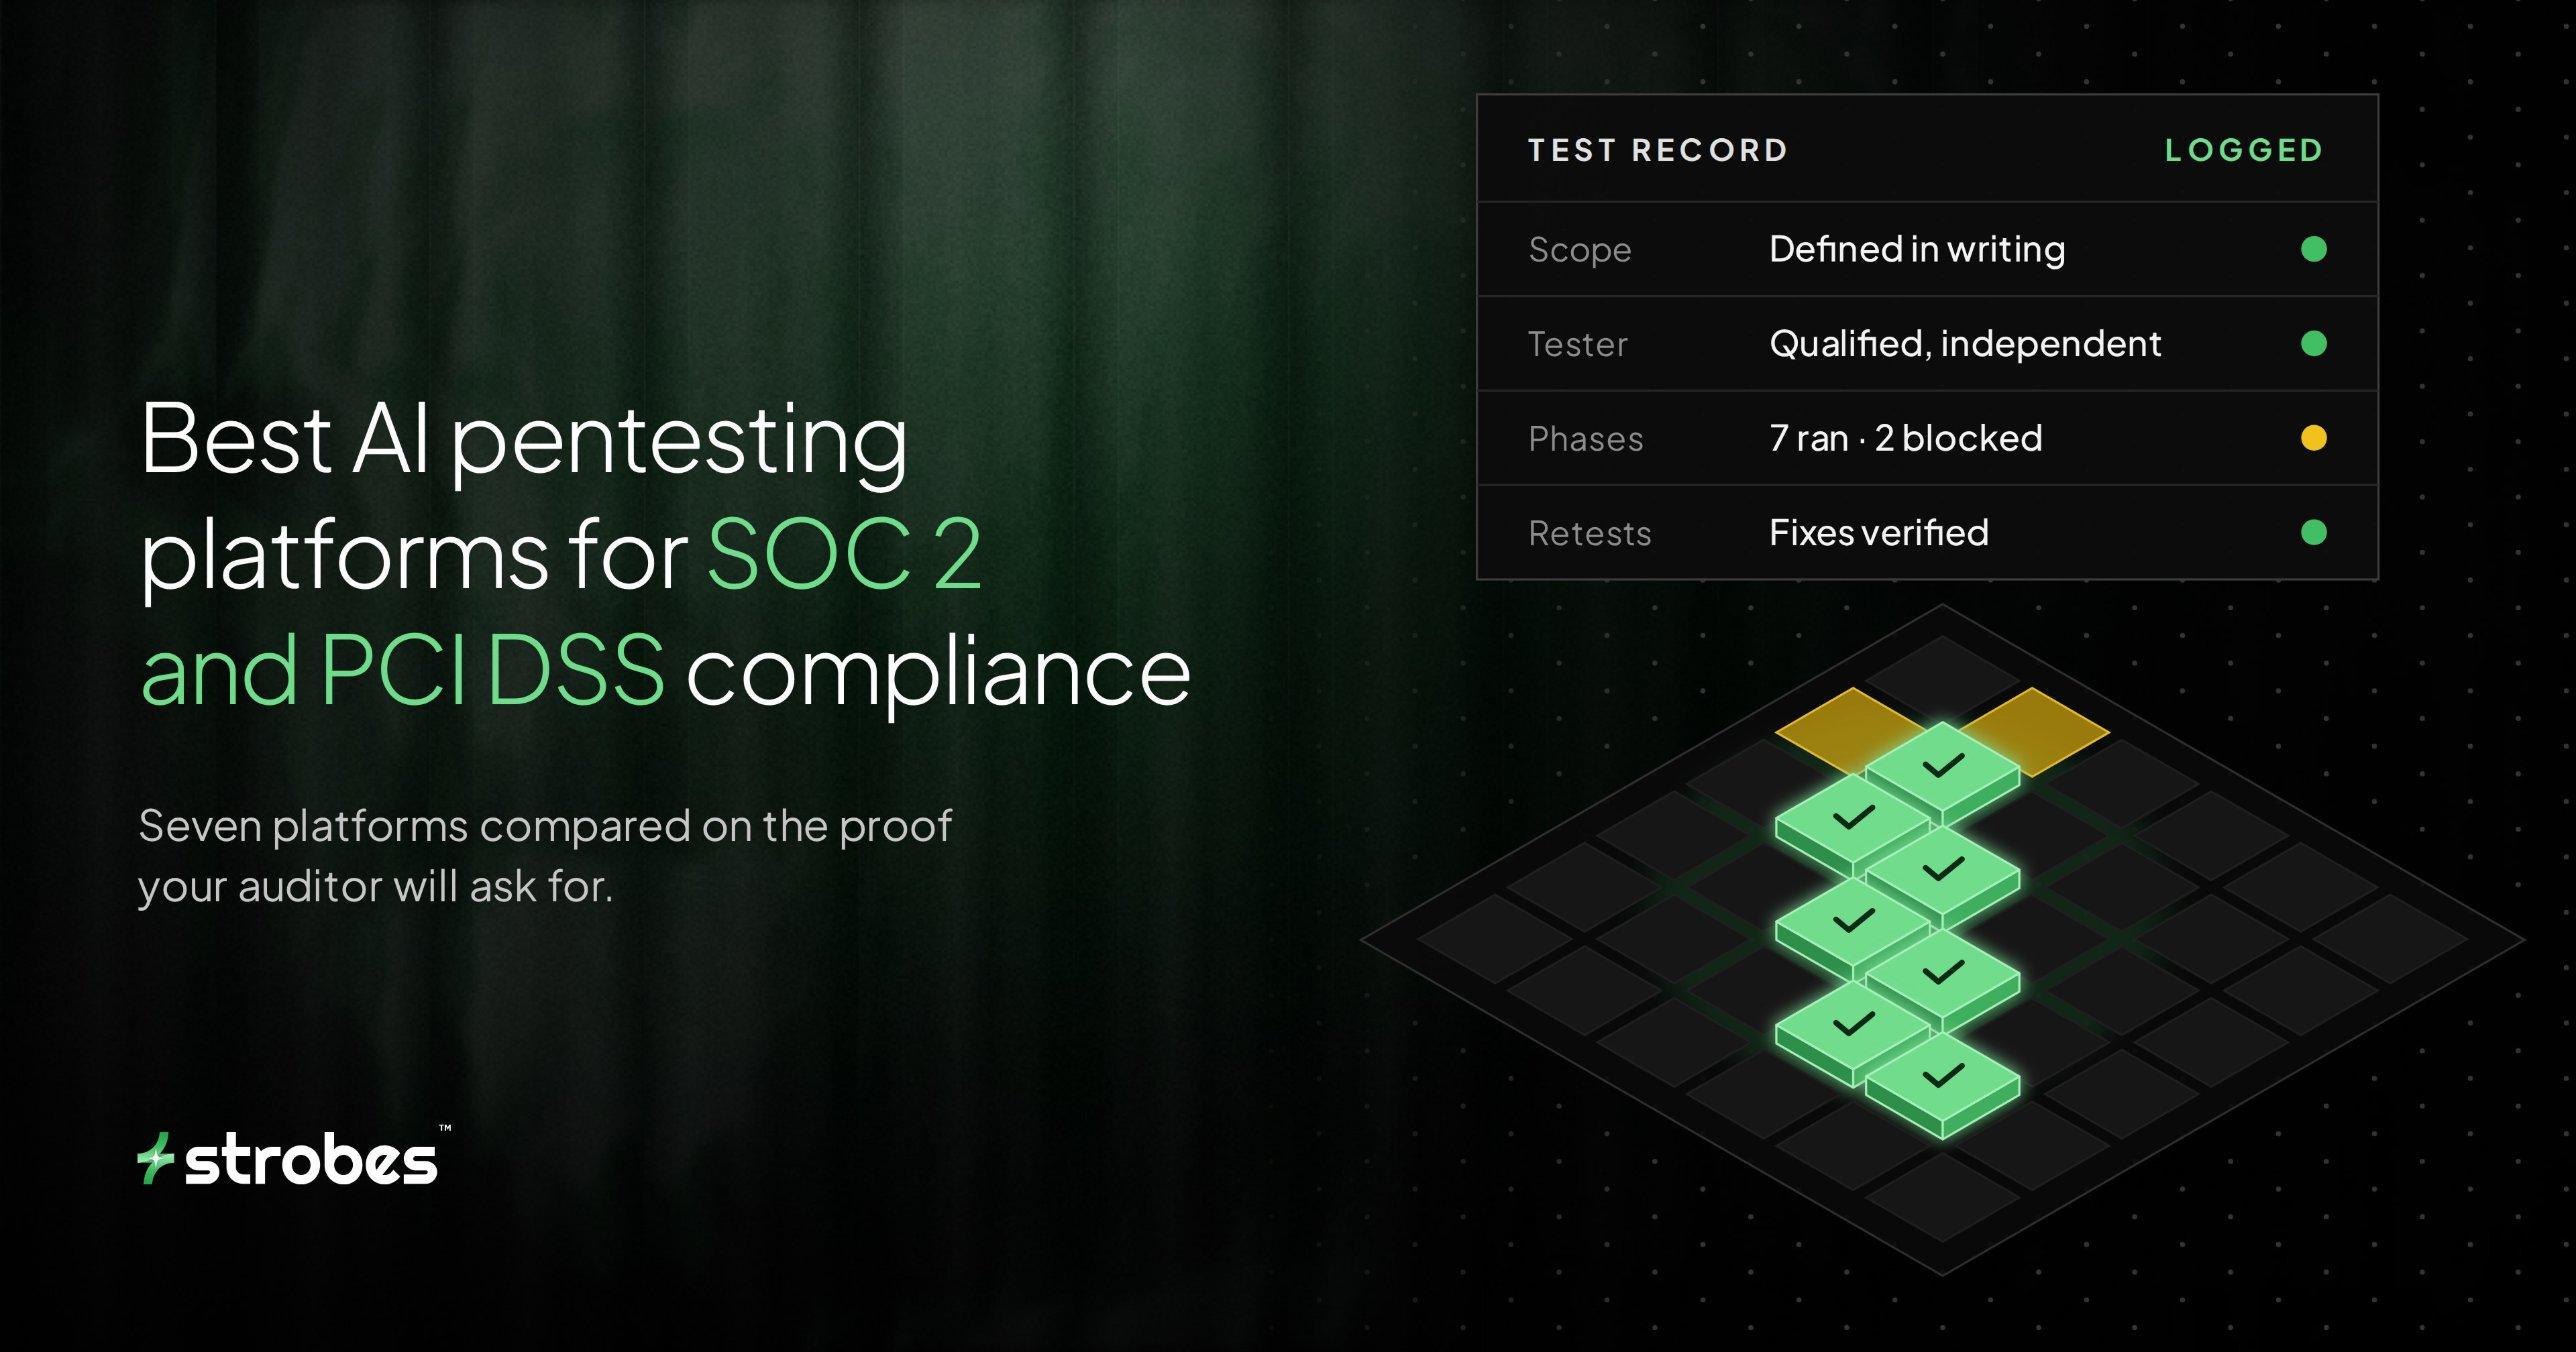
Best AI pentesting platforms for SOC 2 and PCI DSS compliance
Seven AI pentesting platforms compared on what SOC 2 and PCI DSS v4.0.1 actually ask for: scope, who tests, retests, and proof of what ran and what didn't.
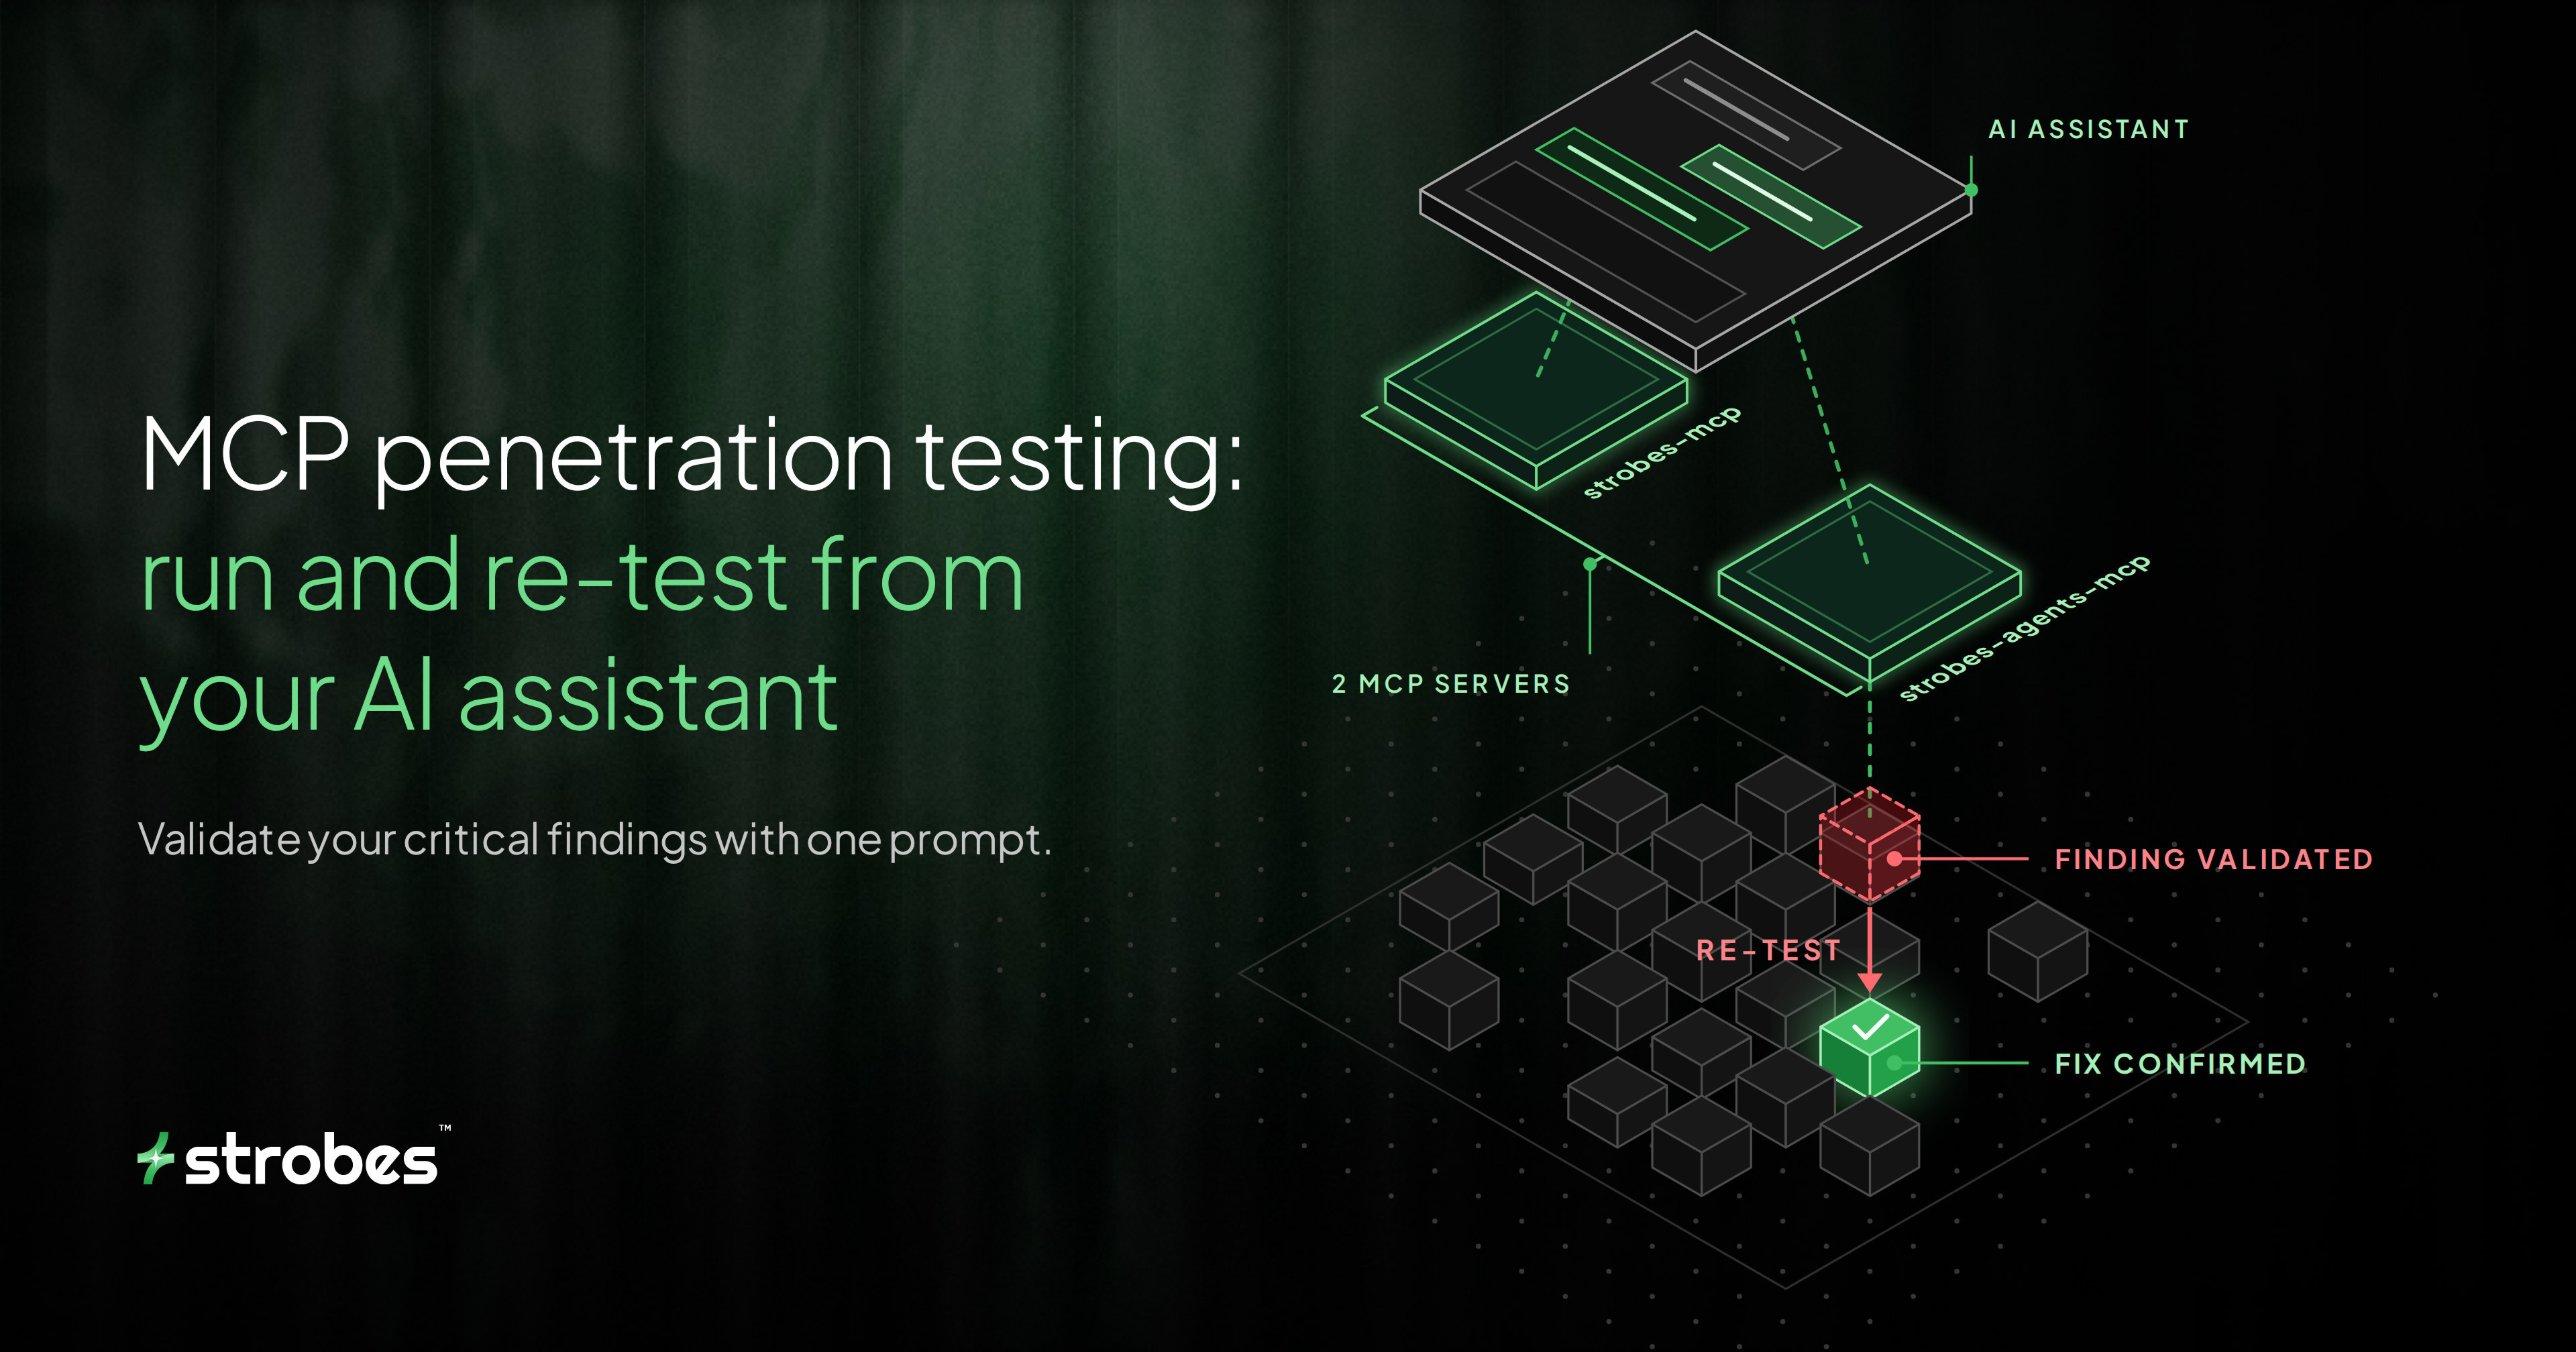
MCP penetration testing: run and re-test from your AI assistant
Meet the Strobes MCP servers for penetration testing. Start agentic pentests, check the findings, and re-test your fixes, right from your AI assistant.
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
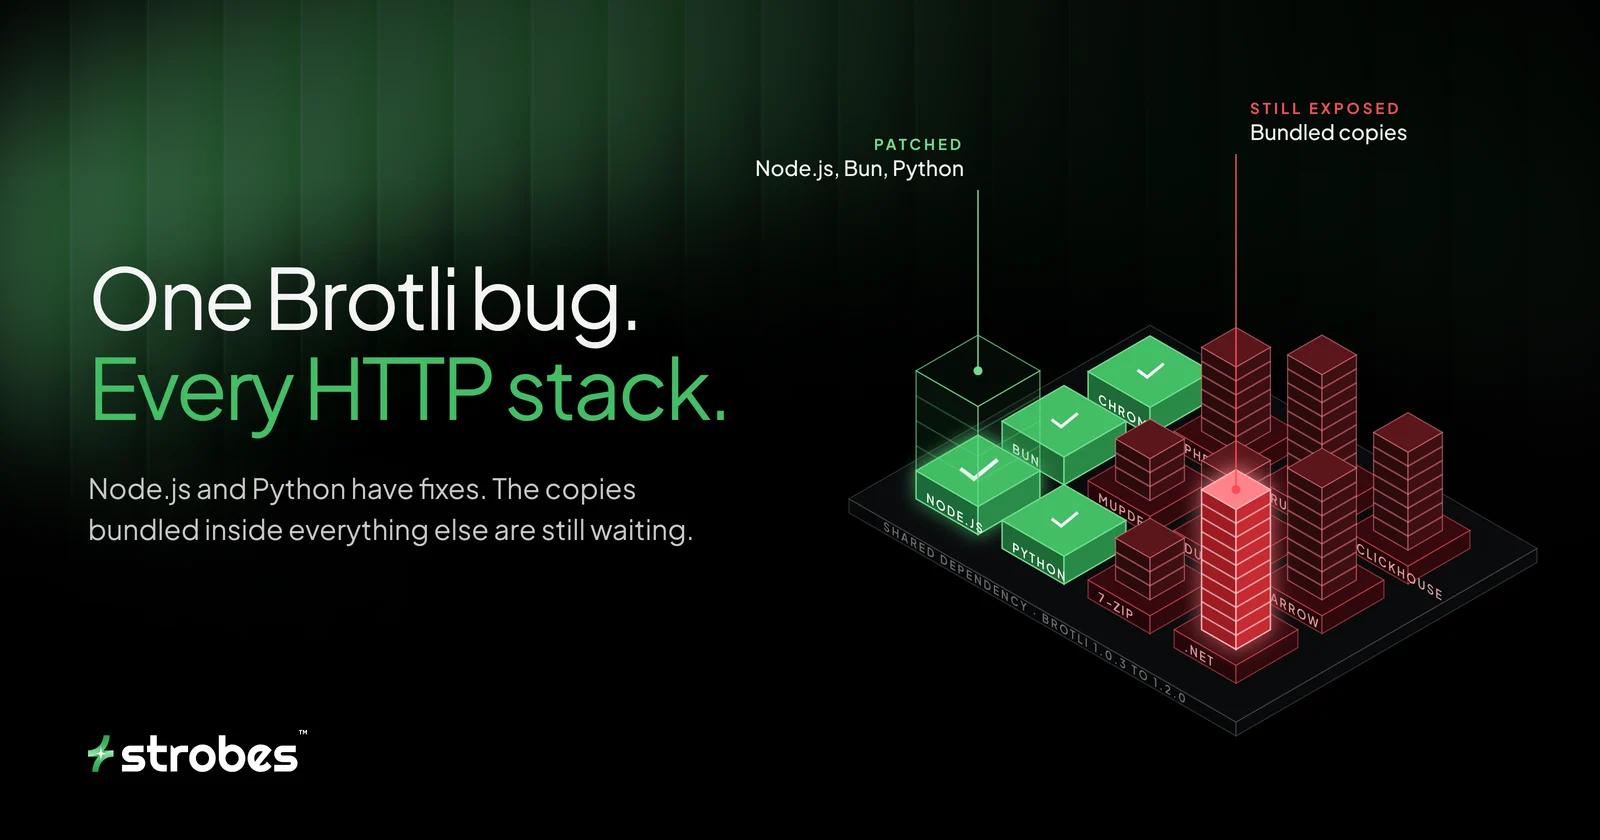
HTTP2Shell (CVE-2026-111497): The Brotli RCE Hitting Node.js, Python and More
HTTP2Shell (CVE-2026-111497), first called Node2Shell, is a Brotli decoder flaw that can lead to remote code execution in Node.js, Python, Bun and any app that decodes untrusted br content. Affected versions, exposure paths, checks and fixes.
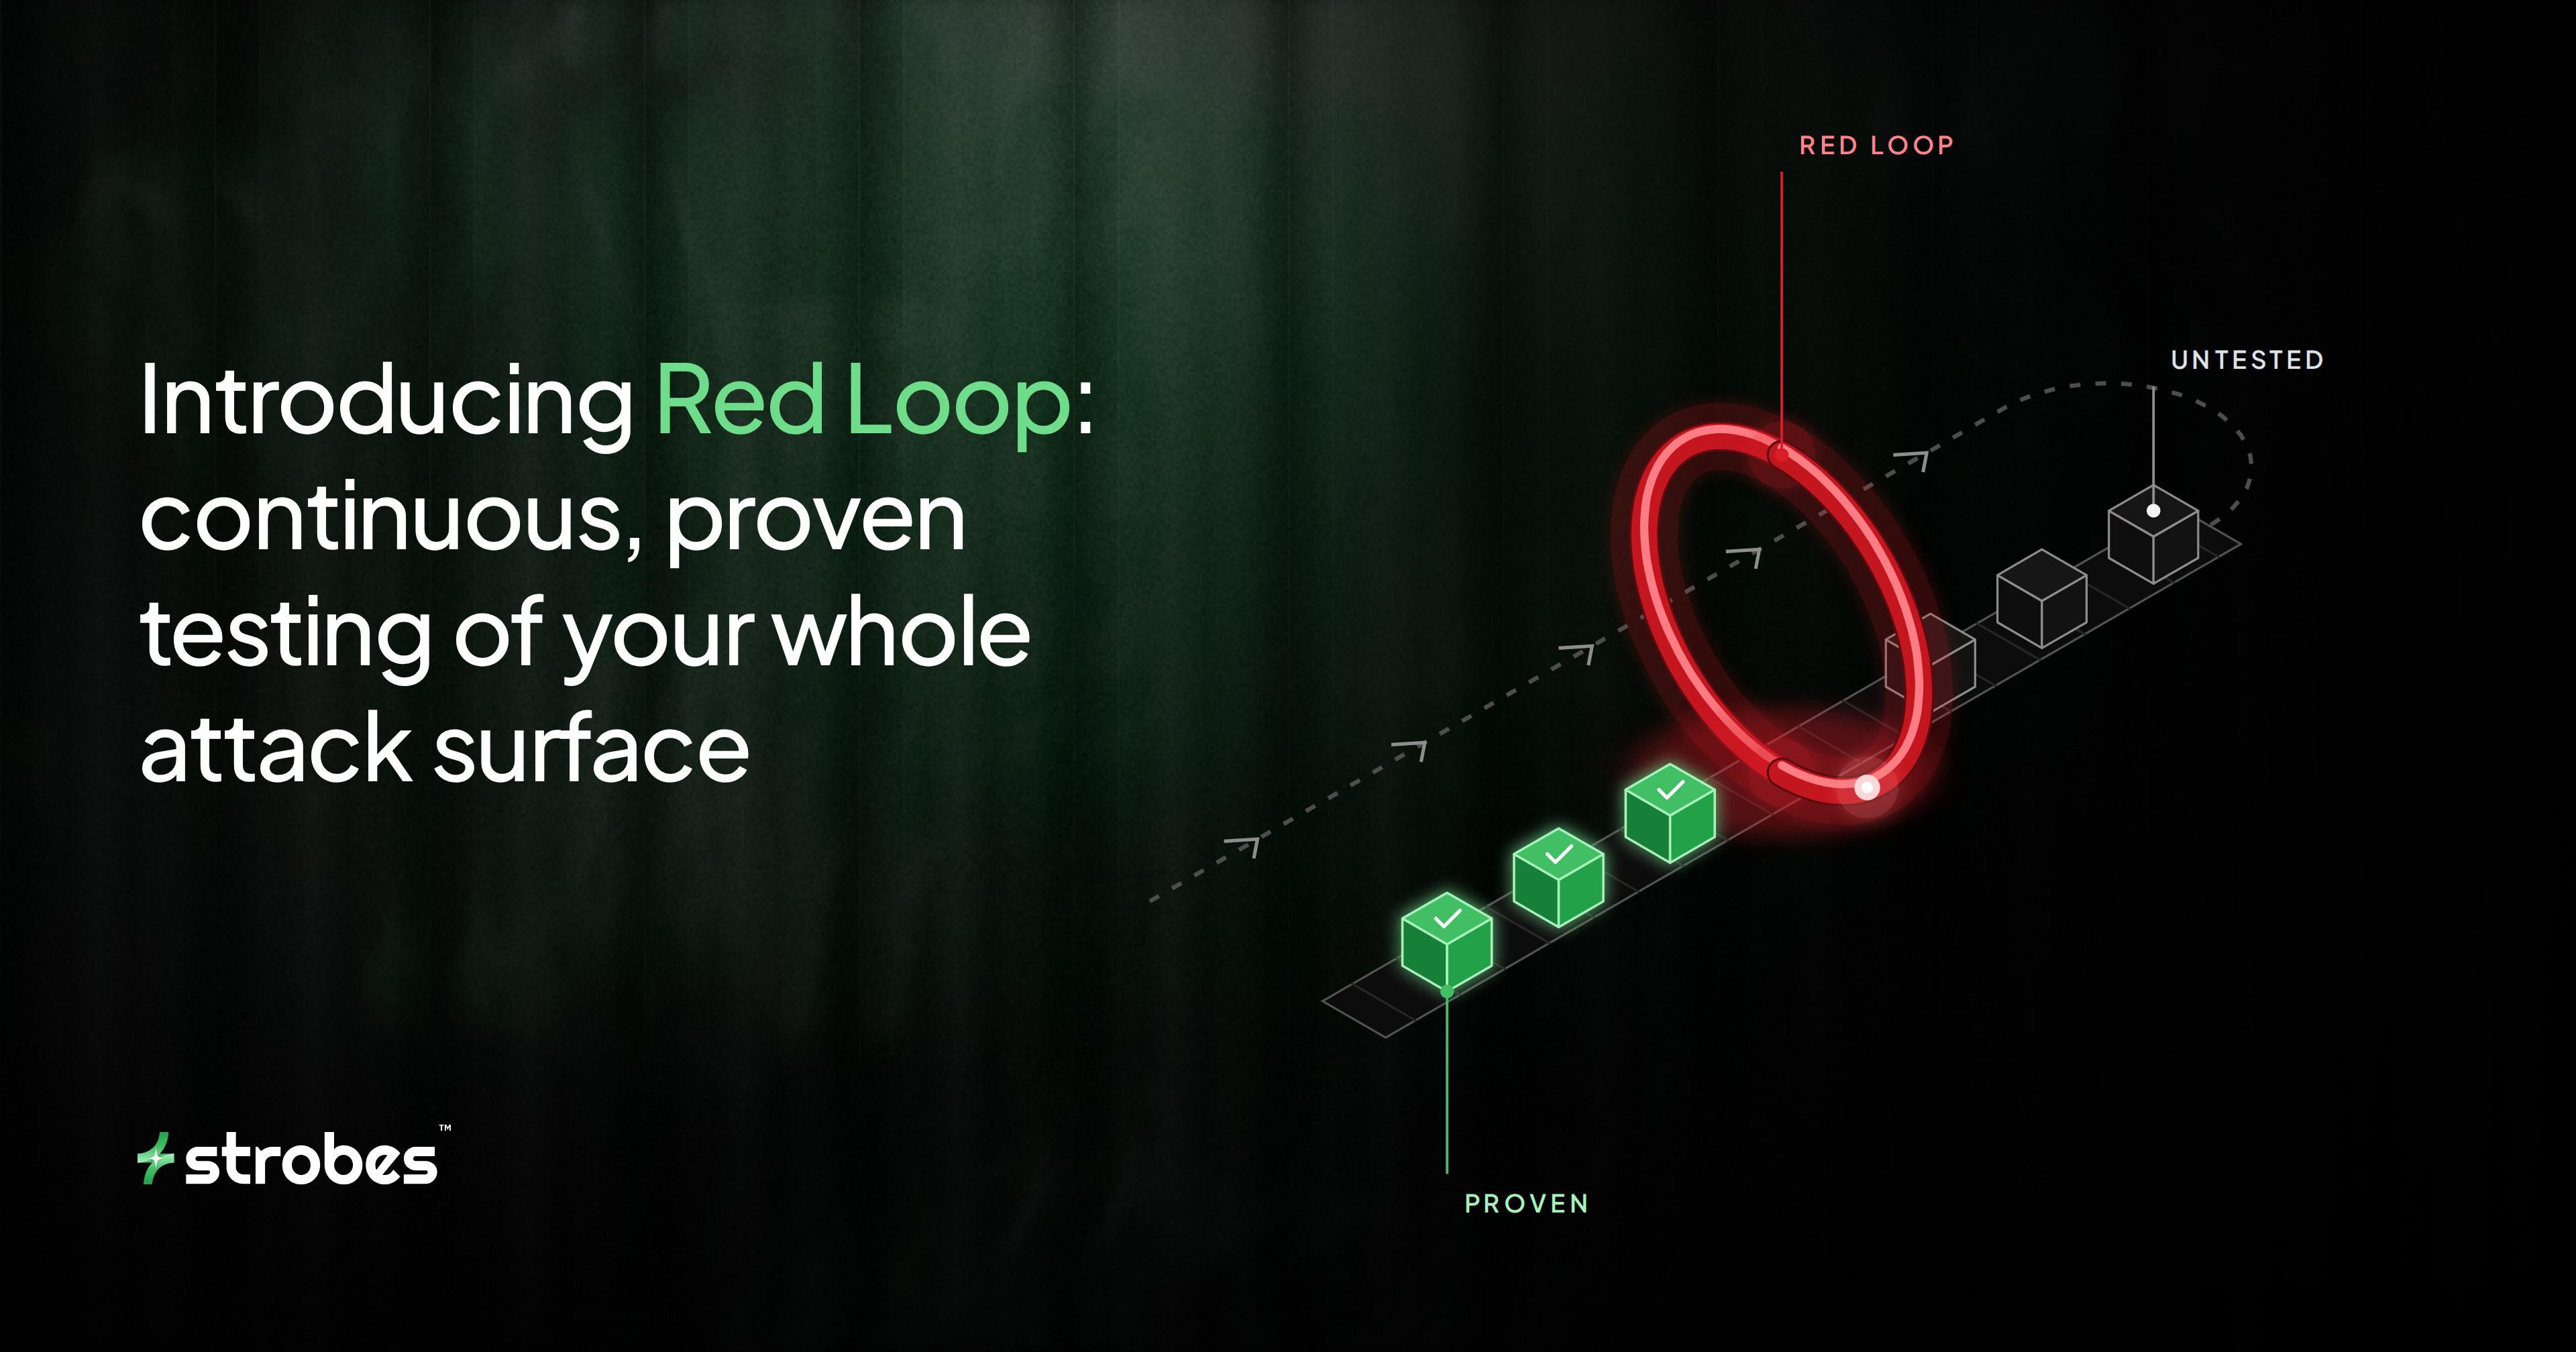
Introducing Red Loop: continuous, proven testing of your whole attack surface
Red Loop brings continuous offensive testing to Strobes Attack Surface Management. It discovers what you own, scans it the same way every time, and sends results to AI agents that attack and validate them. Only proven findings reach your queue.
PHP2Shell (CVE-2026-109618 & CVE-2026-109619): Leaked PHP Flaws and What to Do Now
PHP2Shell: two leaked critical PHP RCE flaws, CVE-2026-109618 and CVE-2026-109619, rated CVSS 9.2. What's confirmed, which PHP versions get the fix, and what to do before and after the October 21 patch.

Your board won't ask if you're secure anymore. It will ask you to prove it.
Boards now ask for evidence that cyber risk is within appetite. What board-ready security evidence looks like, how to govern autonomous testing, and how to get it into your 2027 plan.

Why your annual penetration test is already obsolete
Your annual pentest describes an environment that no longer exists. Here is how continuous offensive security testing closes the gap, and what it takes to run one.

Biggest data breaches of September 2026
153 million driver's licenses claimed, 23.6 million Gyazo records confirmed. September 2026's biggest breaches, with every number sourced.

Strobes Agentic Pentesting Now Tests Android Apps on Your Own Devices
Strobes Agentic Pentesting now runs Android app pentesting on your own phones and emulators: live crawling, traffic interception, Frida instrumentation, and verified findings.

Top CVEs of September 2026: Four Zero-Days, and Patching Wasn’t the Fix
Four of September 2026’s top five CVEs were exploited before a patch existed. Fix order, fixed builds, and the compromise check each one needs.

Strobes joins OpenAI's Daybreak program
OpenAI gates its cyber models behind an application, identity checks, and workspace scoping. Strobes is now verified for Daybreak.

Where your data goes during an AI pentest
Session tokens, customer records, error traces. Here's exactly where that data goes during an agentic pentest, and what to ask any vendor.