
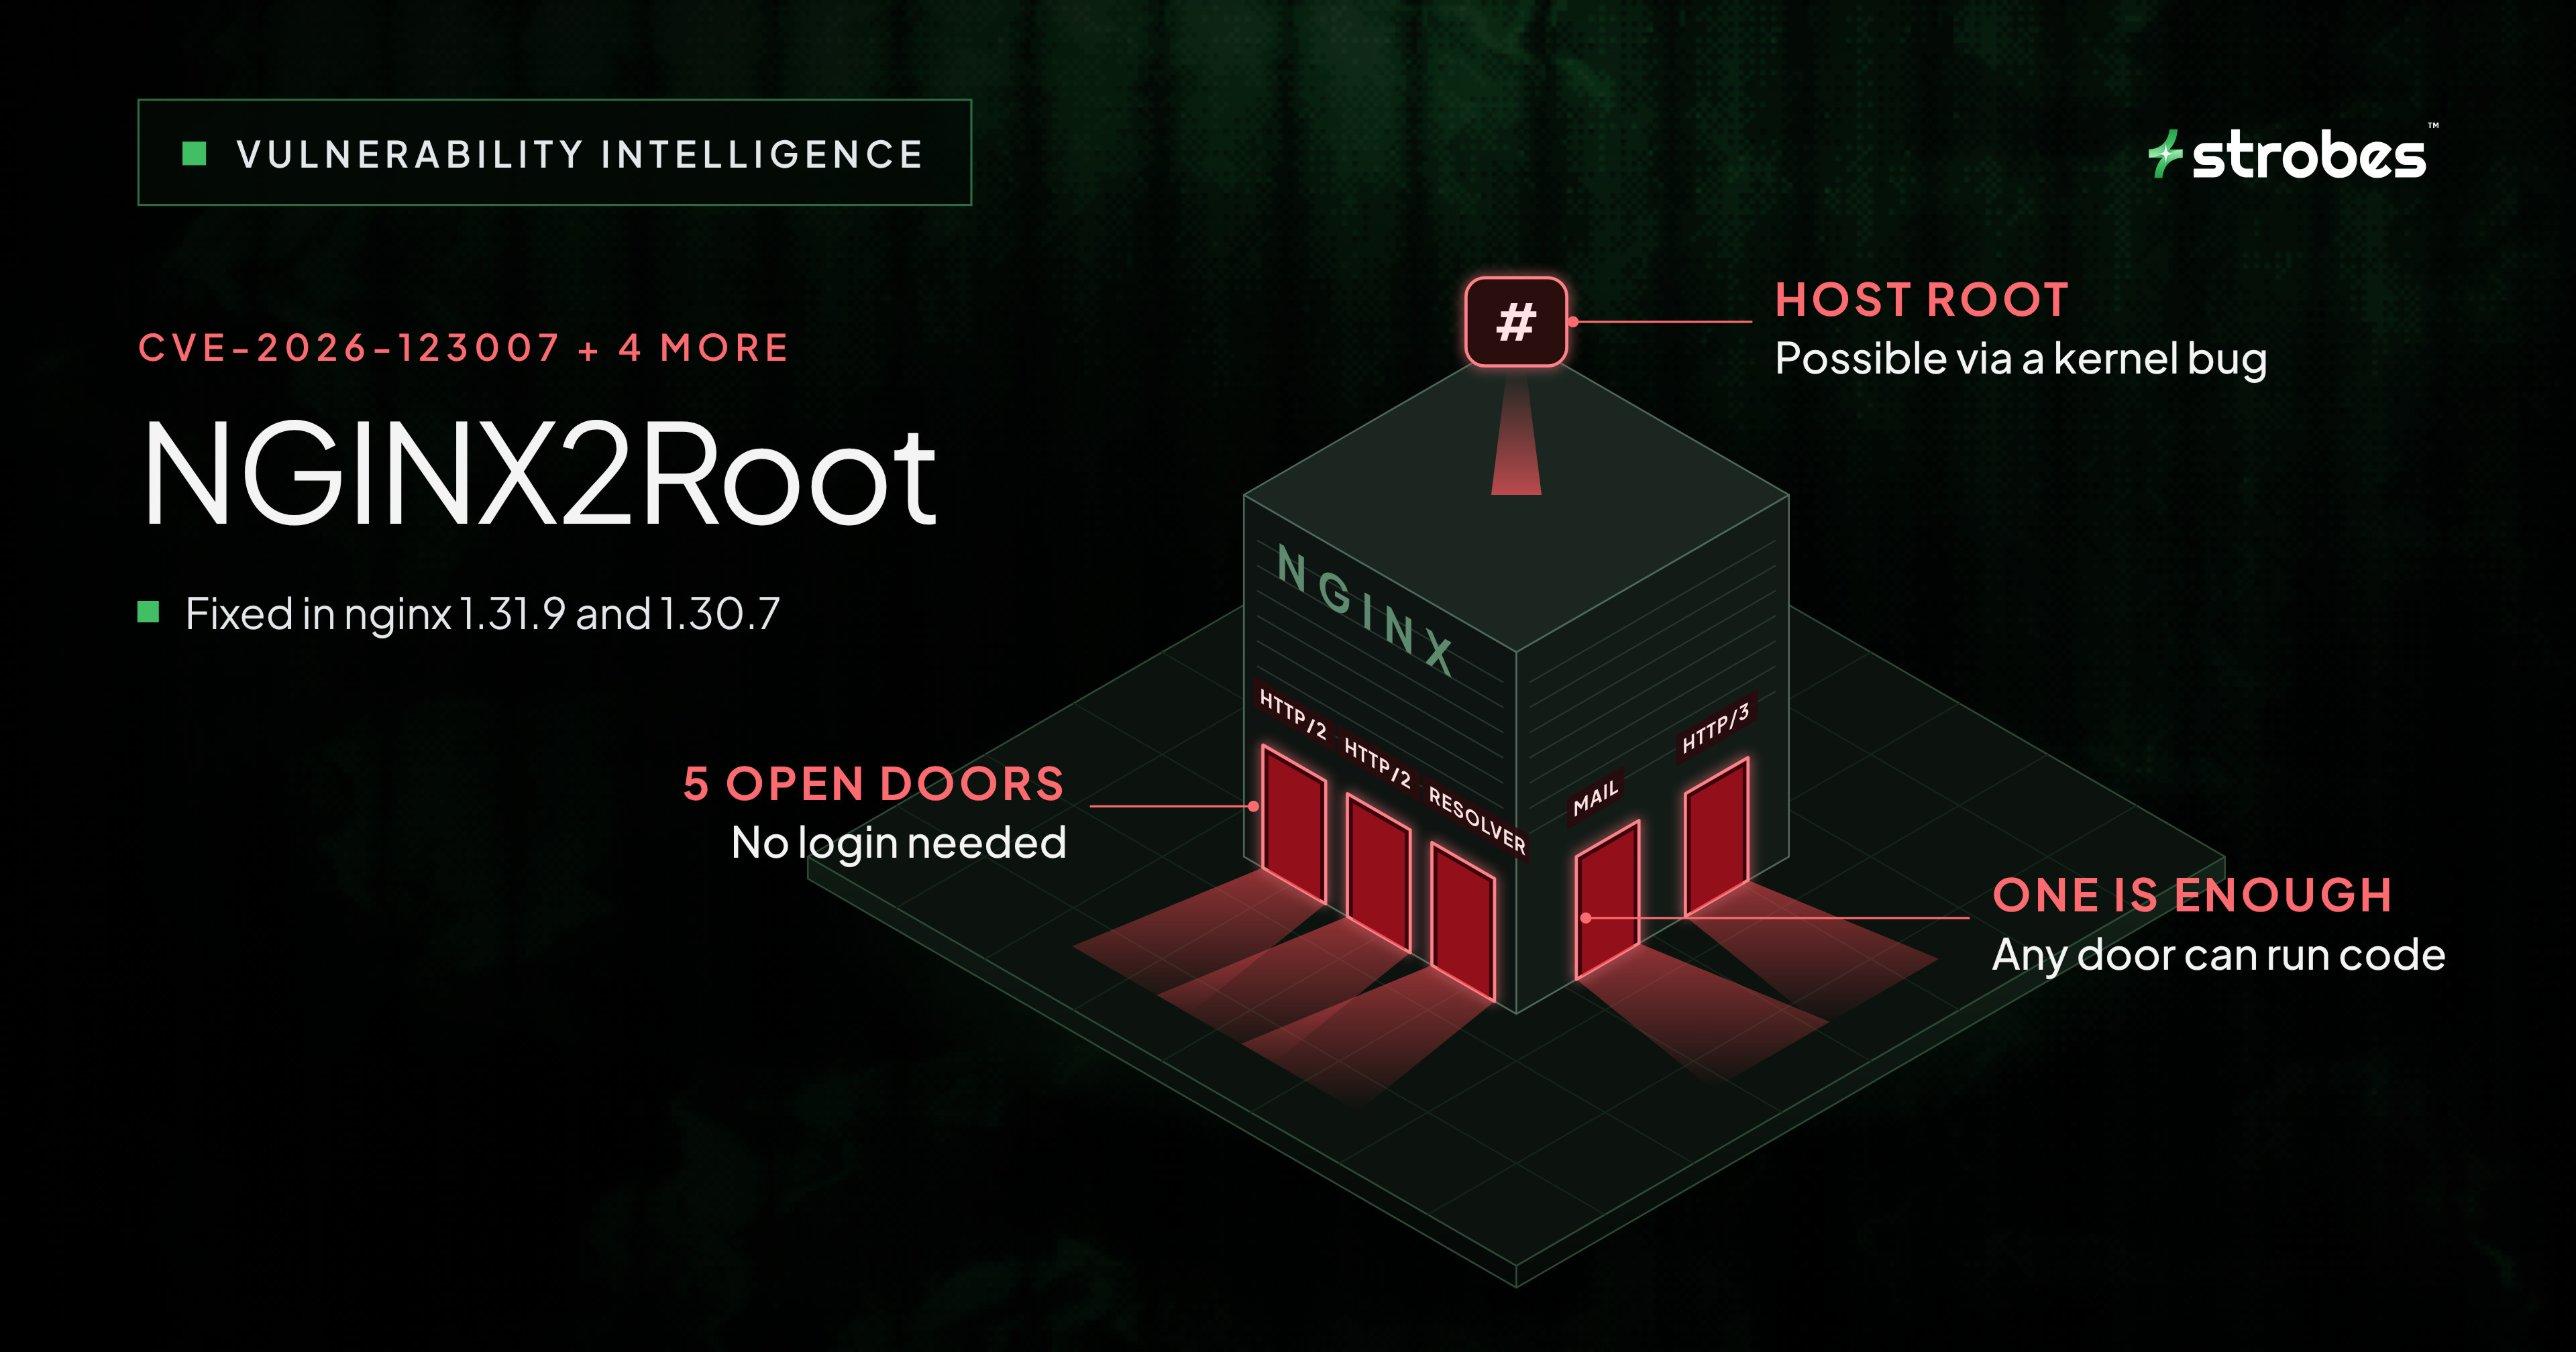
NGINX2Root flaws put nginx servers at risk of takeover
NGINX2Root is five pre-auth nginx memory bugs, led by CVE-2026-123007 in HTTP/2, plus an unpatched kernel bug that leads to host root. Here's what's affected, how to fix it and how to spot attacks.
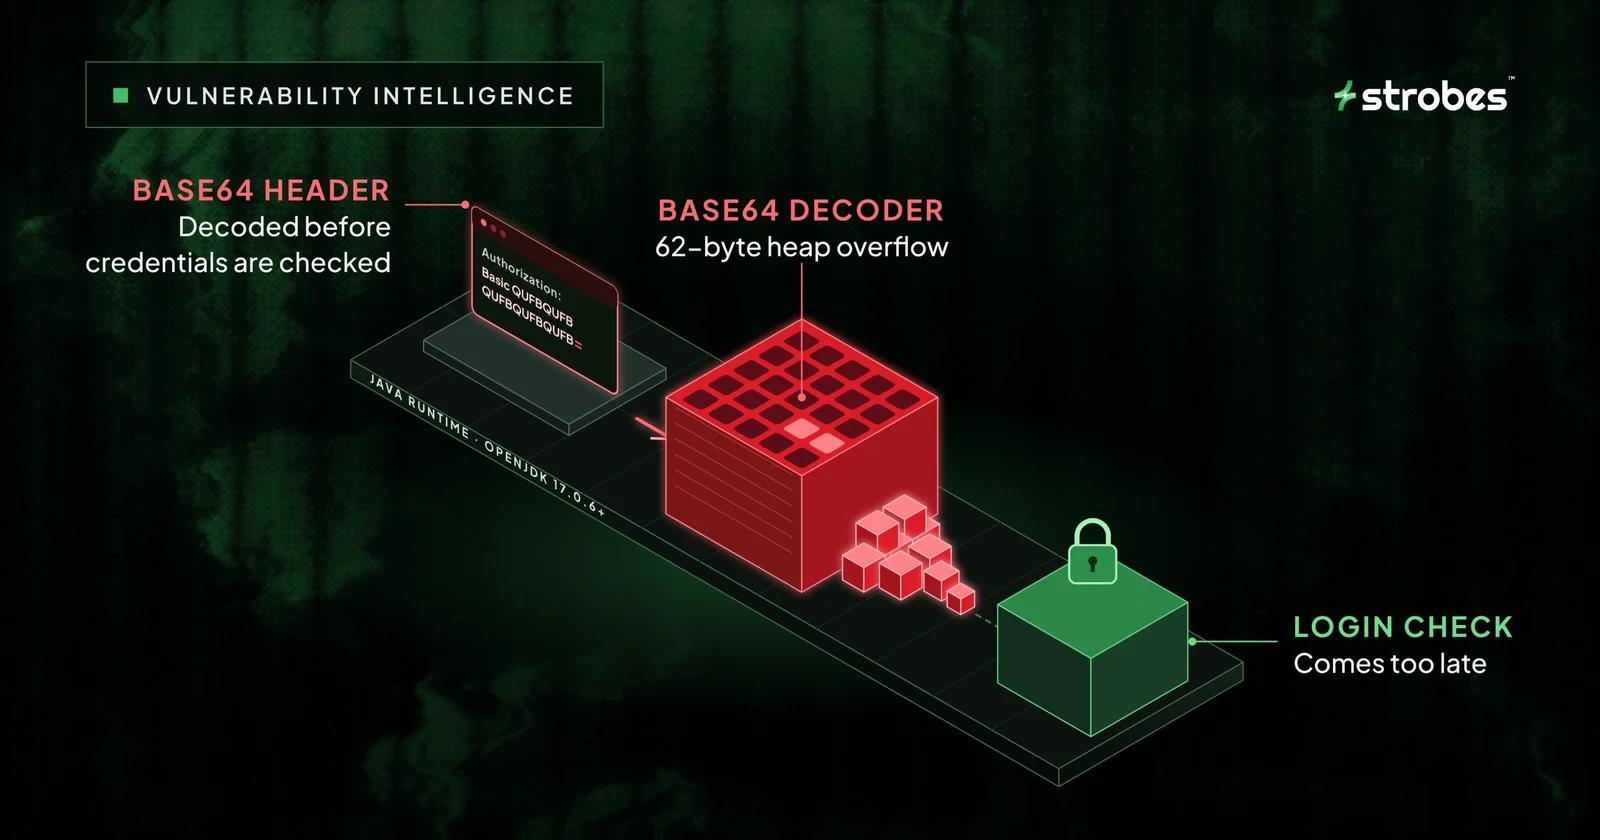
Java4Shell: Could a Base64 String Hijack Your Java Server?
Java4Shell (CVE-2026-114938) is a heap overflow in OpenJDK's built-in Base64 decoder that enables pre-auth RCE on AVX-512 VBMI servers. Affected builds, how to check, and how to fix it.
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
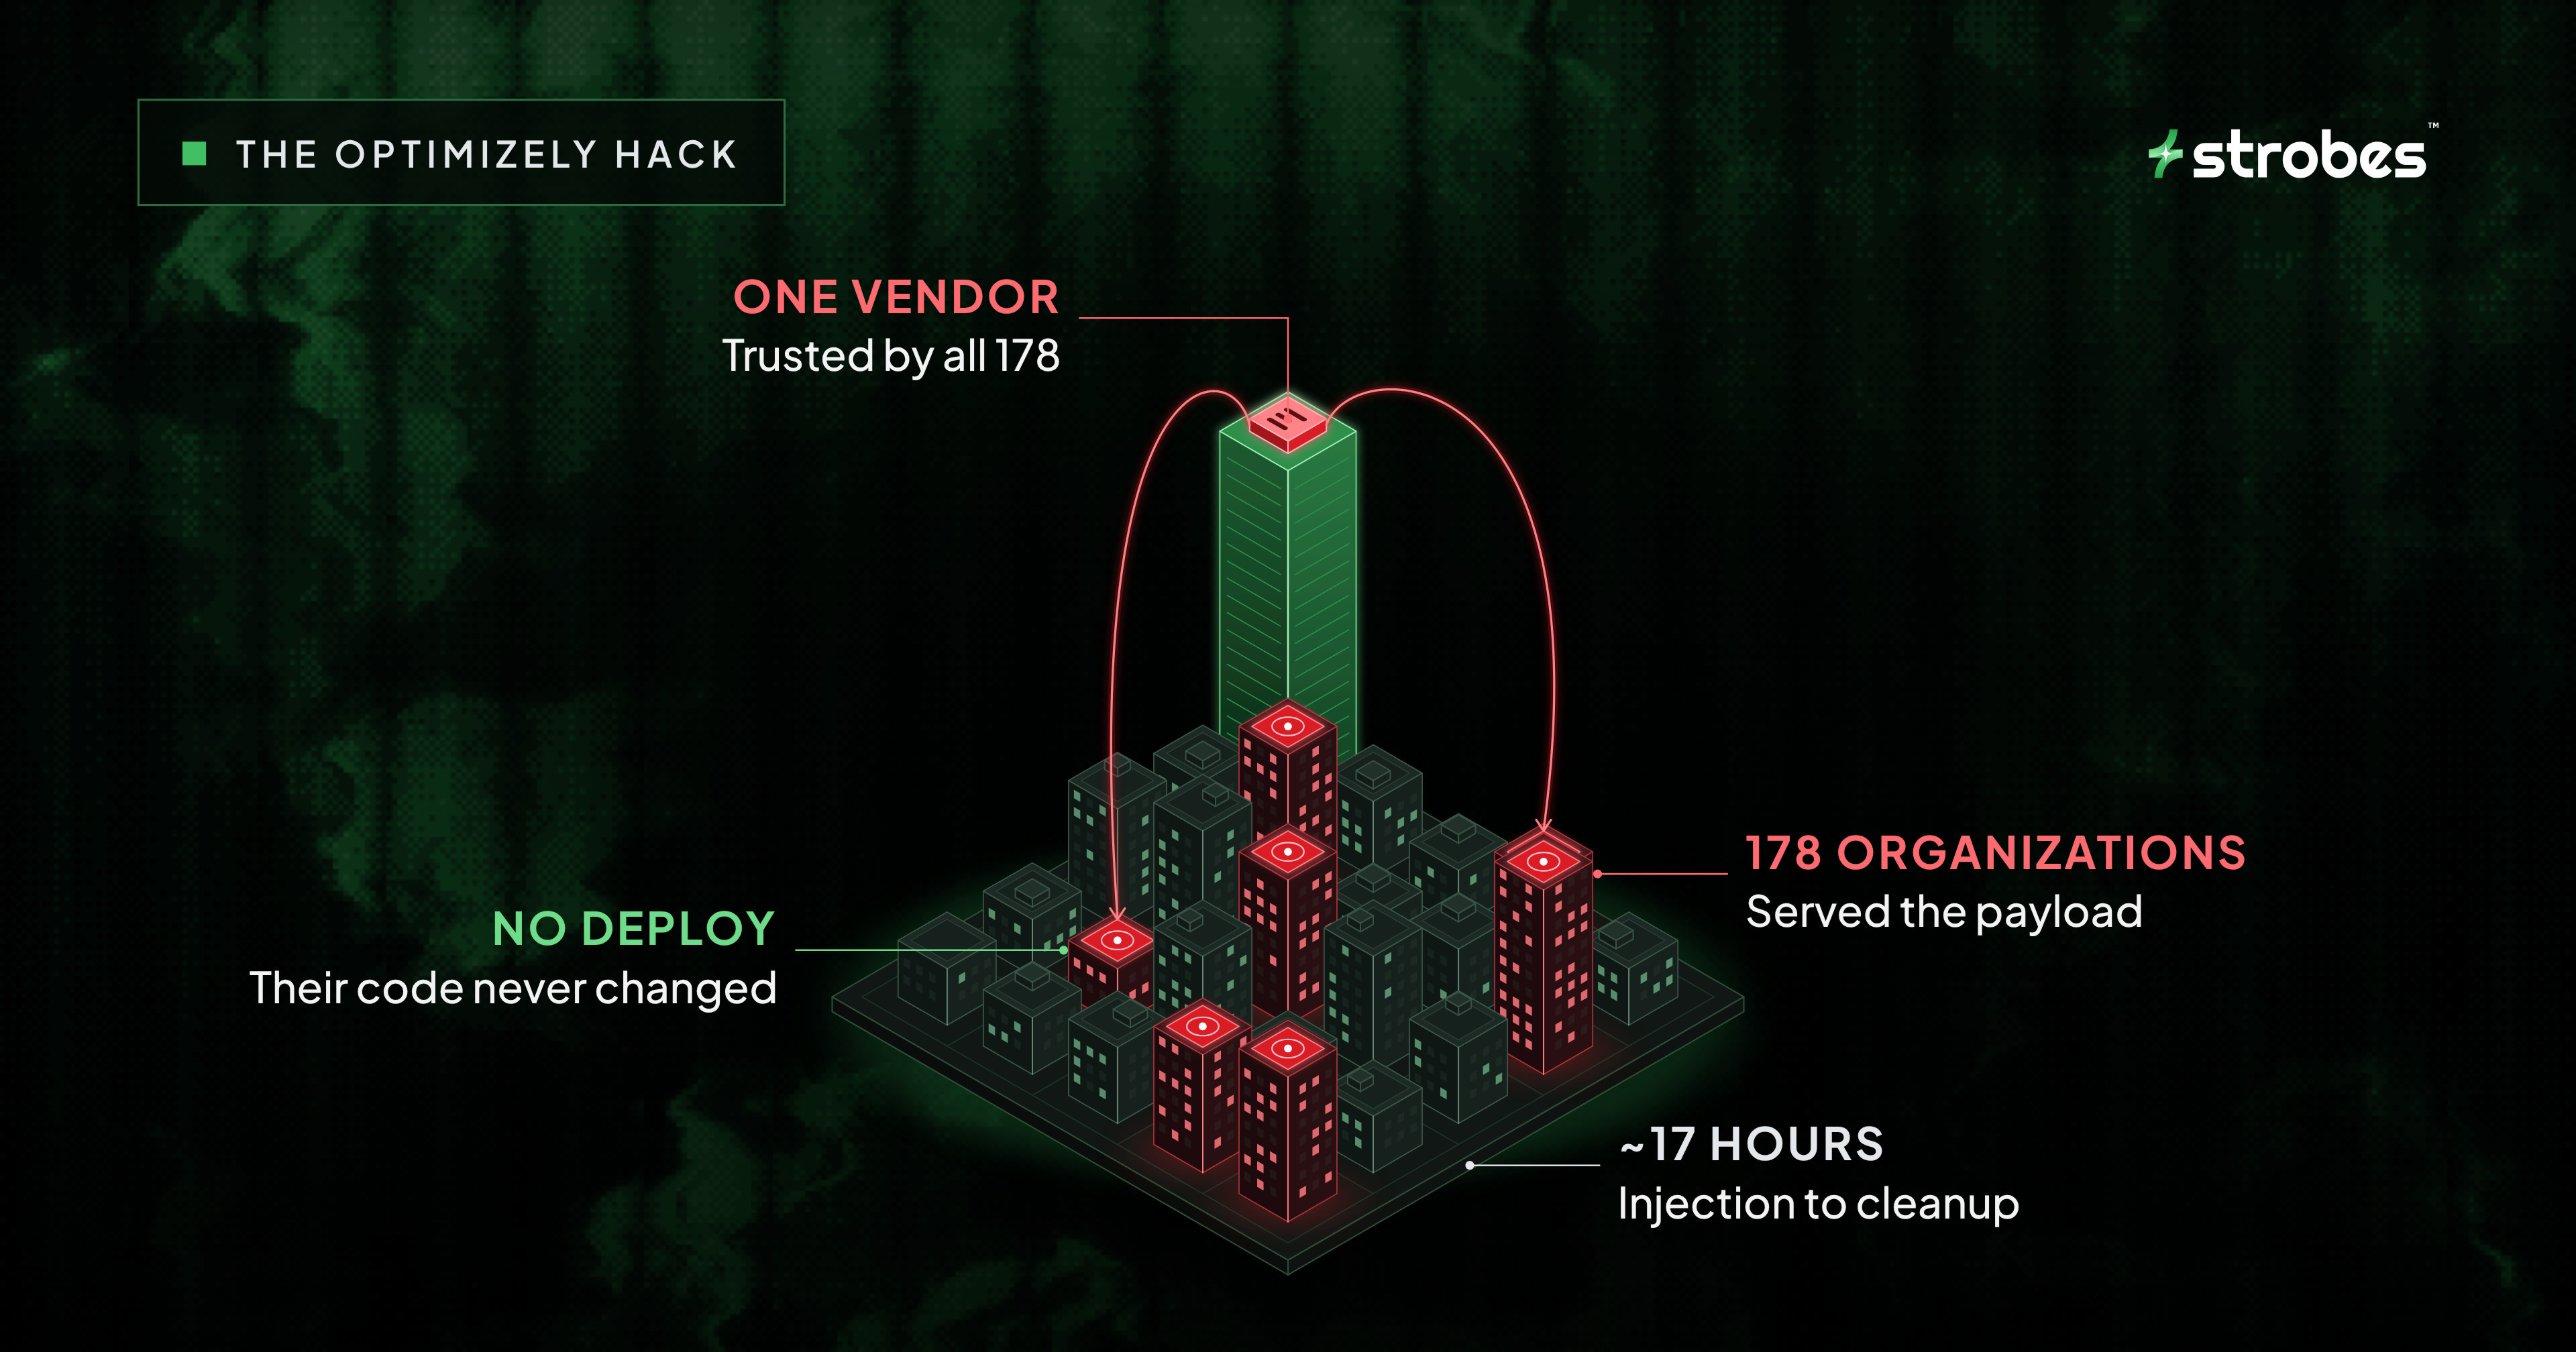
Optimizely hack hit 178 organizations without a single deploy
The Optimizely hack put malware on 178 organizations’ sites without a single deploy. See how it worked, what it targeted and what to check now.
Harnessing the Harness: Introducing AI Workflows
Why single-agent loops break on long offensive engagements, and how Strobes AI Workflows put a deterministic control plane around specialist agents: phases, work-queue tables, loops, gates and evidence-gated findings.
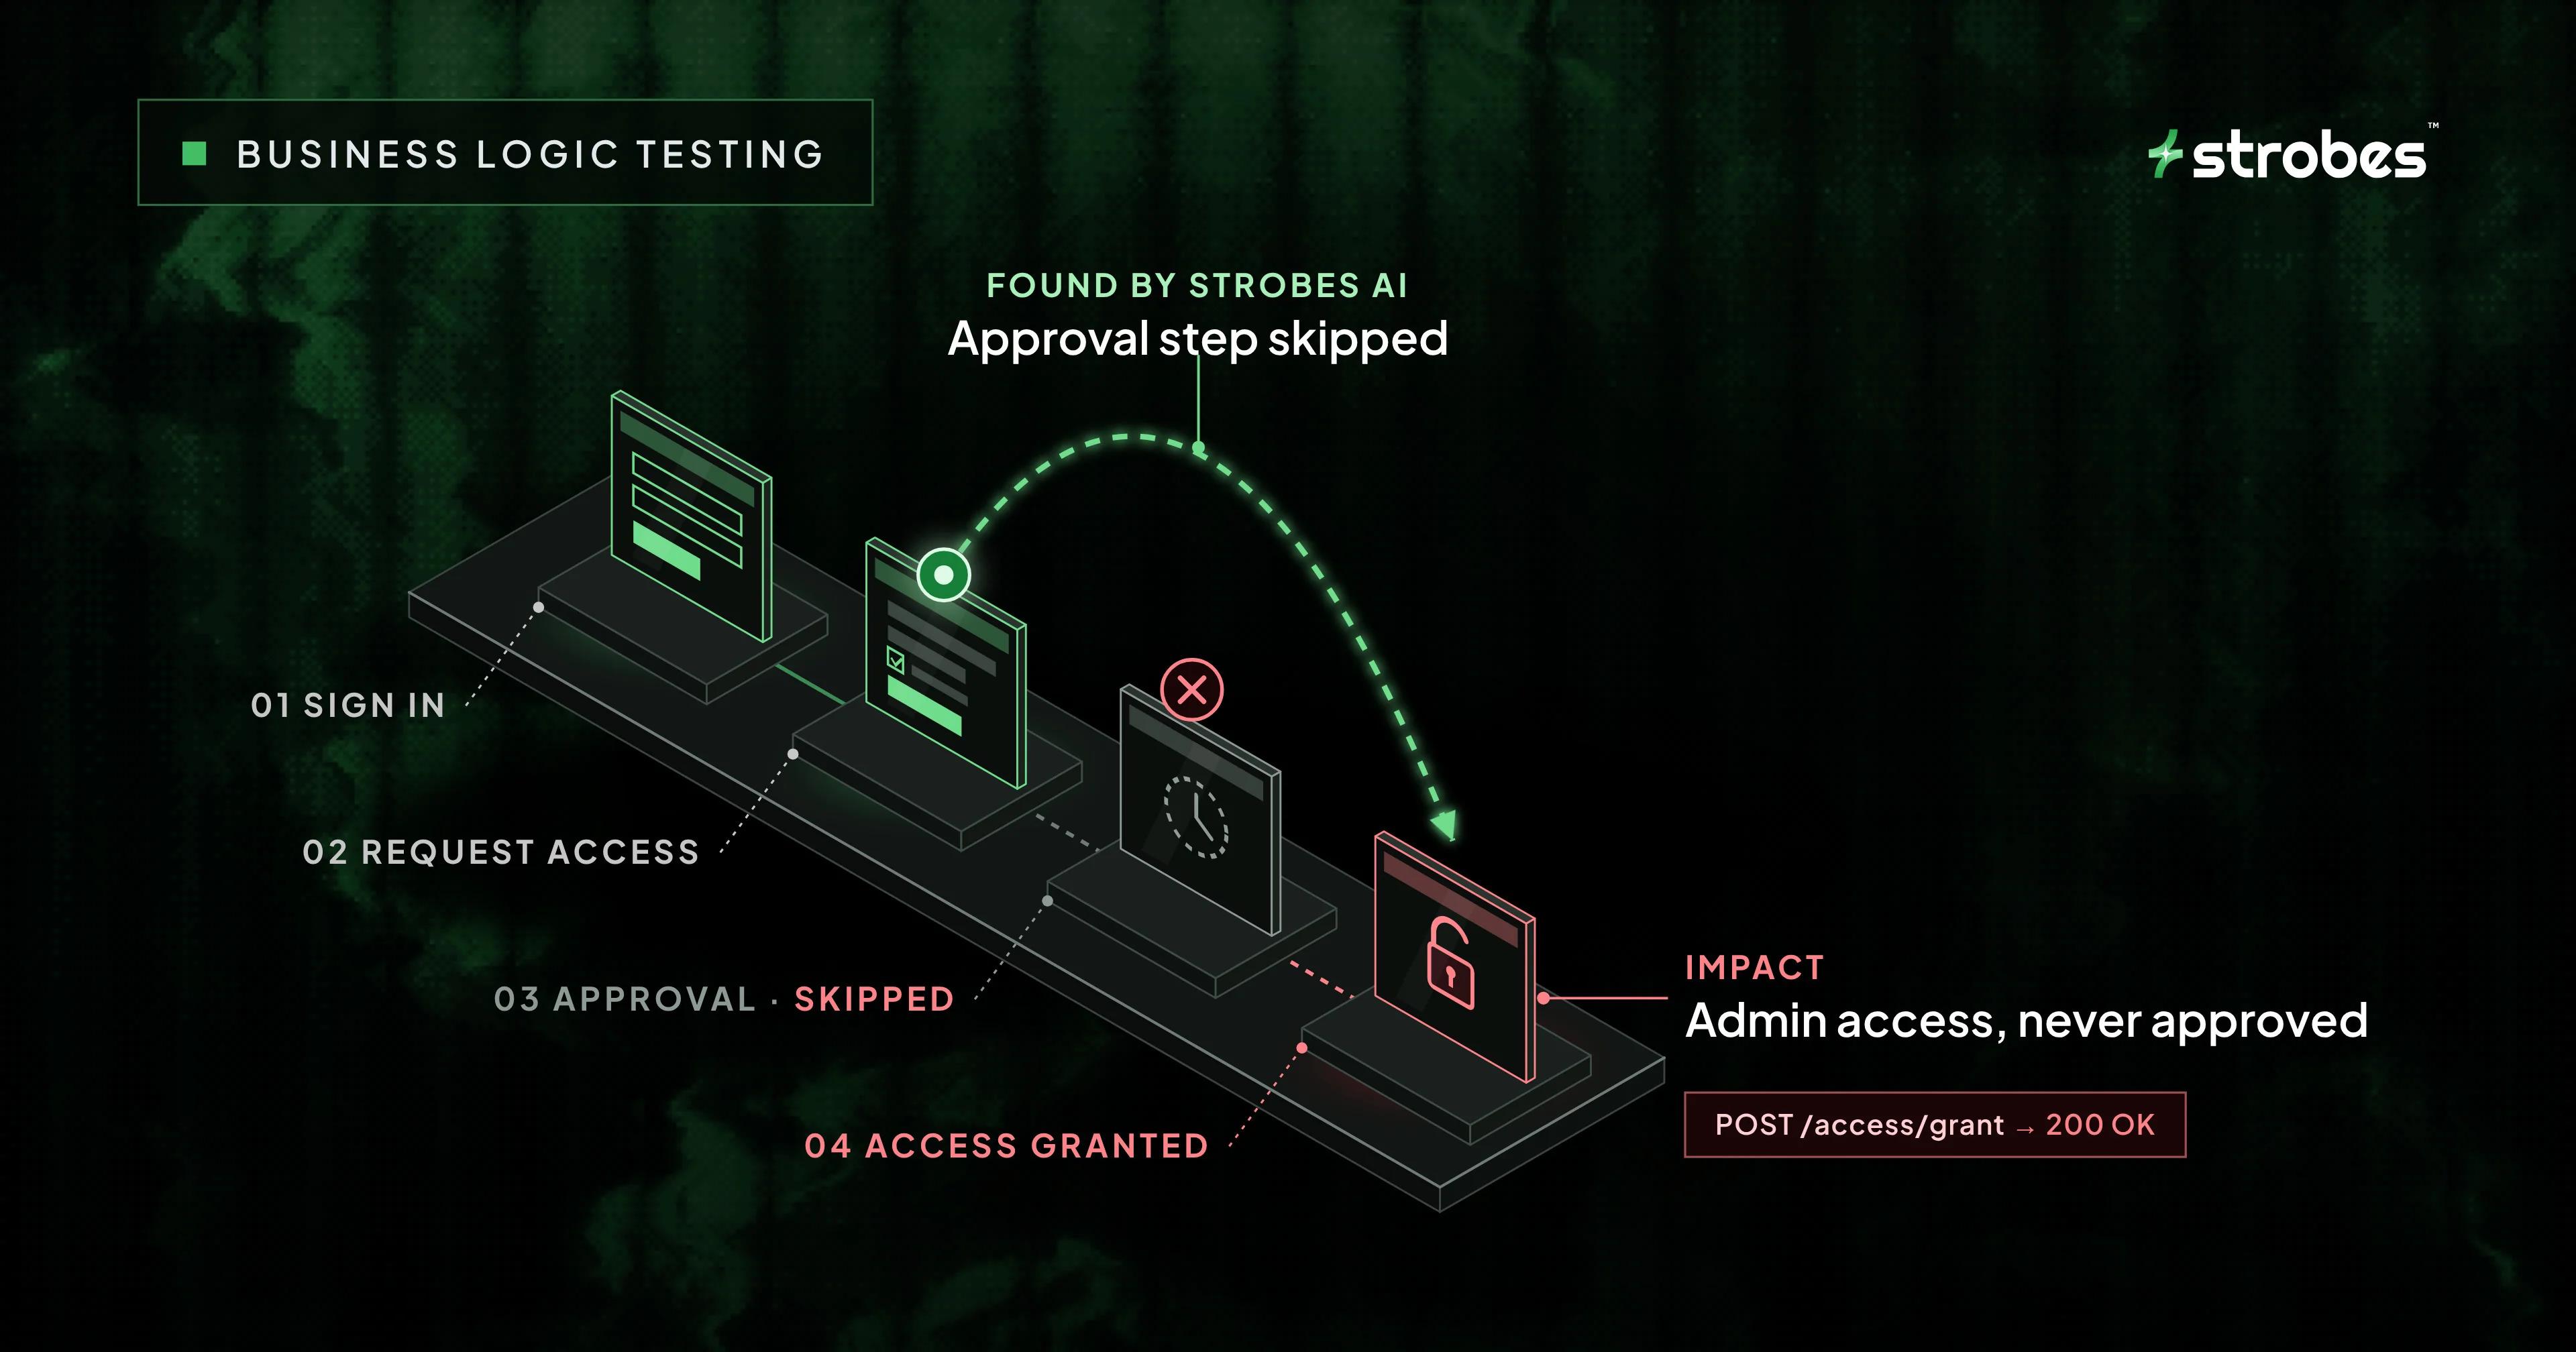
Can AI Pentesting Find Business Logic Flaws?
AI pentesting can find business logic flaws like IDOR, BOLA, and skipped workflow steps when it can test as more than one user. Here is what agents catch, what they need from you, and how to verify a vendor's claims.
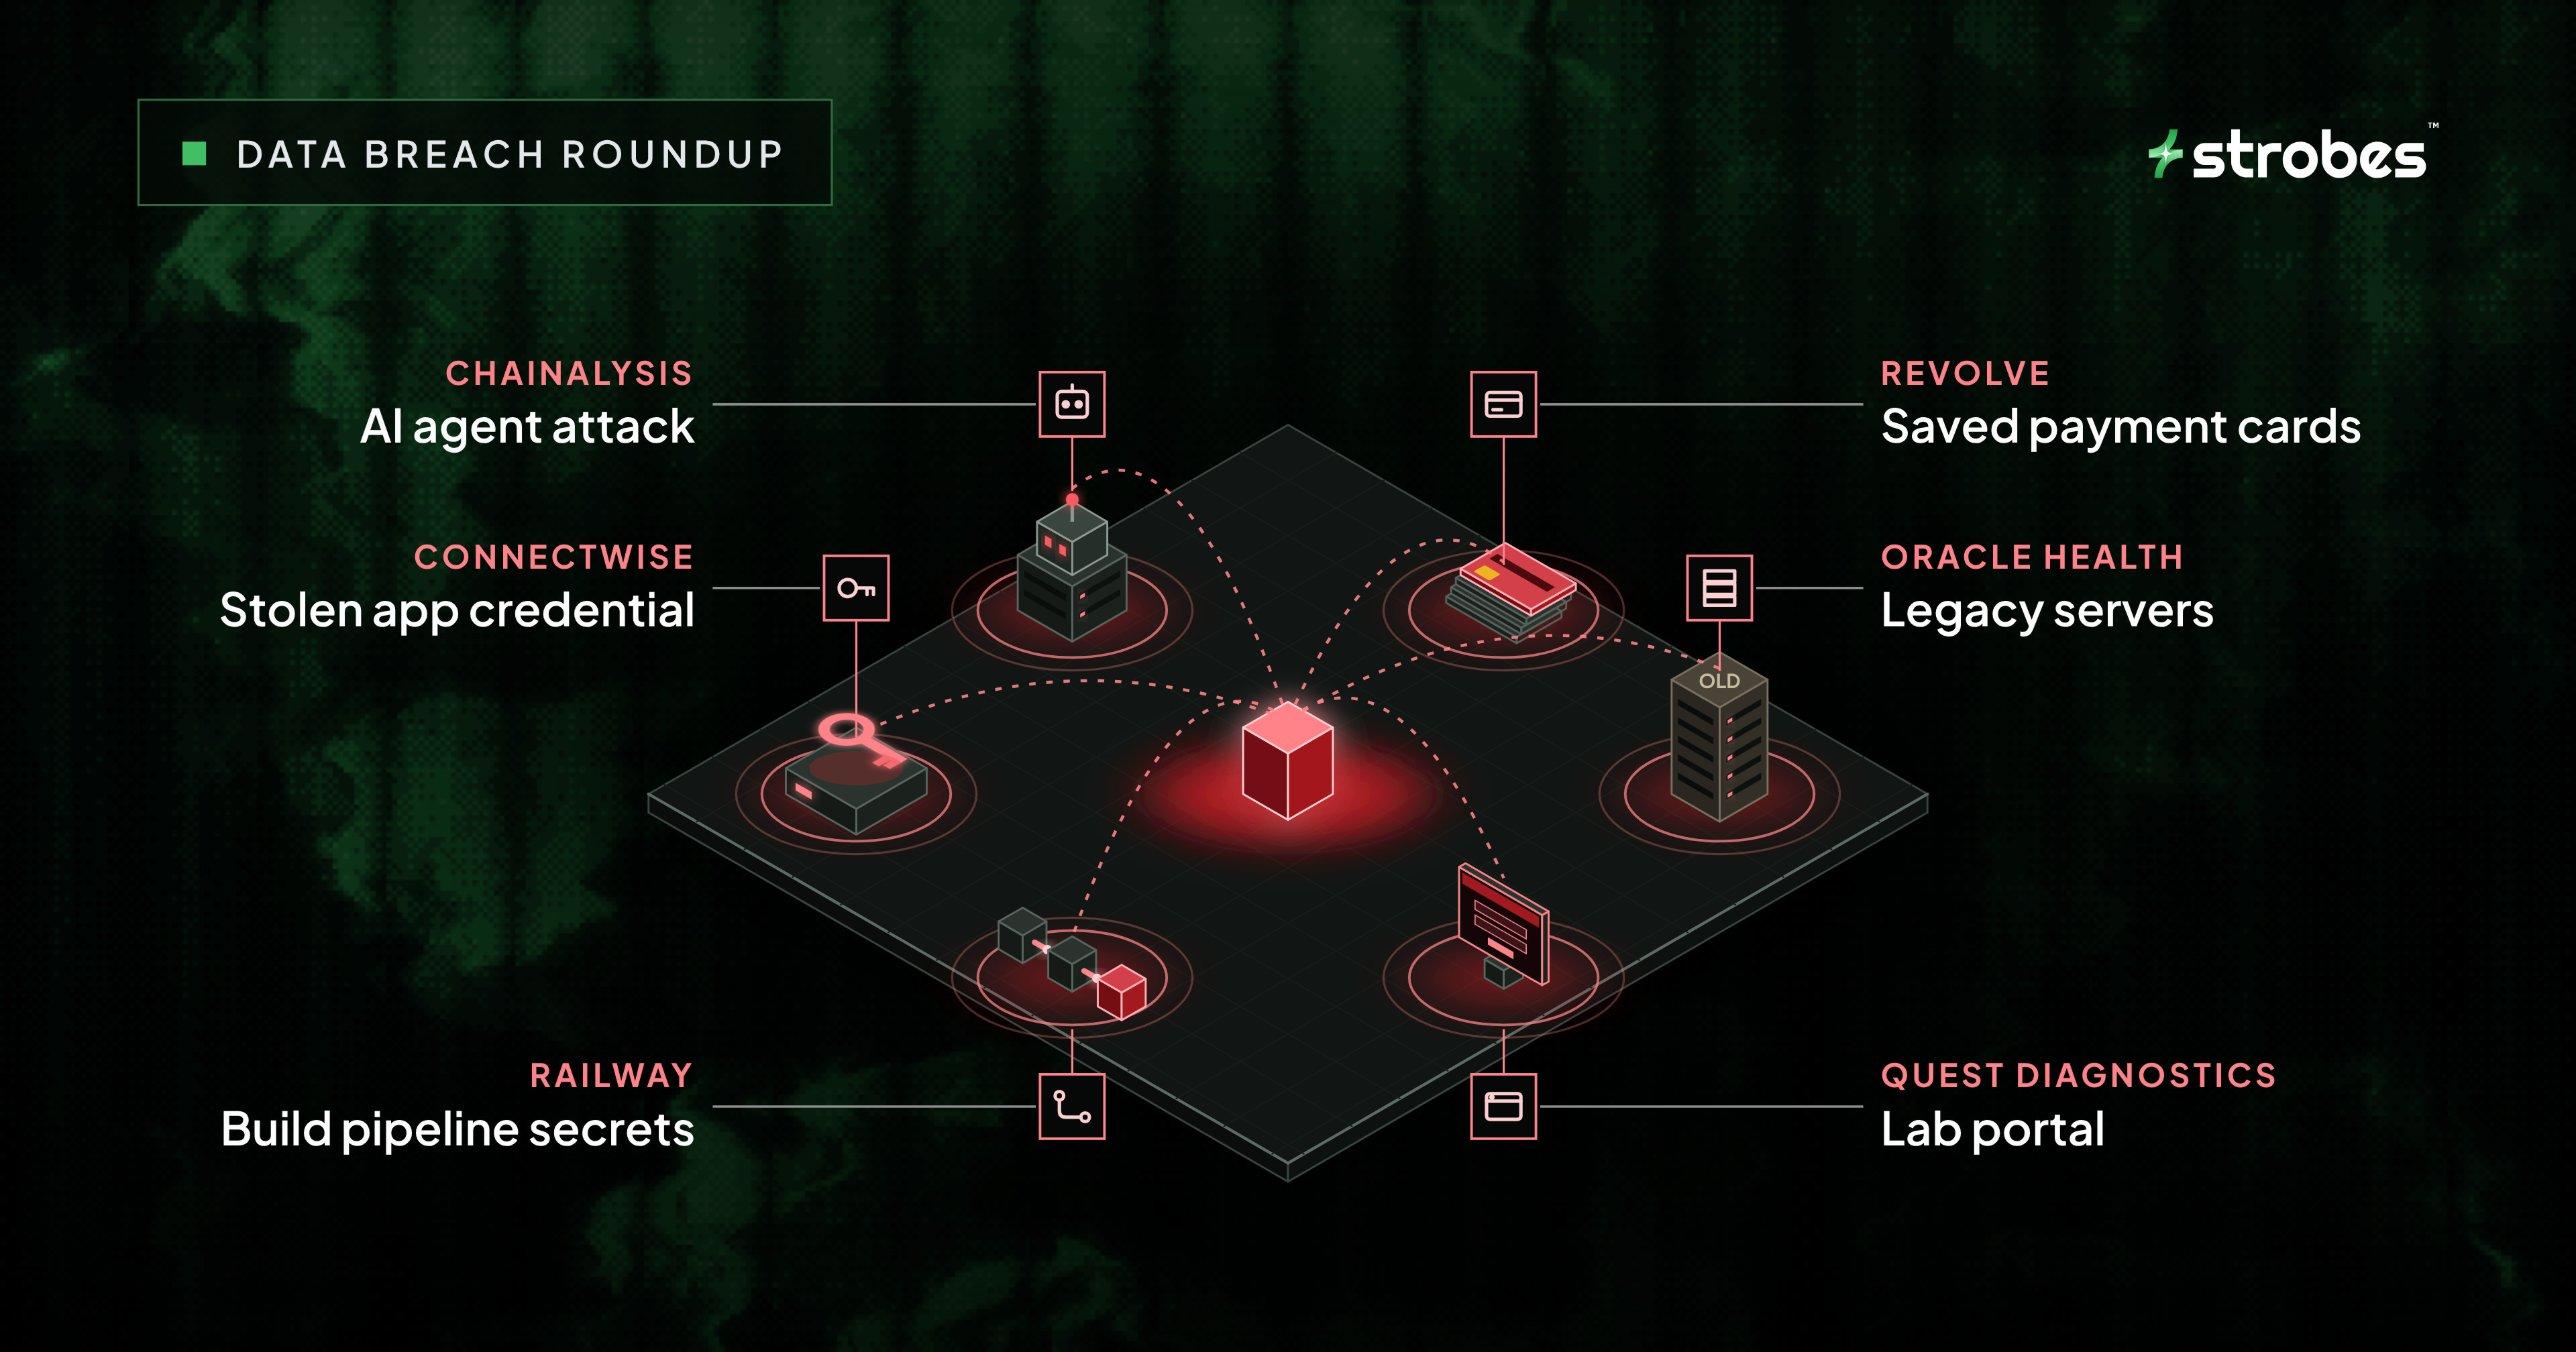
October 2026 Data Breaches and Lessons Learned
Chainalysis, ConnectWise, Oracle Health and 3 more US breaches from October 2026. What happened, what was exposed and what your team should test next.
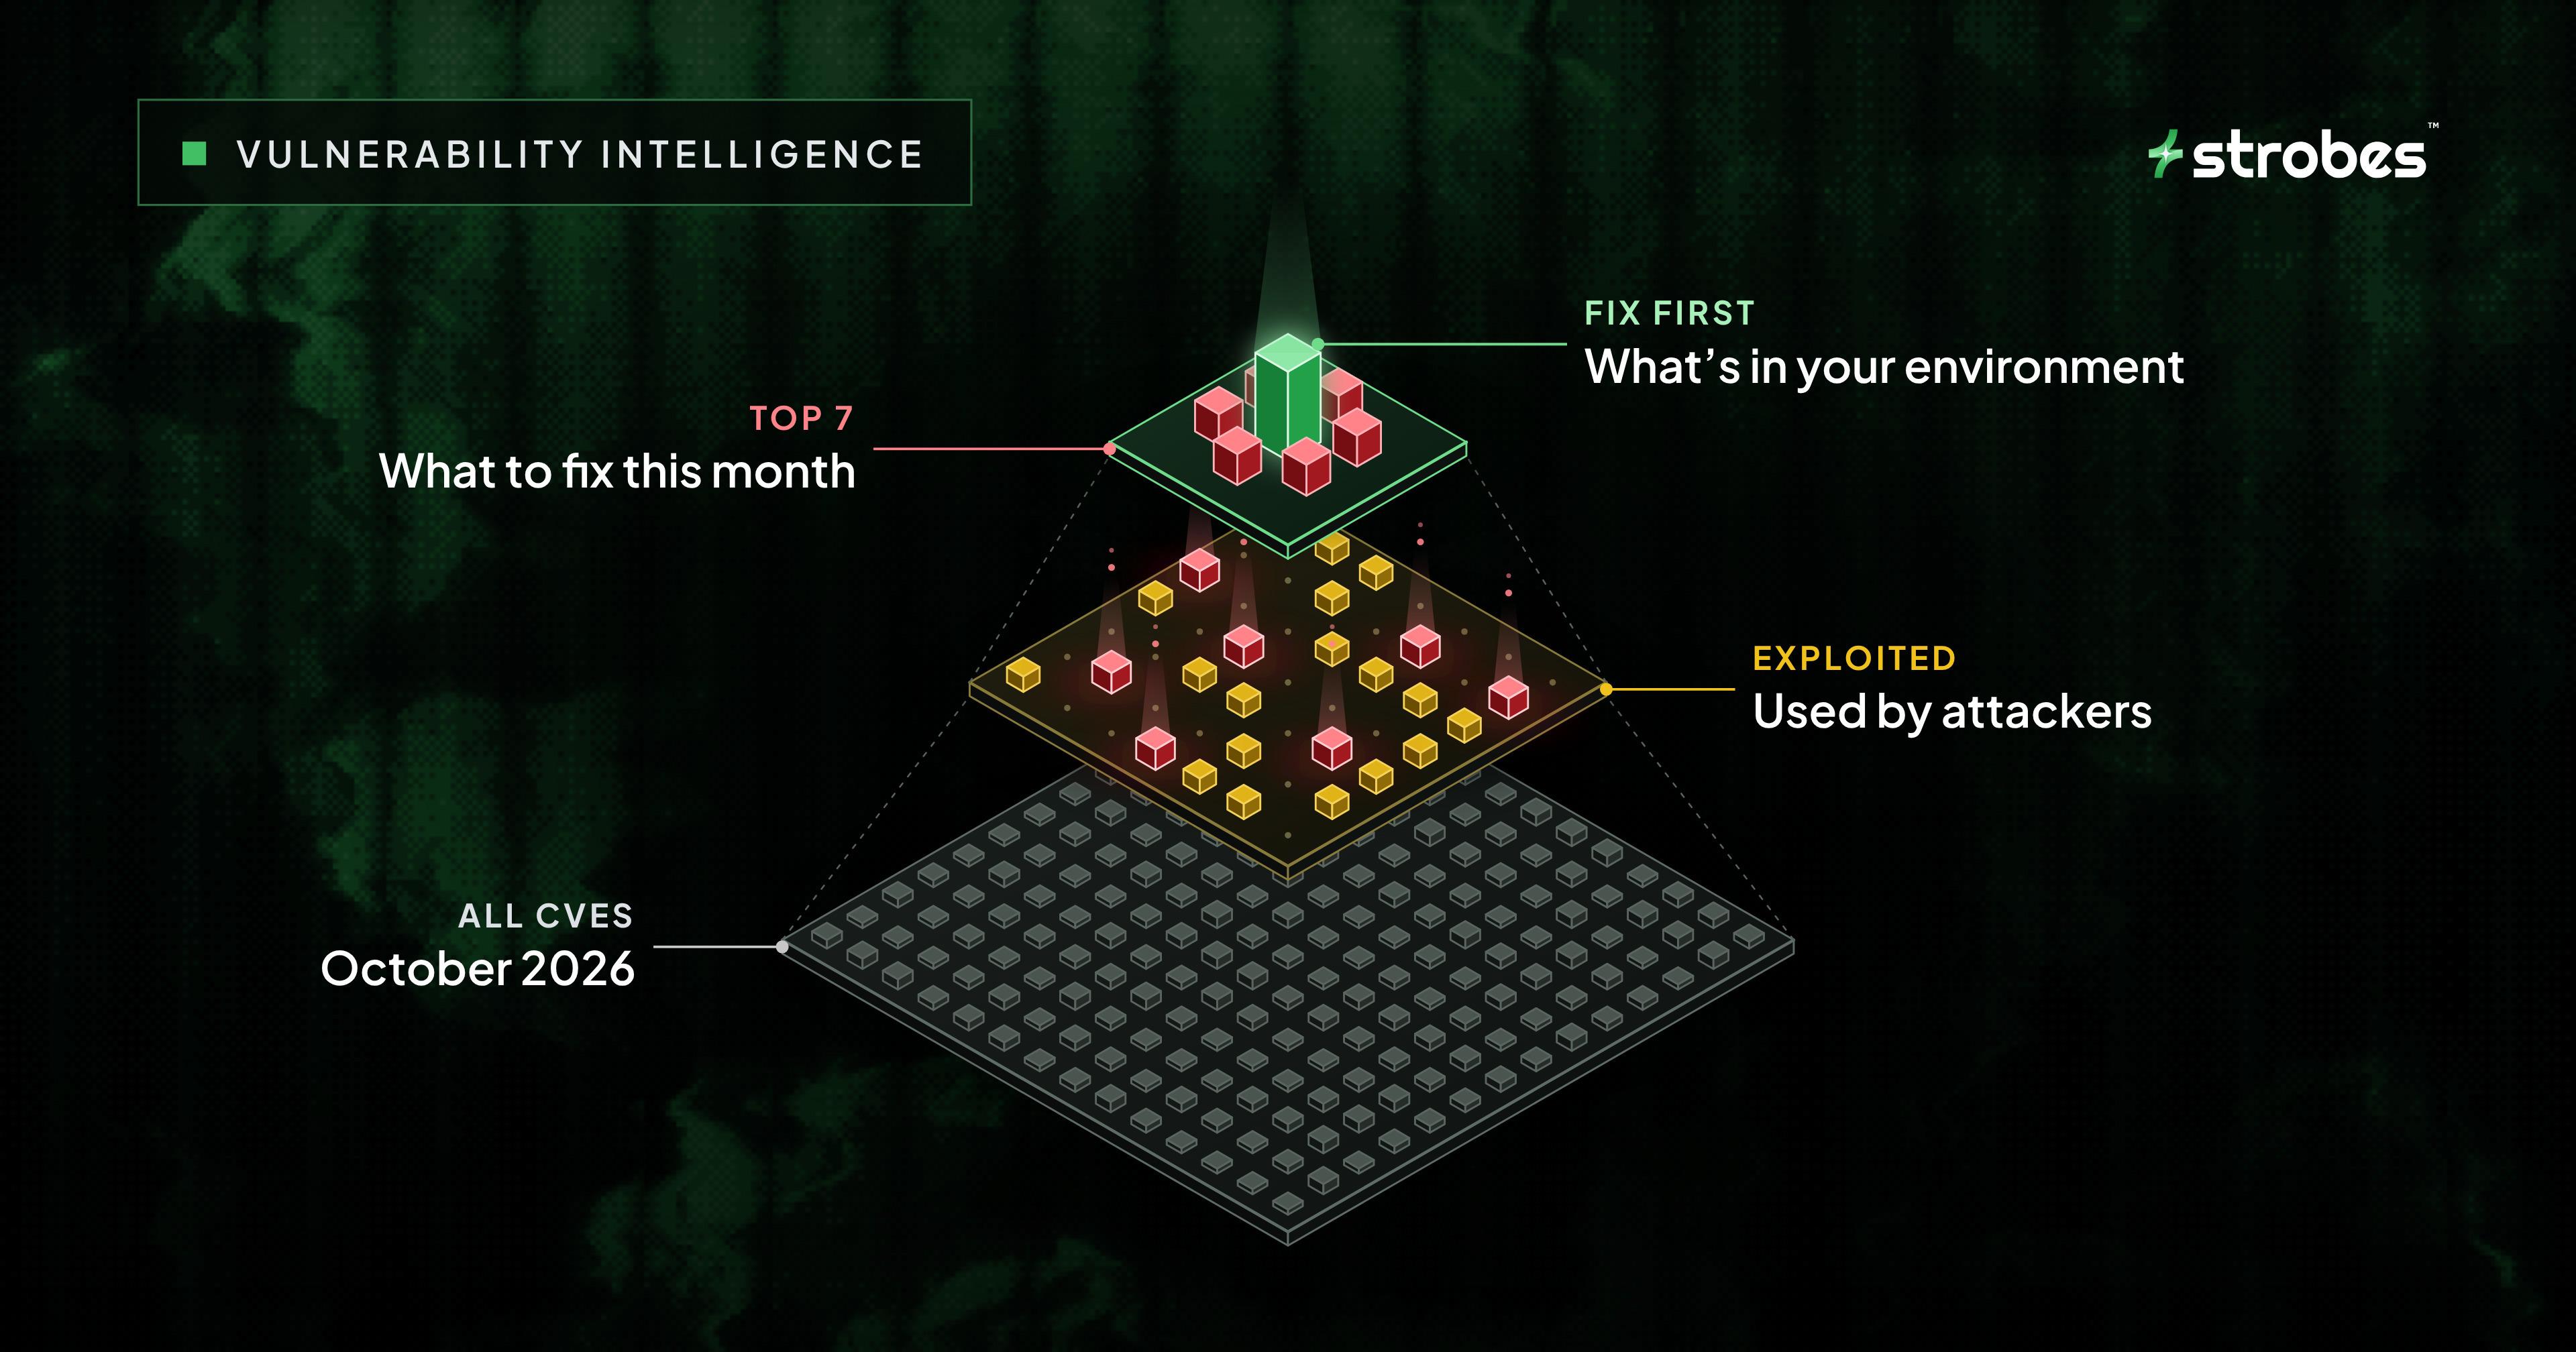
Top 7 CVEs of October 2026: What Attackers Used and What to Fix First
PHP2Shell, HTTP2Shell, Ivanti, BeyondTrust and three more October 2026 CVEs are under attack. See what each one does and how to patch it today.
Running DeepSeek V4.1 Flash in production: serving, KV caching and autoscaling on AWS
A technical guide to self-hosting DeepSeek V4.1 Flash for long-context agent workloads: vLLM configuration, a latency model for sizing, tiered and shared KV cache in S3, prefix-aware routing, autoscaling and unit costs.
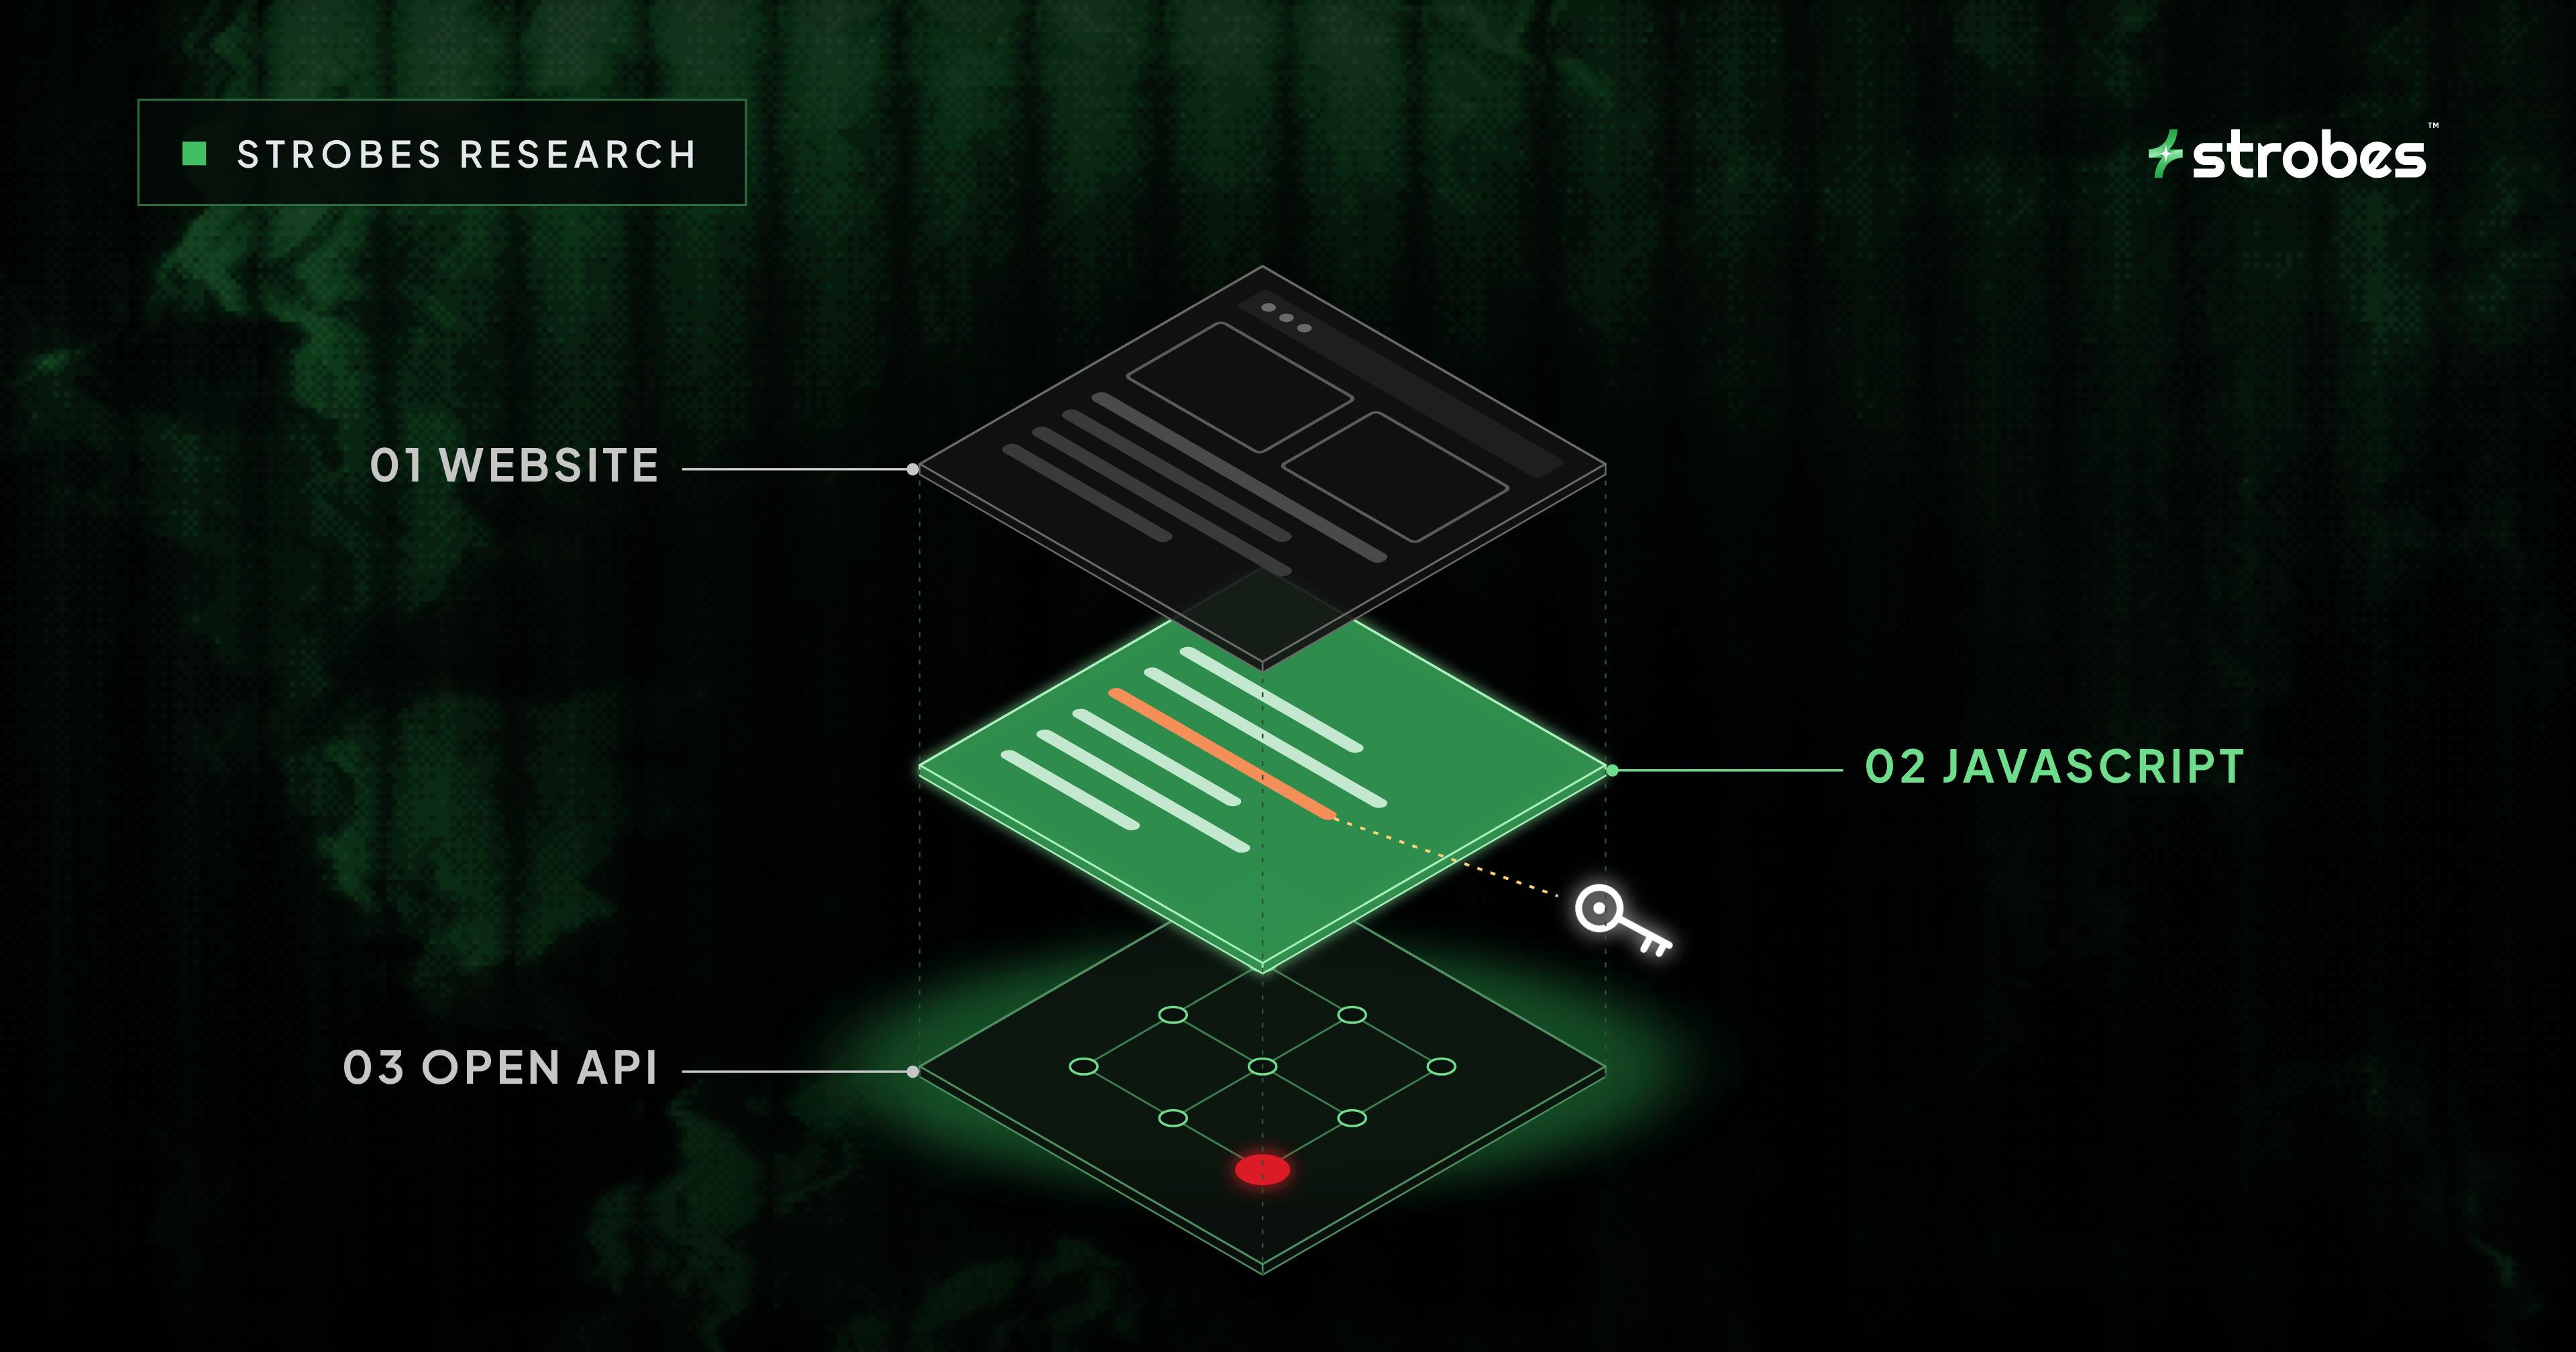
We Checked 286 Indian Companies. 4 in 5 Are One Bug Away From a Breach
We checked 286 Indian companies without logging in. 67% had exposed API keys or secrets in their JavaScript, and 81% had a serious flaw anyone could reach.
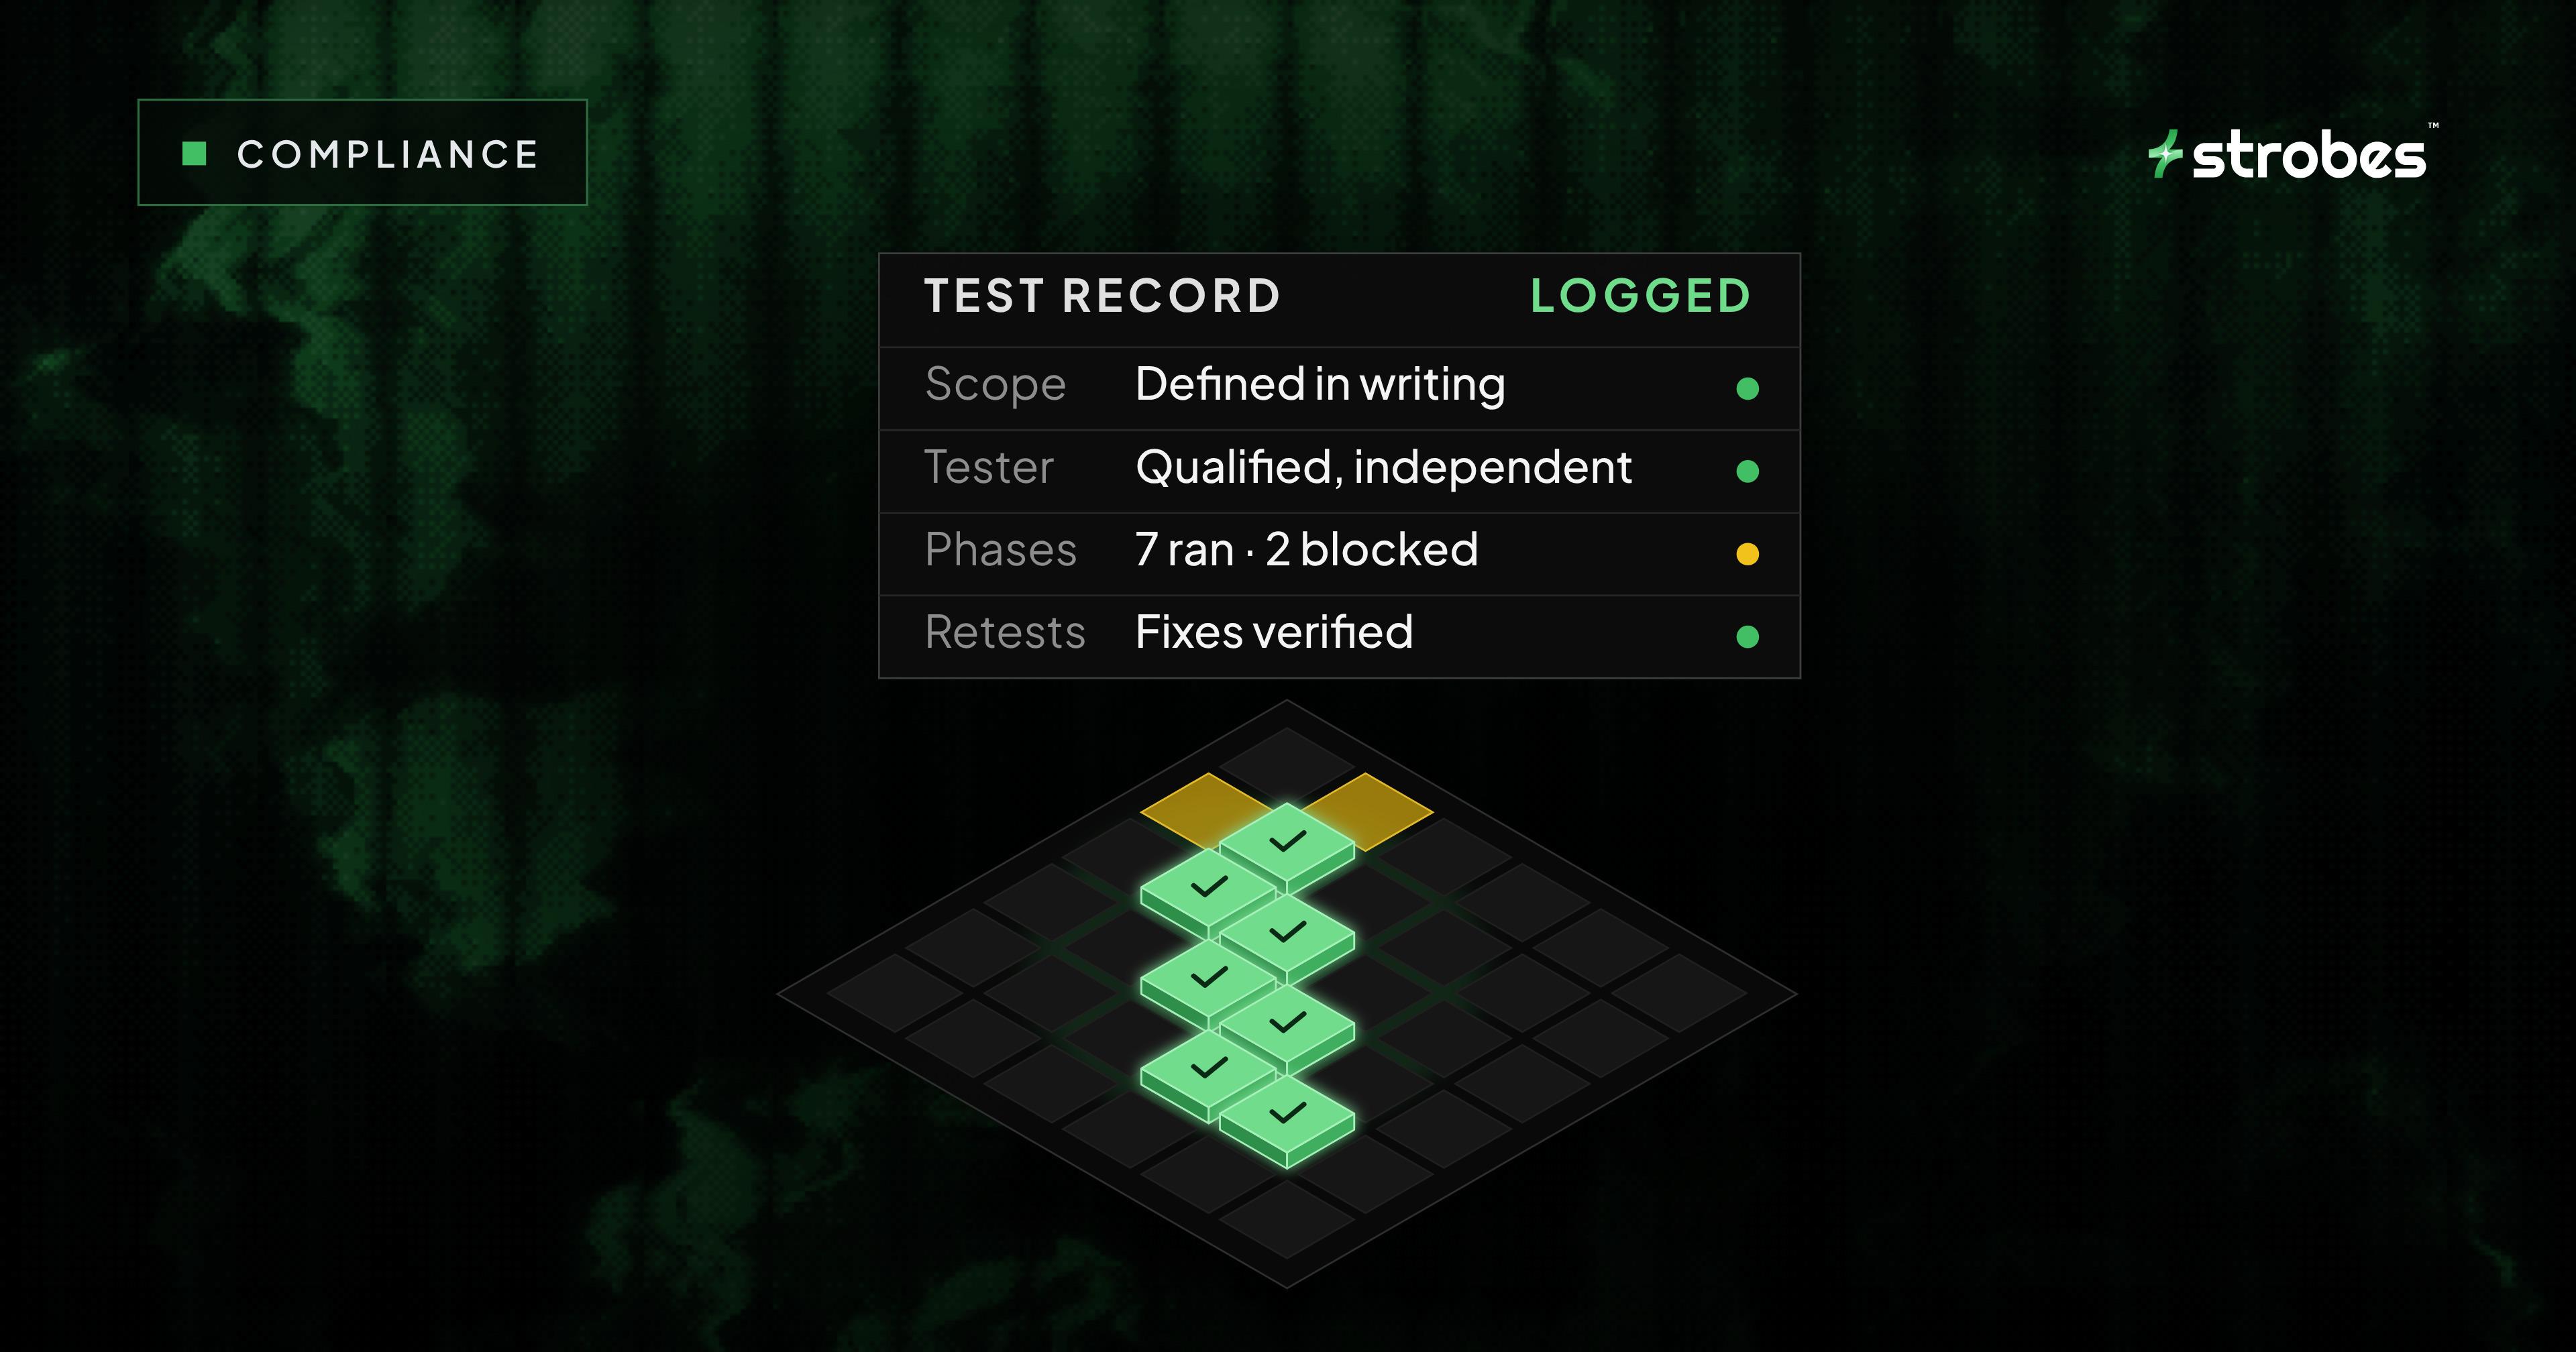
Best AI pentesting platforms for SOC 2 and PCI DSS compliance
Seven AI pentesting platforms compared on what SOC 2 and PCI DSS v4.0.1 actually ask for: scope, who tests, retests, and proof of what ran and what didn't.
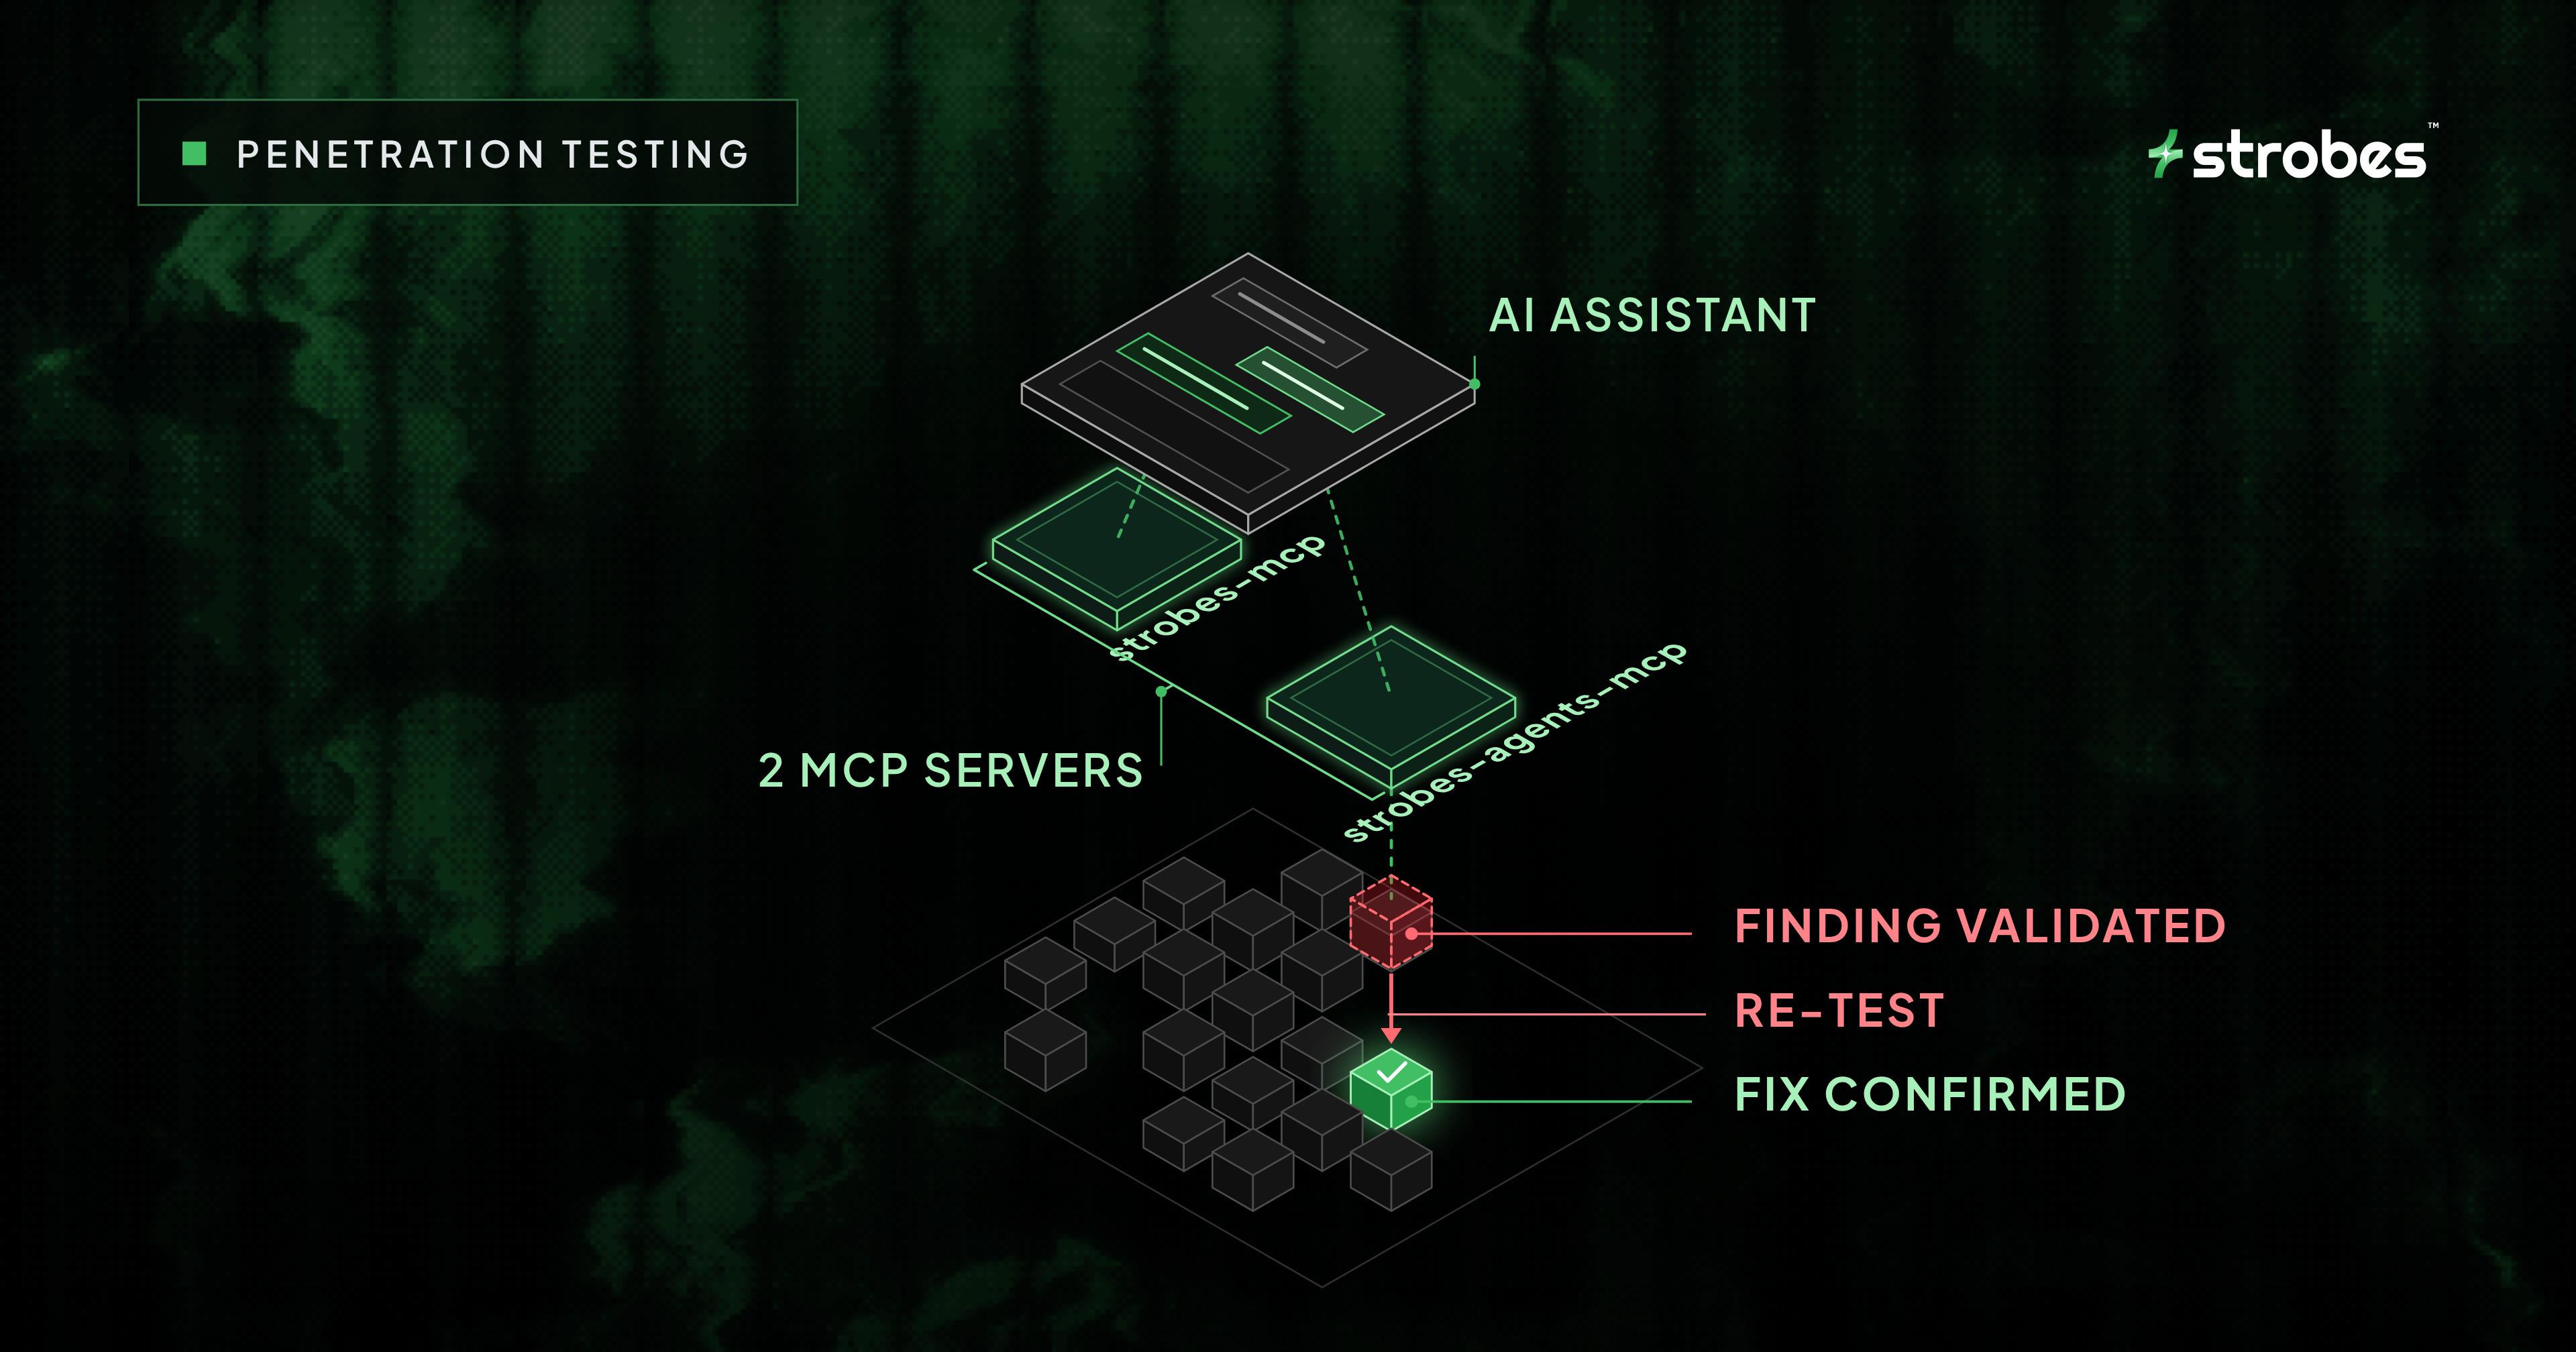
Run pentests from Claude Code with the Strobes MCP servers
Run agentic pentests, validate findings, and re-test fixes from Claude Code or any MCP app with the open-source Strobes MCP servers.
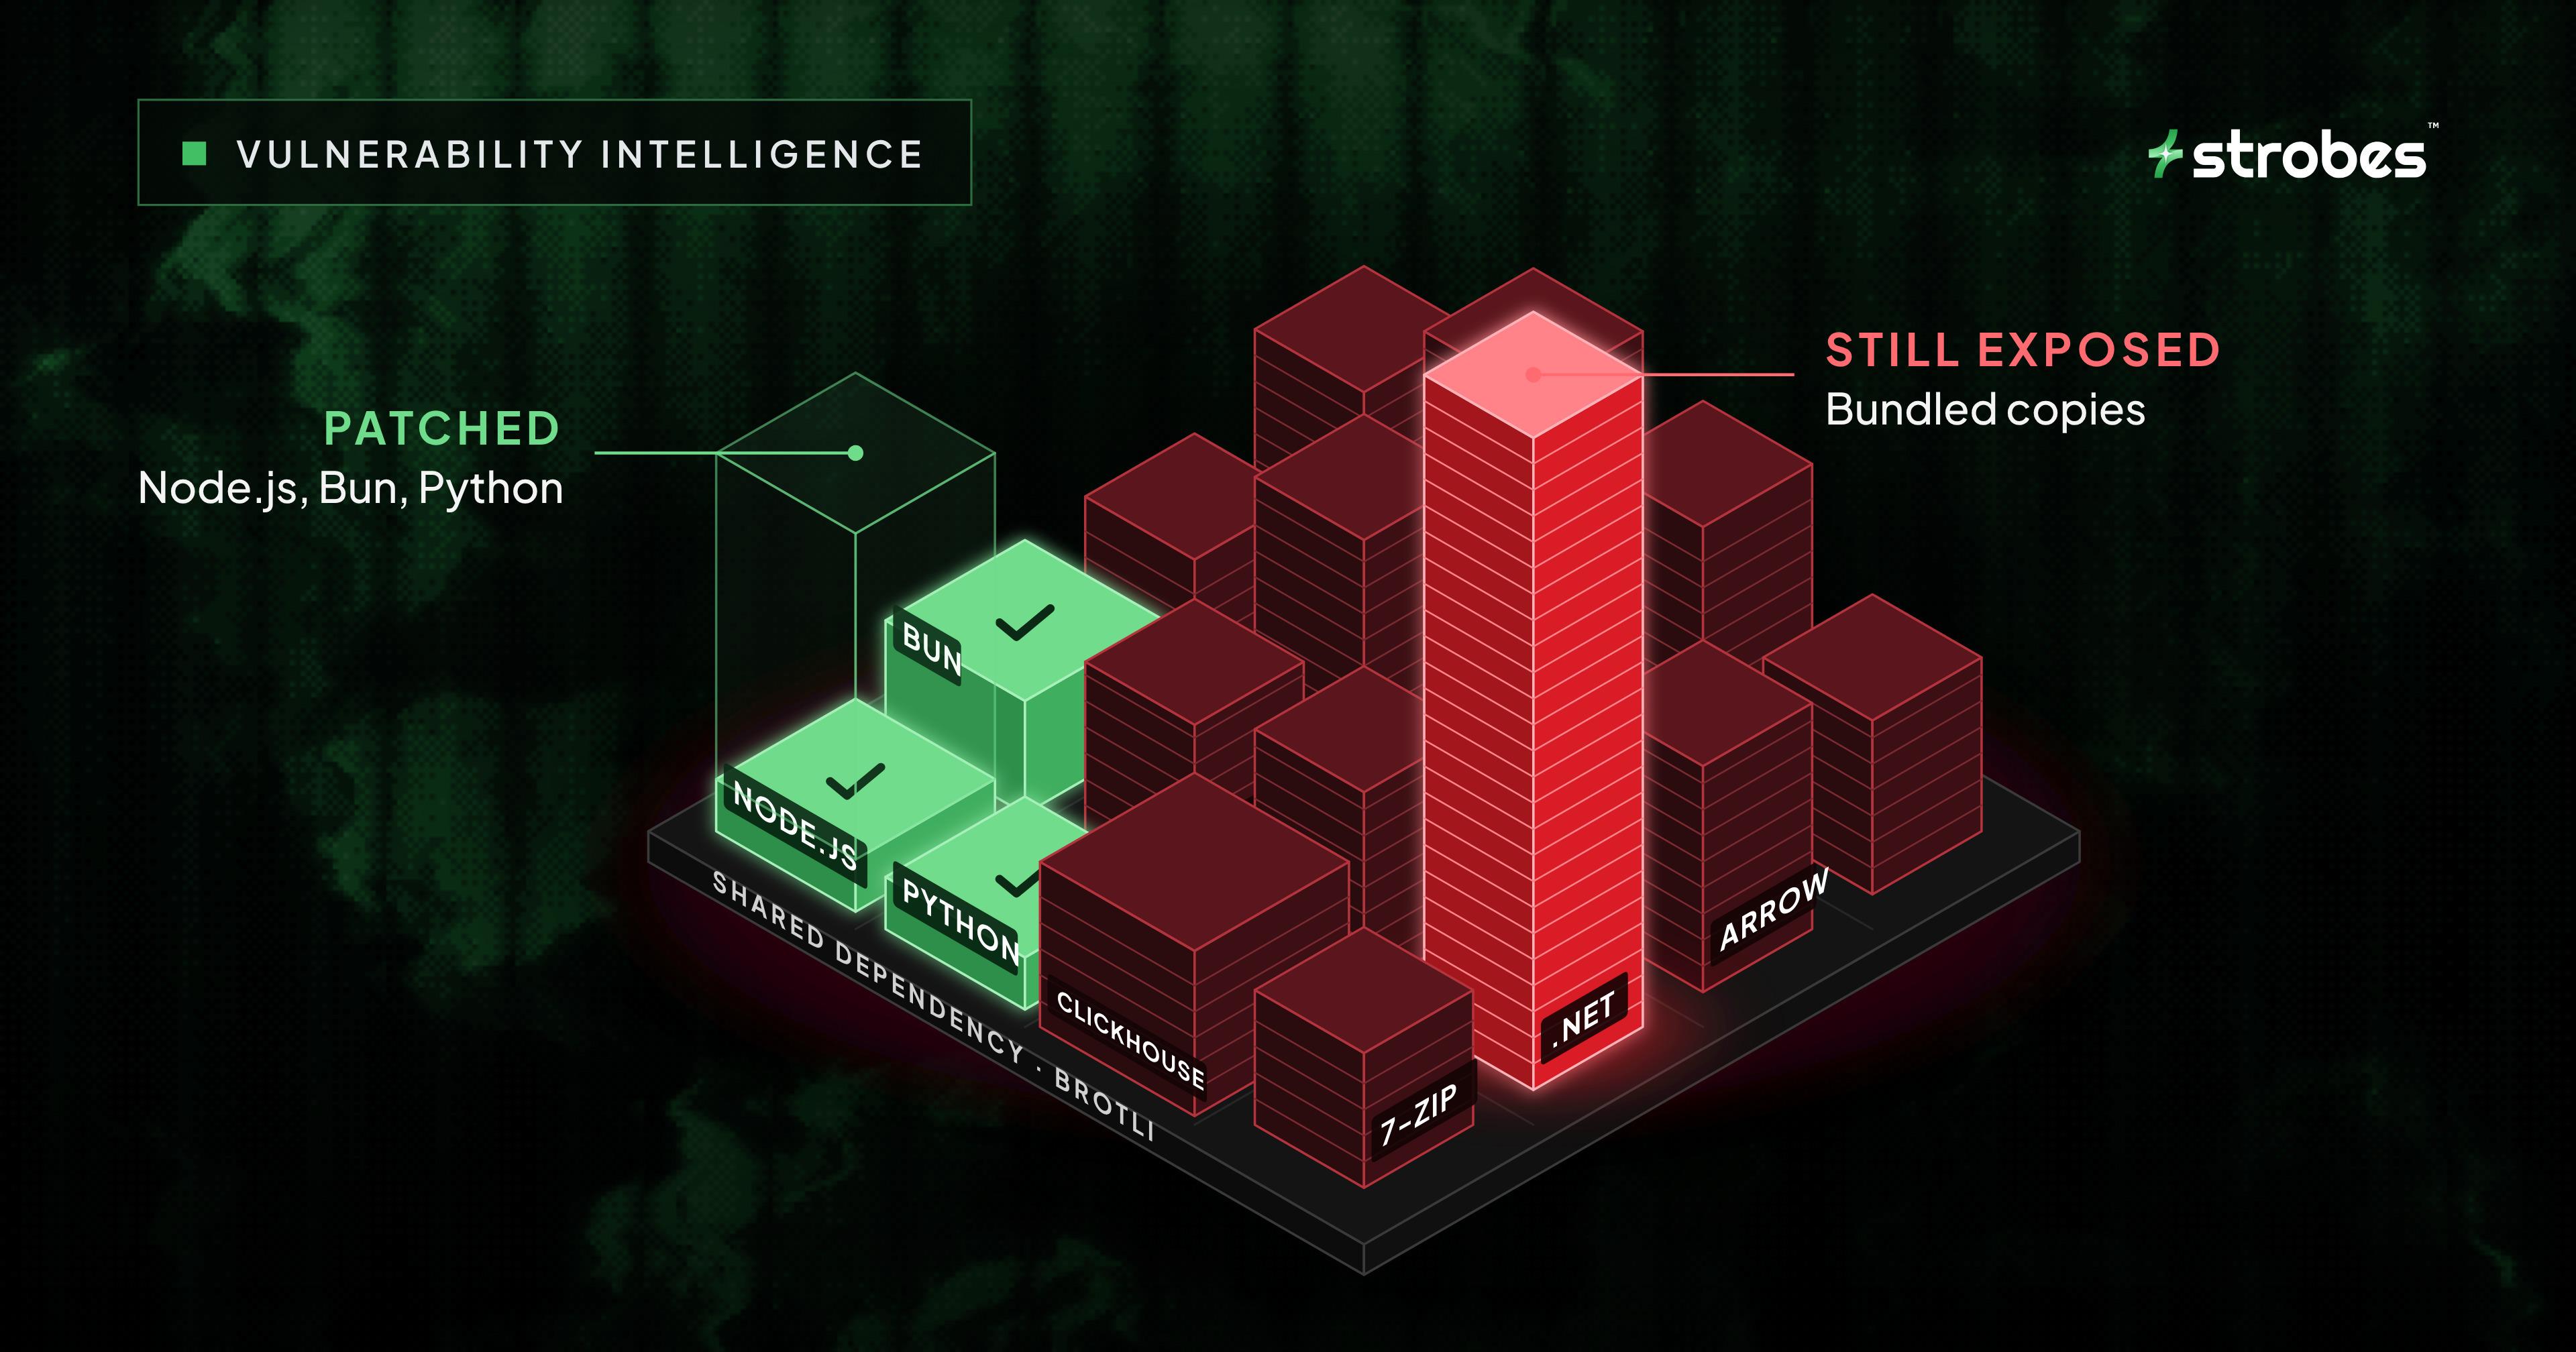
HTTP2Shell (CVE-2026-111497): The Brotli RCE Hitting Node.js, Python and More
HTTP2Shell (CVE-2026-111497), first called Node2Shell, is a Brotli decoder flaw that can lead to remote code execution in Node.js, Python, Bun and any app that decodes untrusted br content. Affected versions, exposure paths, checks and fixes.