
Manual pentesting vs AI pentesting: Which one do you need?
Updated November 2026
- ✓A manual pentest puts a human tester on your app for a week or two. It works well for custom business logic and for tests like PCI DSS that need a qualified tester.
- ✓AI pentesting, also called agentic pentesting, uses AI agents that log in, chain bugs together, and back up each confirmed finding with reproducible proof. It's fast enough to run on every release.
- ✓At Strobes, a small web app test costs $5,760 done manually and $3,500 to $5,000 with AI, depending on your credit rate.
- ✓PCI DSS requires a qualified tester, while SOC 2 doesn't require a pentest at all, so your compliance needs shape the mix.
- ✓Many teams run AI pentesting year-round and add a manual pentest for audits and big launches.
If you're choosing between a manual pentest and AI pentesting, you're really deciding how often your apps get checked and which bugs get caught along the way.
How often you test matters. Verizon's 2026 Data Breach Investigations Report (DBIR) found that exploiting vulnerabilities is now the number one way attackers break in, at 31% of the breaches studied. Every bug that goes unnoticed is one more way in.
A manual pentest puts a human expert on your app for a week or two. Over that time, they learn how your business works, which makes them great at spotting tricky issues in custom features like a new payment flow. Manual pentests are also a common pick for compliance checks like PCI DSS, SOC 2, and ISO 27001, and PCI DSS goes a step further by asking for a qualified tester to own the work. Teams usually book them once or twice a year, and more often for high-risk apps.
AI pentesting, also called agentic pentesting, uses AI agents that poke at your software just like a real hacker would. They log in, swap user IDs to test access controls, link small bugs together into bigger attacks, and back up every confirmed finding with proof you can reproduce. Since these agents run fast, you can test every release as soon as it ships.
At Strobes, we offer both. Many of our customers run AI pentesting across all their apps year-round, then add a manual pentest when an audit or a big launch calls for one. Below, we'll show you where each one fits and how much it costs, so you can build the right mix for your team.
How do manual pentests and AI pentesting compare?
Here's how they stack up side by side.
| Manual pentest | AI pentesting | |
|---|---|---|
| Who does the testing | A human tester | AI agents, with you approving high-risk steps |
| Time to results | One to two weeks | Usually hours, depending on scope |
| How often you test | Usually once or twice a year, mostly because of cost | Every release or on a schedule |
| Business logic | A tester works through your workflows using your business rules and team input | An agent works through your workflows using the business rules, test accounts, and context you give it |
| Chaining bugs | Yes | Yes |
| Evidence | Steps to reproduce and proof of impact | Saved request and response, plus proof you can rerun |
| Retesting | Booked with the tester | Rerun on demand |
| Compliance | Common for PCI DSS, SOC 2, and ISO 27001 | Can support SOC 2 and ISO 27001 evidence, check with your auditor |
| CI/CD fit | Low | High |
| Small web app at Strobes | $5,760 | $3,500 to $5,000 |
What is a manual pentest?
A manual pentest, also called manual penetration testing, is a security test where a skilled human tester attacks your app, network, or cloud setup the way a real attacker would, then shows you what they got into and how to fix it. Many companies buy them through Pentesting as a Service (PTaaS), which lets you book the test, track findings, and request retests on one platform, so you're not chasing PDFs and email threads with a consulting firm.
Manual pentests tend to follow the same basic steps, based on standards like PTES and the OWASP Web Security Testing Guide.
-
Scoping, where you and the tester agree on what's in bounds and how deep to go
-
Recon and discovery, where they map your attack surface with tools like nmap and Burp Suite
-
Exploitation, the main event, where they try to break in and chain small issues into bigger ones
-
Reporting, with proof, a severity rating, and fix steps for every finding
-
Retesting to confirm your fixes actually worked
The real value comes from the exploitation step. Scanners point the tester toward weak spots, and the tester decides what to try next based on how your business works. Say your app lets a regular user approve their own refund request. The request looks perfectly normal, so spotting the problem means knowing how the refund process is supposed to work. You can see how Strobes testers handle this in our web app pentest methodology.
That depth comes with a few trade-offs. A manual pentest checks your app as it was during the test window, so code you ship afterward isn't covered until the next one. Results also depend on who does the work, which is why it's worth asking about tester certifications like OSCP or OSWE before you book. For a step-by-step look at each stage, see our guide to penetration testing phases.
What is AI pentesting?
In this post, AI pentesting means AI agents that pick and run their own testing steps based on what they find, then back up each confirmed finding with reproducible proof, like a working exploit for an app bug. A person still sets the scope, the permissions, and the approval rules. Some tools sold as "AI pentesting" only help a human tester instead, so it's worth asking which kind you're buying.
Here's what that looks like on a real app. The agent logs in as User A and notes the invoice IDs it can see. Then it logs in as User B and asks for one of User A's invoices. If the app hands it over, the agent saves the exact request and response as proof, then checks whether that access leads to anything bigger.
To get the most out of it, give the agent a test account for each user role and a clear scope. You can run these tests on a schedule or on every release, and our agentic pentesting guide walks through the full process.
Is AI pentesting safe to run in production?
Yes. What you can safely test depends on the system and how much risk your team can accept, so set the scope, exclusions, request limits, and approval rules before you start. Having a person approve the risky steps is called human-in-the-loop, and in Strobes it's the job of Supervisor Mode. In Auto mode, the agent runs on its own but always stops to ask you before high-risk actions, like running an exploit, sending database-changing queries such as UPDATE or DROP, or sending DELETE and PUT requests to production-tagged assets. Every action the agent wants to take, from logging a finding to running an exploit, can wait in the Human in the Loop queue until you approve or reject it.
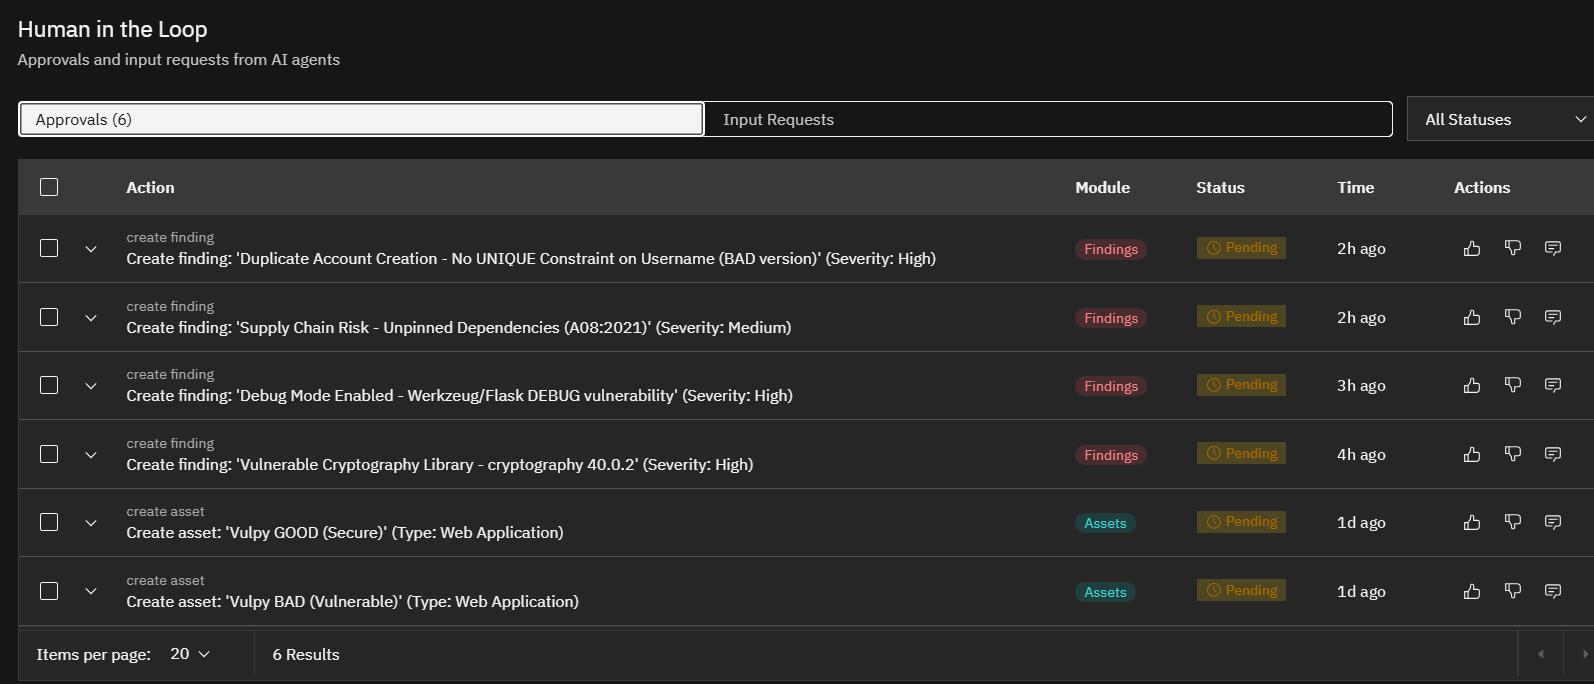
If you want even more control, switch to User mode. The agent then pauses before each major step and waits for you to approve, reject, or change it. For example, you can slow an nmap scan from -T4 to -T2 before it runs against a busy server.
How is AI pentesting different from automated scanning?
A scanner runs a set of checks and reports what matches, while an AI agent picks its next step based on what it just found. If it sees one user's invoice ID, it tries that ID as another user. If a small bug opens a door, it follows it to see where it leads, then saves proof that the issue is real.
Scanners are still useful for broad, repeatable checks. They're a quick, cheap way to check your whole estate for known CVEs, and DAST tools cover many common web vulnerabilities on their own. For a closer look at all three, see DAST vs pentesting vs AI pentesting.
What do studies show when AI goes up against human pentesters?
One useful comparison comes from Stanford researchers. In a December 2025 study, they set an AI agent called ARTEMIS loose on a live university network of about 8,000 hosts and compared it with 10 security professionals. ARTEMIS placed second overall, ahead of 9 of the 10 humans, and 82% of what it reported turned out to be valid. One version of it cost about $18 an hour to run, compared with about $60 an hour for a professional tester.
That result comes with limits, though. Other AI agents in the same study scored below most of the human testers, and ARTEMIS reported more false positives than the humans did. So the study shows what a well-built agent can do, not that every AI pentesting tool matches a skilled human. It also shows why proof matters. A finding you can't confirm is just a lead, which is why Strobes agents only report a finding once they have reproducible proof, like a working exploit for an app bug or the exact setting behind a cloud misconfiguration.
This gets even more important with bugs that take a few steps to find. Here's how an AI agent, or a human tester, checks whether a regular user can make themselves an admin.
1. GET /api/users/me             -> 200 OK, your ID (3f9c...), role "member"
2. GET /api/users/3f9c/roles     -> 200 OK, shows the role field
3. PATCH /api/users/3f9c/roles {"role":"admin"} -> 200 OK, change accepted
4. GET /api/admin/users          -> 200 OK, admin data (403 before step 3)
   result: a regular user just made themselves an admin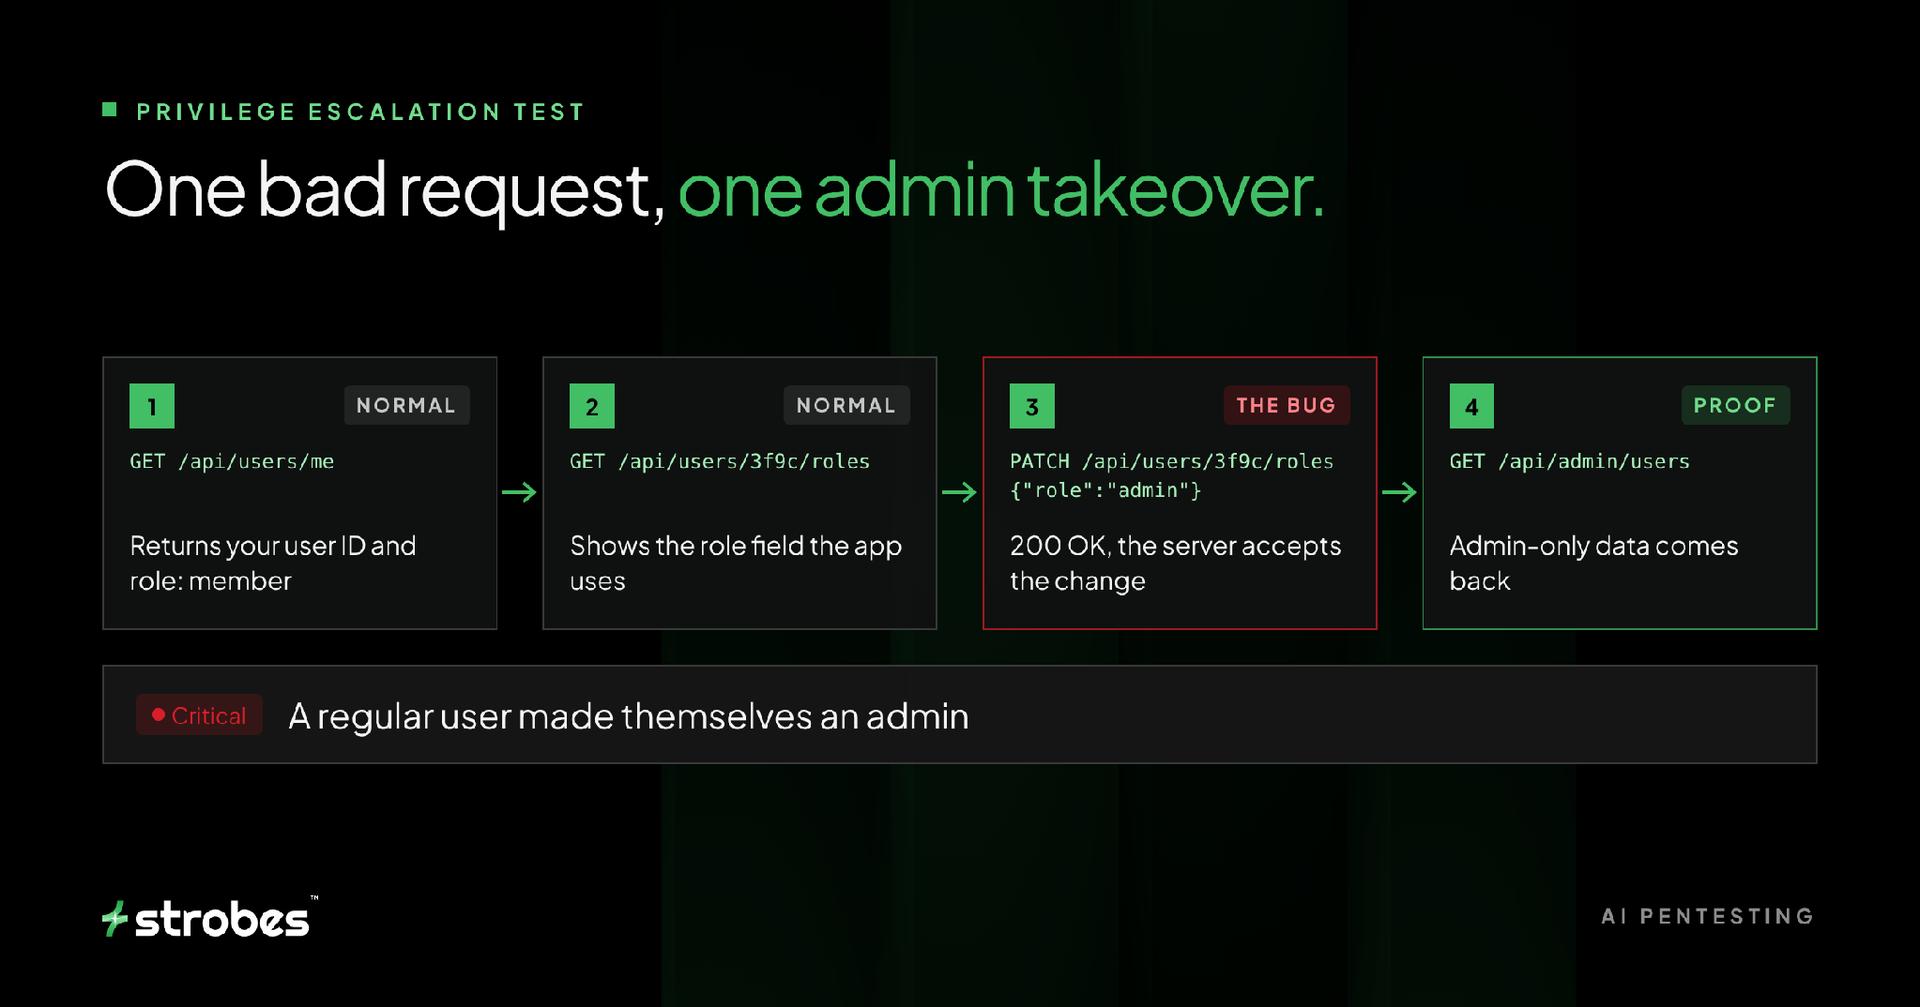
In this example, users are allowed to view their own profile and role, so steps 1 and 2 are normal. The bug is step 3, where the server lets a regular user change their own role. That's broken access control, ranked first on the OWASP Top 10 (2025). Step 4 is the proof, because a 200 OK on step 3 doesn't mean the role actually changed. Before the change, the same account got a 403 Forbidden on that admin page. Now the page opens, so the privilege escalation is confirmed.
Both a human tester and an AI agent can find this issue, check what the new admin access opens up, and retest it after the fix.
Is AI pentesting cheaper than a manual pentest?
Yes, for every Strobes test in the table below. A small web app pentest costs $5,760 done manually, compared with $5,000 for AI pentesting at list price or $3,500 with volume pricing. Across all the tests below, AI pentesting costs 13% to 61% less.
Both are priced in credits, but they're two different kinds of credits with different prices. That small web app uses 6 manual credits at $960 each, or 500 AI credits at $10 each ($7 with volume pricing).
| Test | Manual | AI (list, $10) | AI (volume, $7) |
|---|---|---|---|
| Web app (small, 11–30 pages) | $5,760 | $5,000 (13% less) | $3,500 (39% less) |
| Mobile app (small, 11–30 screens) | $5,760 | $5,000 (13% less) | $3,500 (39% less) |
| Network (large, 501–1,000 IPs) | $14,400 | $12,000 (17% less) | $8,400 (42% less) |
| Web API (large, 101–200 endpoints) | $14,400 | $12,000 (17% less) | $8,400 (42% less) |
| Cloud config (medium, 6–10 accounts) | $14,400 | $8,000 (44% less) | $5,600 (61% less) |
At list price, cloud config reviews show the biggest savings, and small web and mobile apps show the smallest. With volume pricing, savings jump to between 39% and 61%.
From there, your annual cost depends on how many tests you run and how you split them between manual and AI.
What does a hybrid pentest program cost?
Let's say you need 20 small web app tests a year. Here's what that costs with all manual testing, all AI testing, and a 50/50 hybrid where 10 tests stay manual.
| Approach | Annual cost (AI at $10 list rate) | Annual cost (AI at $7 volume rate) |
|---|---|---|
| All manual | $115,200 | $115,200 |
| All AI pentesting | $100,000 (save $15,200) | $70,000 (save $45,200) |
| Hybrid, 10 manual + 10 AI | $107,600 (save $7,600) | $92,600 (save $22,600) |
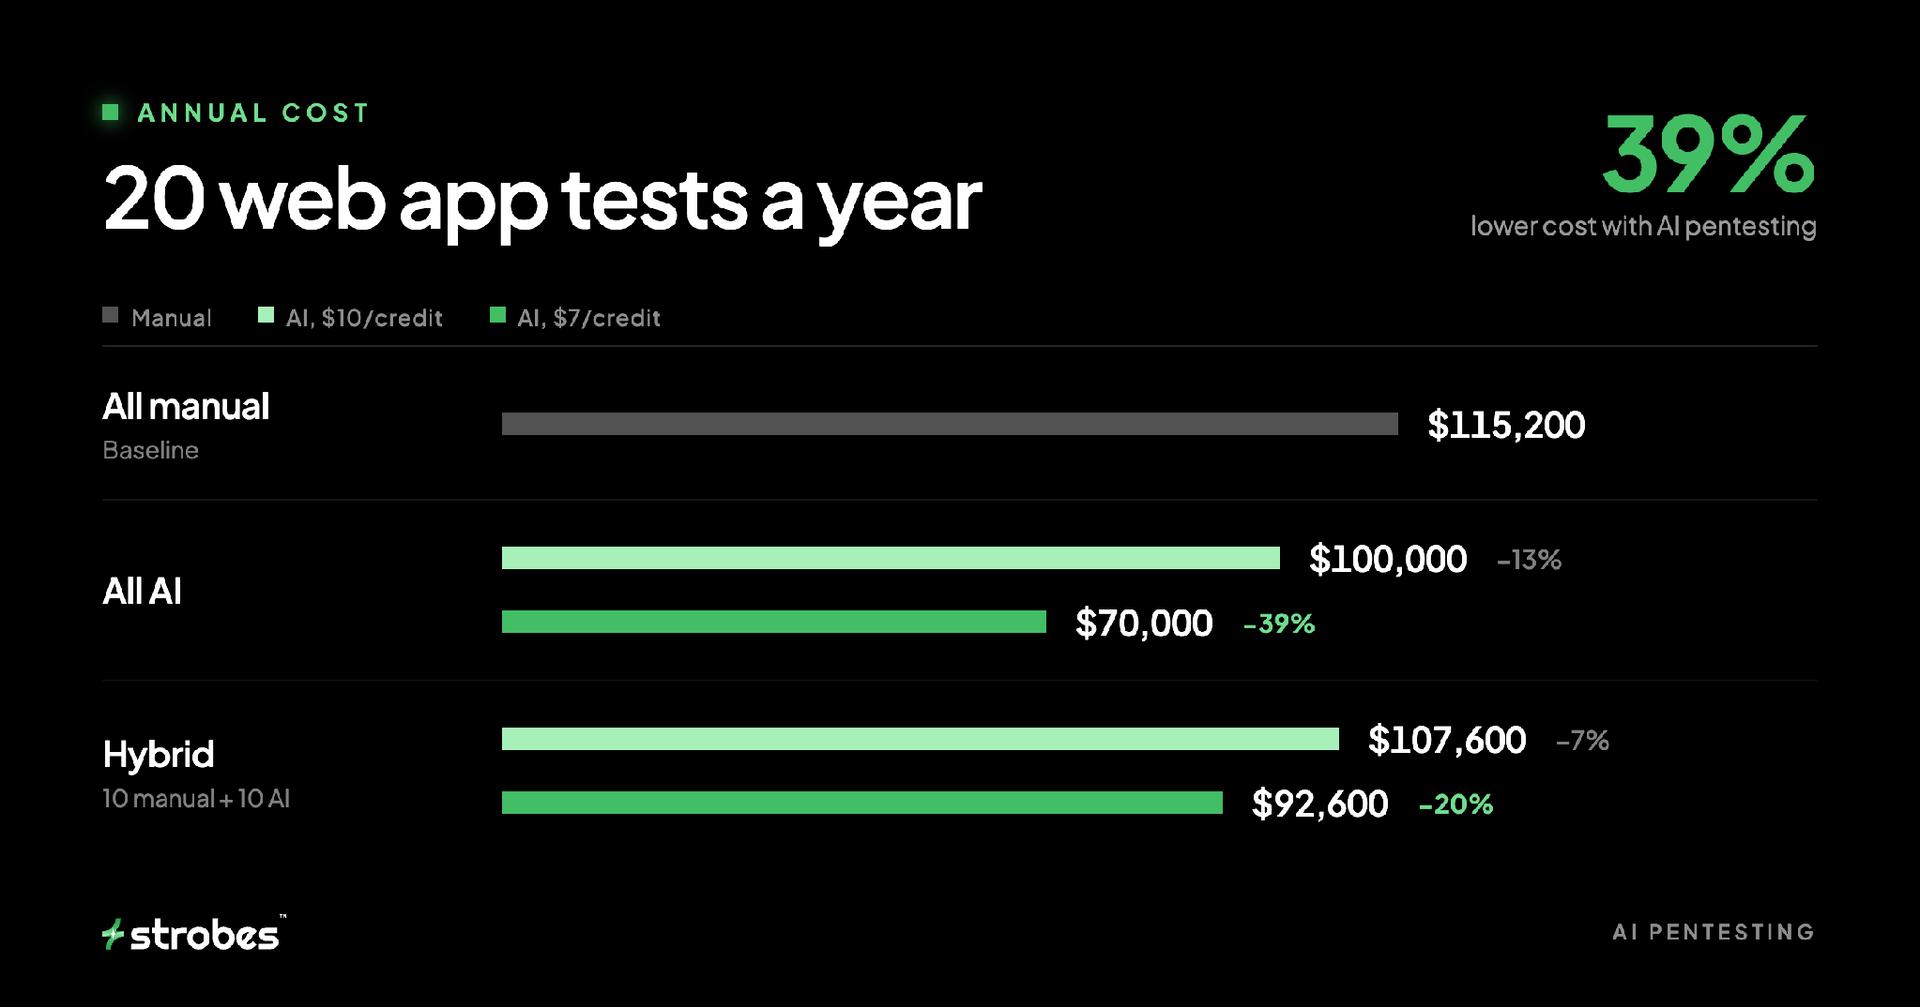
You can also look at it the other way around. If you moved your whole $115,200 manual budget to AI pentesting at volume pricing, it would pay for 32 small web app tests instead of 20. That's 1.6 times the testing capacity for the same spend, and that extra room is what lets you test more often, like after each major release.
Your own numbers will depend on your asset types and how many tests you keep manual. Plug them into our AI Pentest Savings Calculator to see your total.
Is AI pentesting accepted for PCI DSS, SOC 2, and other compliance checks?
It depends on the framework. PCI DSS asks for a qualified tester to own the work, while SOC 2 and ISO 27001 leave the method up to you.
| Framework | What it asks for | Where AI pentesting fits |
|---|---|---|
| PCI DSS v4.0.1 (Req. 11.4) | A pentest every year and after big changes, done by a qualified internal or external tester with organizational independence, plus retesting of exploitable findings and segmentation testing | A qualified tester must own the test and can use AI pentesting as part of it. AI can also cover the months between annual tests |
| SOC 2 | No pentest required. CC4.1 lists pentesting as one way to check your controls | AI pentest reports with a clear method and proof may be accepted. Confirm with your auditor first |
| ISO 27001 | Technical vulnerability management (Annex A 8.8), with no set method | Can support your evidence, as long as you show you find and fix issues |
| HIPAA | A proposed rule would require a pentest every 12 months, but it isn't final yet | Can support your risk analysis, but there's no set pentest rule to meet yet |
| FedRAMP | Testing should include manual techniques, not just automated scanning | Pair it with a manual test |
| Enterprise customer reviews | Depends on the customer, but often proven findings, proof of impact, and a retest | AI reports with reproducible proof fit well when the scope and method match what they asked for |
That last row matters as much as the auditor's view. When a big customer sends a security questionnaire, a recent report with proven findings and a clean retest helps a lot. For more on each framework, see our guides to SOC 2 penetration testing requirements and PCI DSS v4 testing changes.
When should you choose AI pentesting?
AI pentesting is the right call when you need to test a lot, test often, or get answers fast. That usually comes down to one of these situations.
-
You ship often, so new code would otherwise sit untested until the next manual pentest
-
You have many apps, APIs, or cloud accounts, more than a yearly manual budget can cover
-
You need fast retests, so you can confirm a fix the same day it goes out
-
You want evidence between annual tests for SOC 2, ISO 27001, or customer security reviews
To set it up well, give the agent a test account for each user role so it can check what each role can and can't reach. Before you choose a tool, check that it supports your targets, can stay logged in through the test, and gives evidence your team can review.
When should you choose a manual pentest?
A manual pentest is the right call when a person's judgment about your business is part of what you're paying for. That usually comes down to one of these situations.
-
A brand-new feature with custom logic, like a payments flow or permissions across multiple tenants
-
New AI or LLM features, where a tester can build a threat model around prompt injection, RAG data leakage, and what your AI agents are allowed to do
-
Your yearly PCI DSS pentest, which needs a qualified tester
-
Red team or social engineering work, like phishing your staff
-
A major launch or architecture change, where you want a fresh set of eyes on everything
-
A customer contract that names a human-led pentest
How should you split and schedule AI and manual testing?
Start by sorting your assets by risk, then match each group to the right kind of testing. Three steps get you there.
-
List your assets and tier them by how much damage a breach would cause. Customer data, payments, and anything in compliance scope go at the top.
-
Match each tier to a testing method. AI pentesting can cover all your supported apps, APIs, networks, and cloud accounts, and manual pentests go to your highest-risk assets.
-
Plan manual tests from a threat model. Give your tester a list of the attacks you worry about the most, so their time goes to fresh ground instead of findings the AI already proved.
Once you've split things up, set a schedule for each tier. Treat the table below as a starting point, then adjust it for your compliance needs and how often you ship.
| Risk tier | AI pentesting | Manual pentest |
|---|---|---|
| High (payments, customer data, compliance scope) | Every release or weekly | Quarterly |
| Standard (customer-facing apps) | Monthly or every release | Once a year and after big changes |
| Low (internal tools, low-risk apps) | Quarterly | Every 12 to 18 months |
Big events should trigger a test no matter where you are in the schedule. That includes a major release, a new compliance requirement, or a security incident. For more on keeping testing going between pentests, read why your annual penetration test is already obsolete.
How Strobes runs hybrid pentesting
Strobes puts AI pentesting and PTaaS on one platform, so findings from AI agents and human testers land in the same place. Every finding uses the same severity scale, from Critical down to Informational, and you can track each one all the way to a confirmed fix.
You can schedule recurring AI pentests, keep control of high-risk steps with Supervisor Mode, and reach internal targets through Agent Shell without opening inbound firewall ports. When a human tester joins through PTaaS, their findings show up right next to the AI's.
Frequently asked questions
Can AI pentesting replace a manual pentest?
For a lot of your apps, AI pentesting can handle the testing on its own, release after release. You'll still want a qualified human for PCI DSS pentests and some high-risk features, which is why many teams use both.
How much does a manual pentest cost?
At Strobes, a manual pentest runs $5,760 for a small web or mobile app and $14,400 for a large network or API. Your price depends on the scope, since bigger apps and networks use more credits.
Does PCI DSS accept an AI pentest report?
PCI DSS requires a qualified internal or external tester to own the annual pentest. That tester can use AI pentesting as part of the work, and AI can also cover the time between annual tests and speed up retests.
Does SOC 2 require a penetration test?
No. SOC 2 doesn't require one, though CC4.1 lists pentesting as one way to check your controls. Many auditors expect to see one anyway, and an AI pentest report with a clear method and proof may be accepted. Check with your auditor first.
How long does a manual pentest take compared with an AI pentest?
A manual pentest usually takes one to two weeks, plus time to schedule the tester. An AI pentest on Strobes usually delivers a full report within hours, depending on scope, so you can test new code soon after it goes live.
Can AI pentesting find access control flaws like IDOR?
Yes. AI agents log in as different users, swap IDs between accounts, and check whether one user can see another's data, which is exactly how IDOR bugs show up. For highly custom workflows, adding a manual test gives you a second look.
Do I need a retest after fixing findings?
Yes. A retest confirms your fix actually closed the hole, and PCI DSS requires one for exploitable issues found in your pentest. With AI pentesting, you can rerun the test on demand right after the fix goes out.
Ready to see your own numbers? Try the AI Pentest Savings Calculator or book a demo.