
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
Top CVEs of September 2026: Four Zero-Days, and Patching Wasn’t the Fix
Four of September 2026’s top five CVEs were exploited before a patch existed. Fix order, fixed builds, and the compromise check each one needs.
Top CVEs of August 2026
August's CVSS 7.0 was a Lazarus zero-day exploited for five weeks. Its CVSS 10.0 needed no patch at all. The top CVEs of August 2026, ranked by exploitation evidence rather than severity, with remediation steps for all five.
Top CVEs of July 2026
Five CVEs defined July 2026, ranked by what attackers actually exploited, not CVSS: an AD FS zero-day, twin SharePoint RCEs, a May patch that became a July KEV deadline, and the month's highest score that nobody touched.
Top CVEs of May 2026: 5 Critical Flaws to Patch Now
Five CVEs dominated May 2026: cPanel's two-month zero-day, Linux's stealth kernel priv-esc, Langflow exploited 20 hours after disclosure, n8n's perfect-10 RCE chain, and Microsoft's SSO bypass. Here's what happened and what to do.
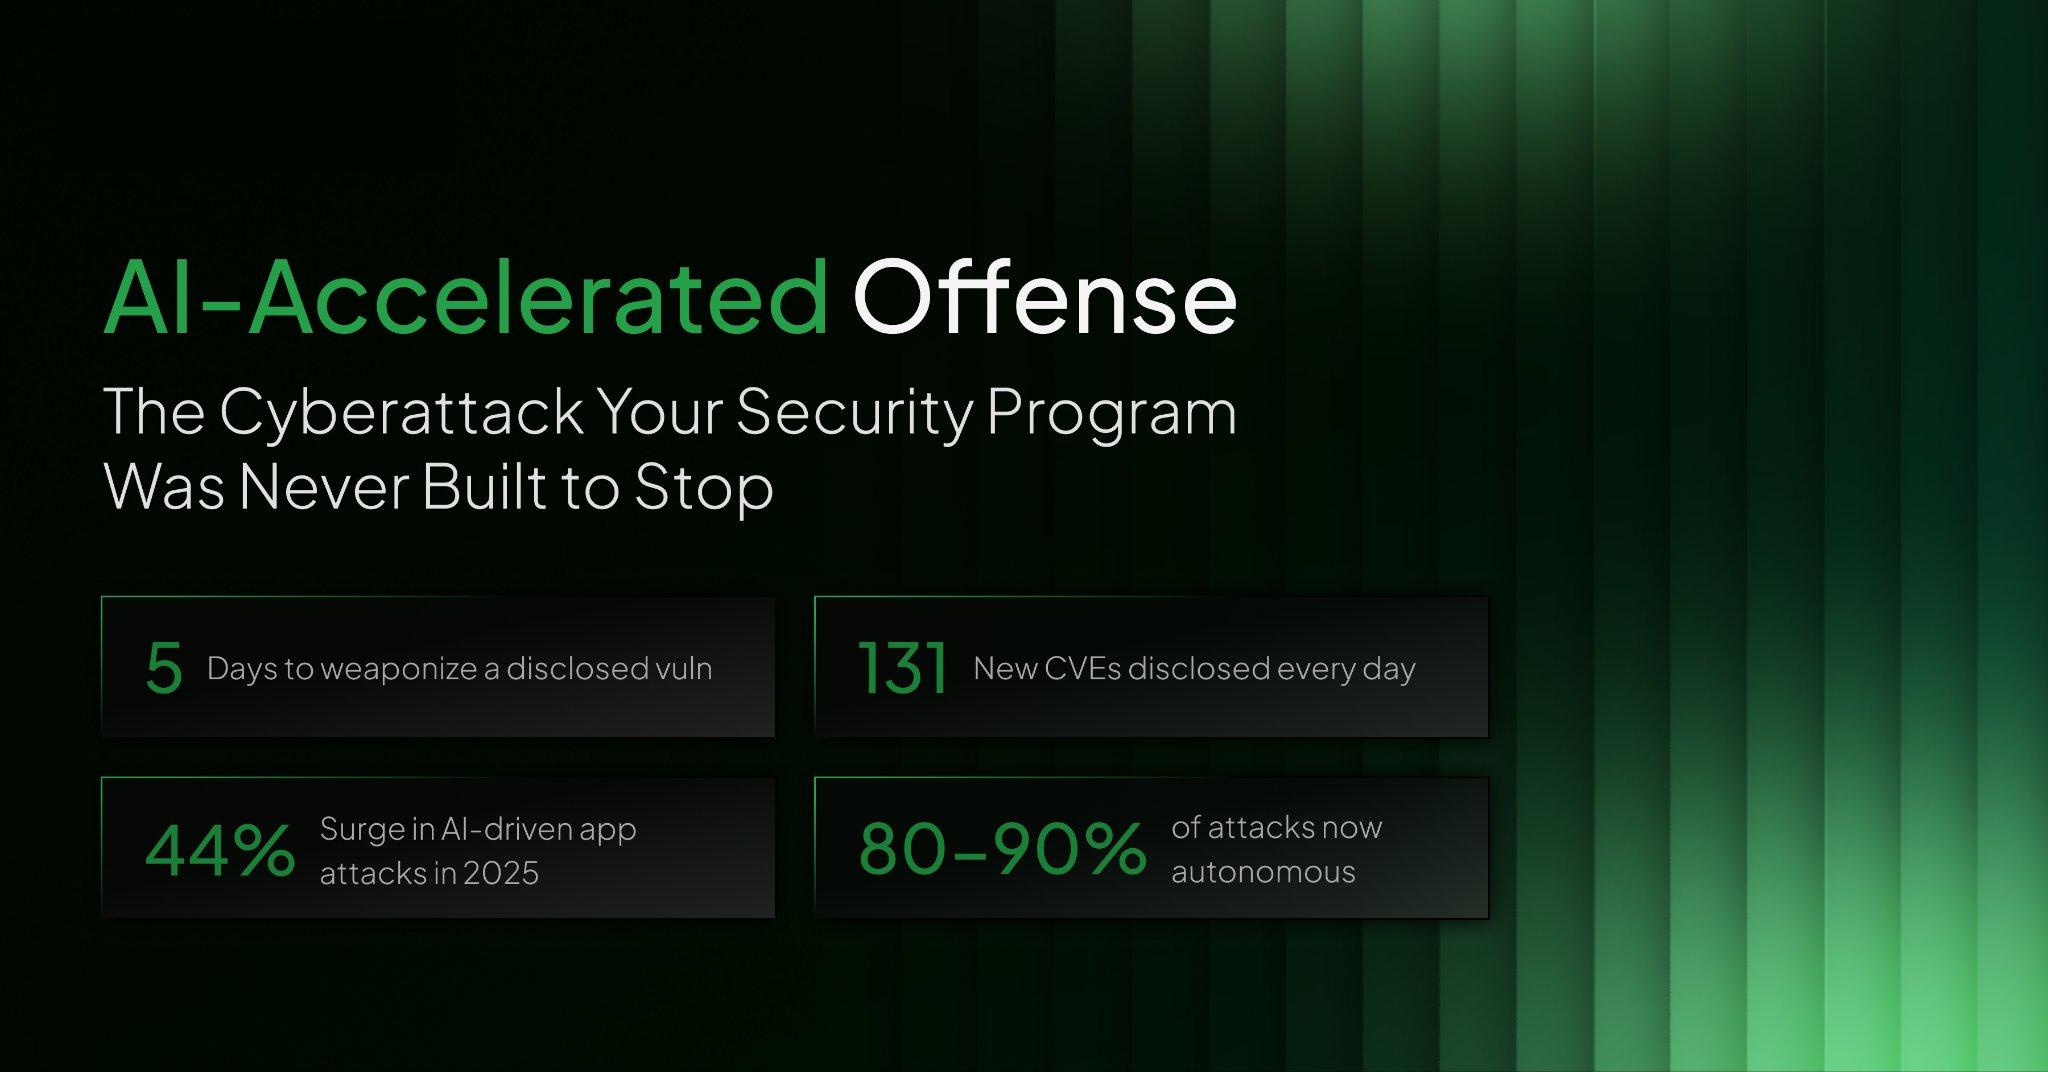
AI-Accelerated Offense: The Cyberattack Your Security Program Was Never Built to Stop
AI-Accelerated Offense uses autonomous agents to run the full cyberattack chain in hours. A frontier AI model found thousands of zero-day vulnerabilities across every major OS and browser in weeks. See how it works, why your security program is already behind, and what to do now.
Is Claude Mythos the End of Pentesting?
Claude Mythos found thousands of zero-days in Linux, browsers, and Apache. Does that make pentesting platforms obsolete? Understanding why models, harnesses, and platforms are three different things -- and why smarter AI makes Strobes more valuable, not less.
How Strobes AI Turns a Supply Chain Zero-Day into a Full Exposure Assessment in Under 30 Minutes
When the axios npm package was compromised on March 31, 2026, Strobes AI agents autonomously performed incident response, identified every exposed repository across the attack surface, and generated a complete exposure assessment with remediation tasks in under 30 minutes.
Identifying Security Misconfigurations in Enterprise Networks
Verizon's DBIR ties a large share of breaches to misconfiguration, not zero-days. Here are the enterprise network misconfigurations testers find most, with the exploit output and the GPO-level fixes.
CVE-2025-61882 Explained: The Oracle Zero-Day Breach That Hit Enterprises Hard
A critical zero-day vulnerability in Oracle E-Business Suite (EBS) was exploited by the Cl0p ransomware group in mid-2025. The flaw, later tracked as CVE-2025-61882, allowed remote code execution without authentication, giving attackers complete control over affected systems. On the Strobes Vulnerab
CVE-2025-53770 - Microsoft SharePoint zero-day exploited in RCE attacks
CVE-2025-53770 is a critical remote code execution vulnerability (CVSS 9.8) in on-premises Microsoft SharePoint Server that allows unauthenticated attackers to completely compromise servers through deserialization of untrusted data. The Microsoft SharePoint Zero-Day vulnerability is currently being
The Ultimate Guide to Zero-Day Vulnerability Exploits & Attacks
Nowadays, zero-day vulnerability exploits are among the most popular topics in the infosec community. Zero-days are unknown vulnerabilities that attackers can exploit to access systems or data. These vulnerabilities are usually found in software or hardware and can be used to bypass security control