Strobesstrobes
Platform
Solutions
Resources
Customers
Company
Pricing
Book a Demo
Strobesstrobes

Strobes connects every exposure signal to autonomous action, so security teams fix what matters, prove what works, and stop chasing noise.

Book a DemoTalk to an expert
ISO 27001SOC 2CREST
  • Platform
  • Platform Overview
  • Agentic Exposure Management
  • AI Agents
  • Integrations
  • API & Developers
  • Workflows & Automation
  • Analytics & Reporting
  • Solutions
  • Exposure Assessment (EAP)
  • Attack Surface Management
  • Application Security Posture
  • Risk-Based Vulnerability Management
  • Adversarial Exposure Validation (AEV)
  • AI Pentesting
  • Pentesting as a Service
  • CTEM Framework
  • By Industry
  • Financial Institutions
  • Technology
  • Retail
  • Healthcare
  • Manufacturing
  • By Roles
  • CISOs
  • Security Directors
  • Cloud Security Leaders
  • App Sec Leaders
  • Resources
  • Quick Agentic Pentest
  • Blog
  • Customer Stories
  • eBooks
  • Whitepapers
  • Datasheets
  • Videos & Demos
  • Exposure Management Academy
  • Pentesting ROI Calculator
  • Pentest Health Check
  • Security Tool ROI Calculator
  • Company
  • About Strobes
  • Meet the Team
  • Trust & Security
  • Contact Us
  • Careers
  • Become a Partner
  • Technology Partner
  • Partner Deal Registration
  • Press Release

Weekly insight for security leaders

CTEM research, agentic AI trends, and what's actually moving the needle.

© 2026 Strobes Security Inc. All rights reserved.

Privacy PolicyTerms of ServiceCookie PolicyAccessibilitySitemap
Blog

Security Insights

Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.

Top CVEs of August 2026 by Strobes: the vulnerabilities that mattered this month, what is actively exploited and what to remediate first
CVEVulnerability Intelligence

Top CVEs of August 2026

August's CVSS 7.0 was a Lazarus zero-day exploited for five weeks. Its CVSS 10.0 needed no patch at all. The top CVEs of August 2026, ranked by exploitation evidence rather than severity, with remediation steps for all five.

Sep 3, 202614 min
How to Achieve Cheaper, Faster and Accurate Pentests
Prev12345Next
Penetration TestingOffensive Security

How to Achieve Cheaper, Faster and Accurate Pentests

Cheaper, faster and accurate pentests were never a real tradeoff. Context removes it: one graph of assets, code and cloud that every engagement reads from and writes back to.

Aug 21, 202623 min
Tooling as Code and Structured Scratchpads
engineeringOffensive Security

Tooling as Code and Structured Scratchpads

The two changes that moved our AI security agents furthest this year had nothing to do with the model. Here is how tooling as code and structured scratchpads reshaped how the agents act, and how they prove a finding is real.

Aug 3, 202615 min
How agentic pentesting separates test failures from real security findings
Penetration TestingOffensive Security

How Agentic Pentesting Separates Test Failures From Real Security Findings

Agentic pentesting reliability on unstable apps: a six-state failure taxonomy, safe retry rules, and what a trustworthy pentest report must disclose.

Jul 8, 202618 min
Bug bounty vs pentesting vs AI pentesting comparison featured image
Penetration TestingApplication Security

Bug Bounty vs. Pentesting vs. AI Pentesting: Which Model Fits Your AppSec Program?

Bug bounty vs pentesting vs AI pentesting: compare costs, coverage, compliance, and when to use each model. Build a layered AppSec testing strategy.

Jun 4, 202621 min
Continuous application pentesting for DevSecOps teams - AI-driven pentesting in CI/CD pipelines
Penetration TestingApplication Security

Continuous Application Pentesting for DevSecOps Teams

How DevSecOps teams integrate continuous application pentesting into CI/CD pipelines. AI-driven testing, run-over-run diffing, and developer workflow integration.

Jun 4, 202619 min
Why AI-Generated Exploit Code Must Run in Isolation
LLM SecurityOffensive Security

Why AI-Generated Exploit Code Must Run in Isolation

Agent-written exploit code is the new RCE vector aimed at the tester. Here's why per-task isolation and egress control are non-negotiable.

May 29, 202613 min
ISO 27001 Penetration Testing Requirements
CompliancePenetration Testing

ISO 27001 Penetration Testing Requirements

ISO 27001:2022 never names penetration testing, yet it is how you evidence Annex A 8.8 and 8.29 at a surveillance audit. The honest read on required vs expected, with the 2013 lineage and the Oct 2025 deadline.

May 20, 20268 min
PCI DSS Penetration Testing Requirements
CompliancePenetration Testing

PCI DSS Penetration Testing Requirements

PCI DSS v4.0.1 Requirement 11.4 is the rare standard that names penetration testing outright: internal and external annually plus after change, segmentation at 12 or 6 months, mandatory since 31 Mar 2025.

May 5, 20267 min
Top 10 Data Breaches of April 2026 - Monthly Security Briefing
Data BreachesCybersecurity

Top 10 Data Breaches of April 2026

The biggest data breaches of April 2026 ranked and analyzed, from Checkmarx supply chain poisoning to Salesforce misconfigurations and ransomware hitting two major US banks.

May 1, 202615 min
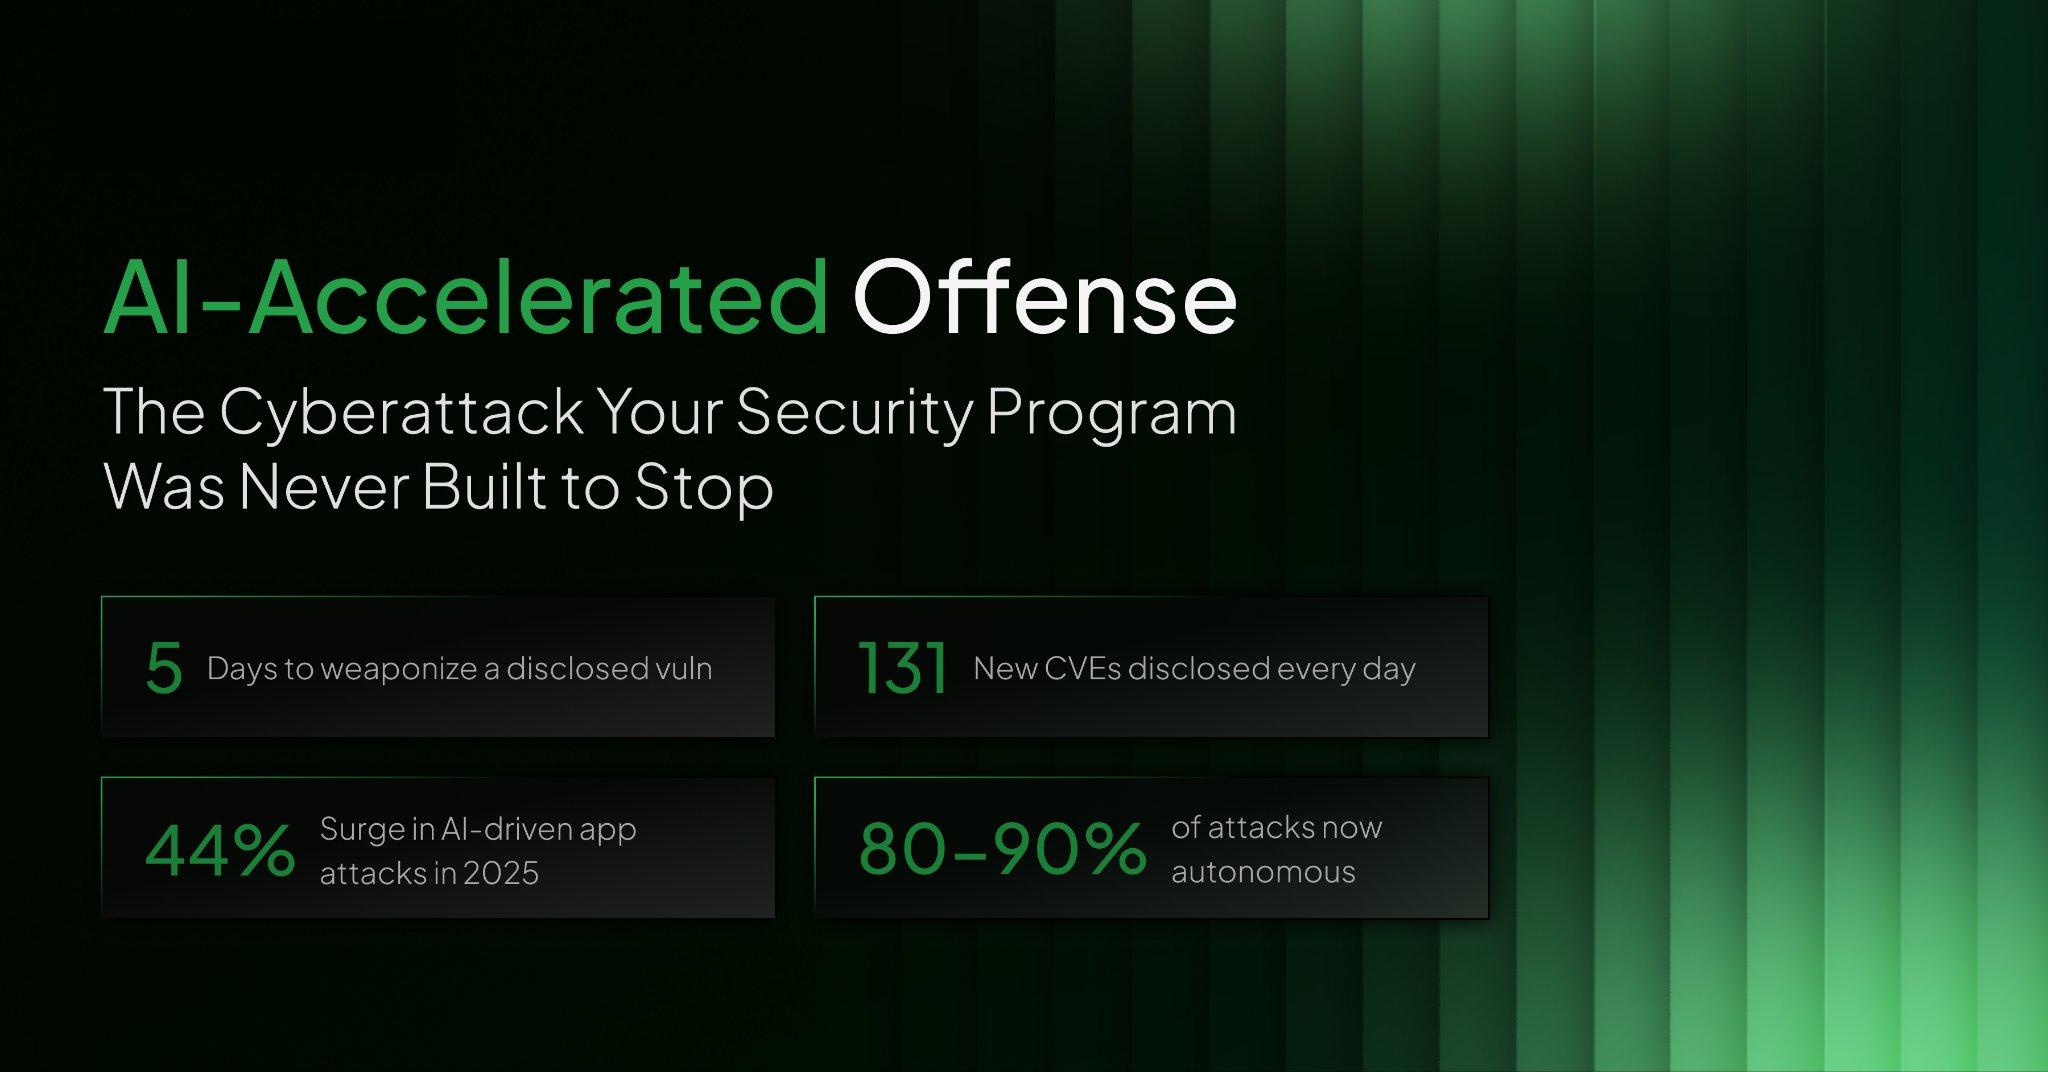
AI-Accelerated Offense: 5 days to weaponize a disclosed vulnerability, 131 new CVEs daily, 44% surge in AI-driven attacks, 80-90% of attacks now autonomous
Offensive SecurityCybersecurity

AI-Accelerated Offense: The Cyberattack Your Security Program Was Never Built to Stop

AI-Accelerated Offense uses autonomous agents to run the full cyberattack chain in hours. A frontier AI model found thousands of zero-day vulnerabilities across every major OS and browser in weeks. See how it works, why your security program is already behind, and what to do now.

Apr 23, 202613 min
HIPAA Penetration Testing Requirements
CompliancePenetration Testing

HIPAA Penetration Testing Requirements

HIPAA never says "penetration test," but the Security Rule's risk analysis and its REQUIRED evaluation standard expect technical testing of every system touching ePHI. Here is the precise read.

Apr 20, 20267 min