
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.

What Is Agentic Pentesting? The Complete Guide for Security Teams (2026)
Agentic pentesting uses specialized AI agents to test your entire attack surface in hours, not weeks. Here is how it works, what surfaces it covers, how safety is enforced, and how to evaluate platforms with real benchmarks.

Best AI Pentesting Tools in 2026: Ranked, Priced & Compared (12 Tools)
Which AI pentesting tool actually reduces risk in 2026? We reviewed 12 platforms on autonomy, proof quality, pricing, and what happens after a vulnerability is found.

Is Claude Mythos the End of Pentesting?
Claude Mythos found thousands of zero-days in Linux, browsers, and Apache. Does that make pentesting platforms obsolete? Understanding why models, harnesses, and platforms are three different things -- and why smarter AI makes Strobes more valuable, not less.

Agentic Pentesting with Strobes AI
What happens when you point Strobes AI at a real web app and let it run a full OWASP WSTG assessment with zero hand-holding? 32 tasks, 21 phases, 42 confirmed vulnerabilities — all autonomous.
DAST vs Penetration Testing vs Agentic Pentesting
DAST scans running apps automatically, pentesting adds human exploitation, and agentic pentesting is the AI-driven third category. Here is how all three compare on depth and frequency.
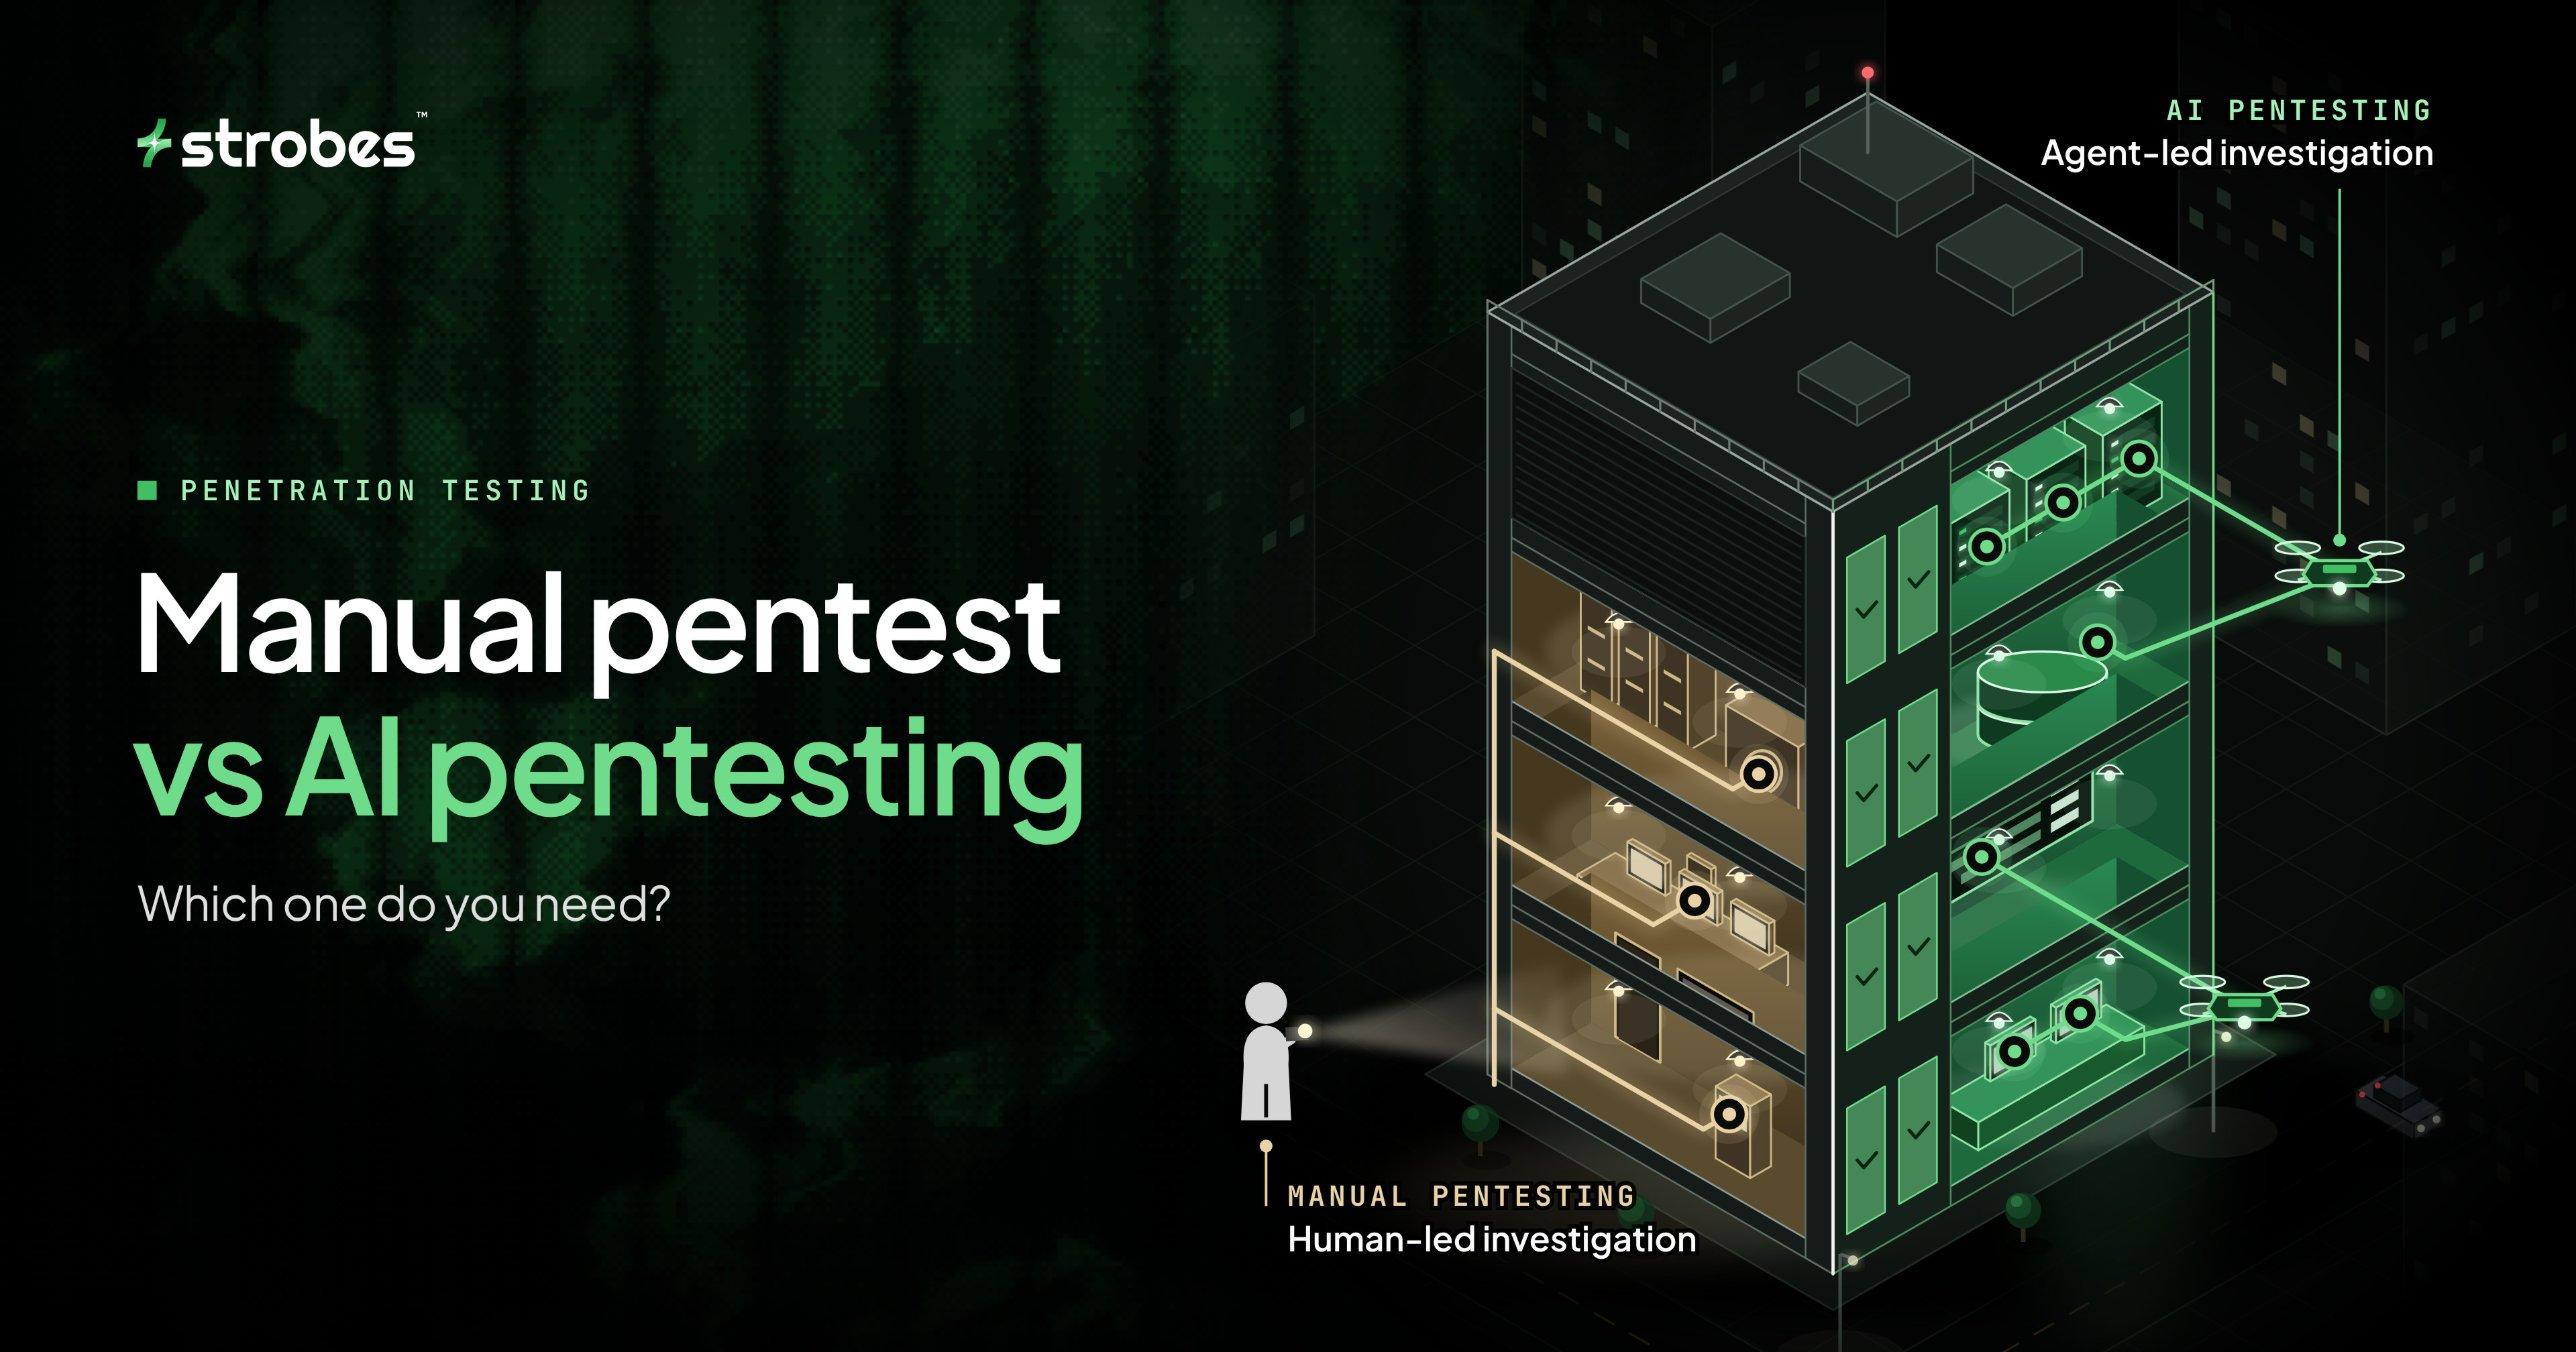
Manual pentesting vs AI pentesting: Which one do you need?
A manual pentest gives you human depth for business logic and PCI DSS. AI pentesting gives you proven findings on every release for 13% to 61% less. Here is where each fits, what it costs, and how to build a hybrid program.