
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.

How to Pentest APIs at Scale (Without Hiring 10 More Pentesters)
Learn how to pentest hundreds of API endpoints using AI agents. Cover OWASP API Top 10, authorization testing, and scale without hiring more pentesters.
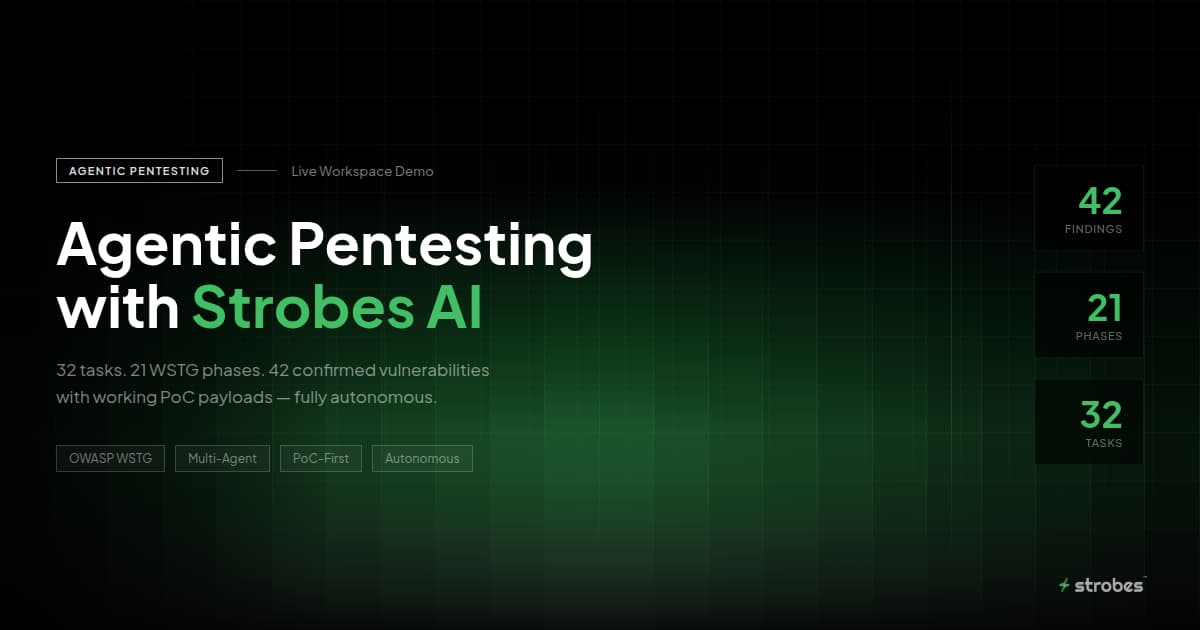
Agentic Pentesting with Strobes AI
What happens when you point Strobes AI at a real web app and let it run a full OWASP WSTG assessment with zero hand-holding? 32 tasks, 21 phases, 42 confirmed vulnerabilities — all autonomous.
Mobile App Penetration Testing Checklist (OWASP MASVS)
A MASVS-aligned mobile pentest checklist that runs highest-yield first: storage and network before resilience, with the real apktool, jadx, MobSF, and objection output you read at each step.
OWASP WSTG: The Web Security Testing Guide Explained
The OWASP WSTG is the methodology behind most web pentest reports. Here is how its 12 categories, stable test IDs, and Top 10 mapping work in a real engagement.
OWASP Top 10 for LLMs: Key Risks & Mitigation Strategies
The rapid advancement of AI, particularly in large language models (LLMs), has led to transformative capabilities in numerous industries. However, with great power comes significant security challenges. The OWASP Top 10 for LLMs addresses evolving threats. This article explores what's new, what’s ch
OWASP Mobile Top 10 Vulnerabilities [2025 Updated]: Key Impacts & Preventions
The OWASP Mobile Top 10 2025 highlights the most critical security risks in mobile applications, helping organizations protect user data, ensure compliance, and build digital trust. This guide explains key threats and practical strategies to address them. Learn how Strobes, with Continuous Threat Ex
API Penetration Testing Methodology and the OWASP API Top 10
A repeatable API pentest methodology on the OWASP API Top 10 (2023): five phases, a test per risk, a real BFLA-to-BOLA chain, a findings table, and config-level fixes.
API Penetration Testing Checklist
A phase-by-phase API penetration testing checklist with the real requests, the Schemathesis and Autorize runs, a findings table, and the config fixes, all mapped to the OWASP API Top 10.
Penetration Testing Standards: PTES, OSSTMM, NIST, and OWASP
PTES, OSSTMM, NIST SP 800-115, and the OWASP guides are the four standards behind professional pentesting. Here is what each covers, how they stack, and how to spot a vendor faking it.

Understanding the OWASP Top 10 Application Vulnerabilities
The OWASP Top 10 is a globally recognized guide to the most critical web application security risks. Compiled by industry experts, it highlights vulnerabilities like broken access control, cryptographic failures, and injection attacks, issues that put sensitive data and business operations at risk.