
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
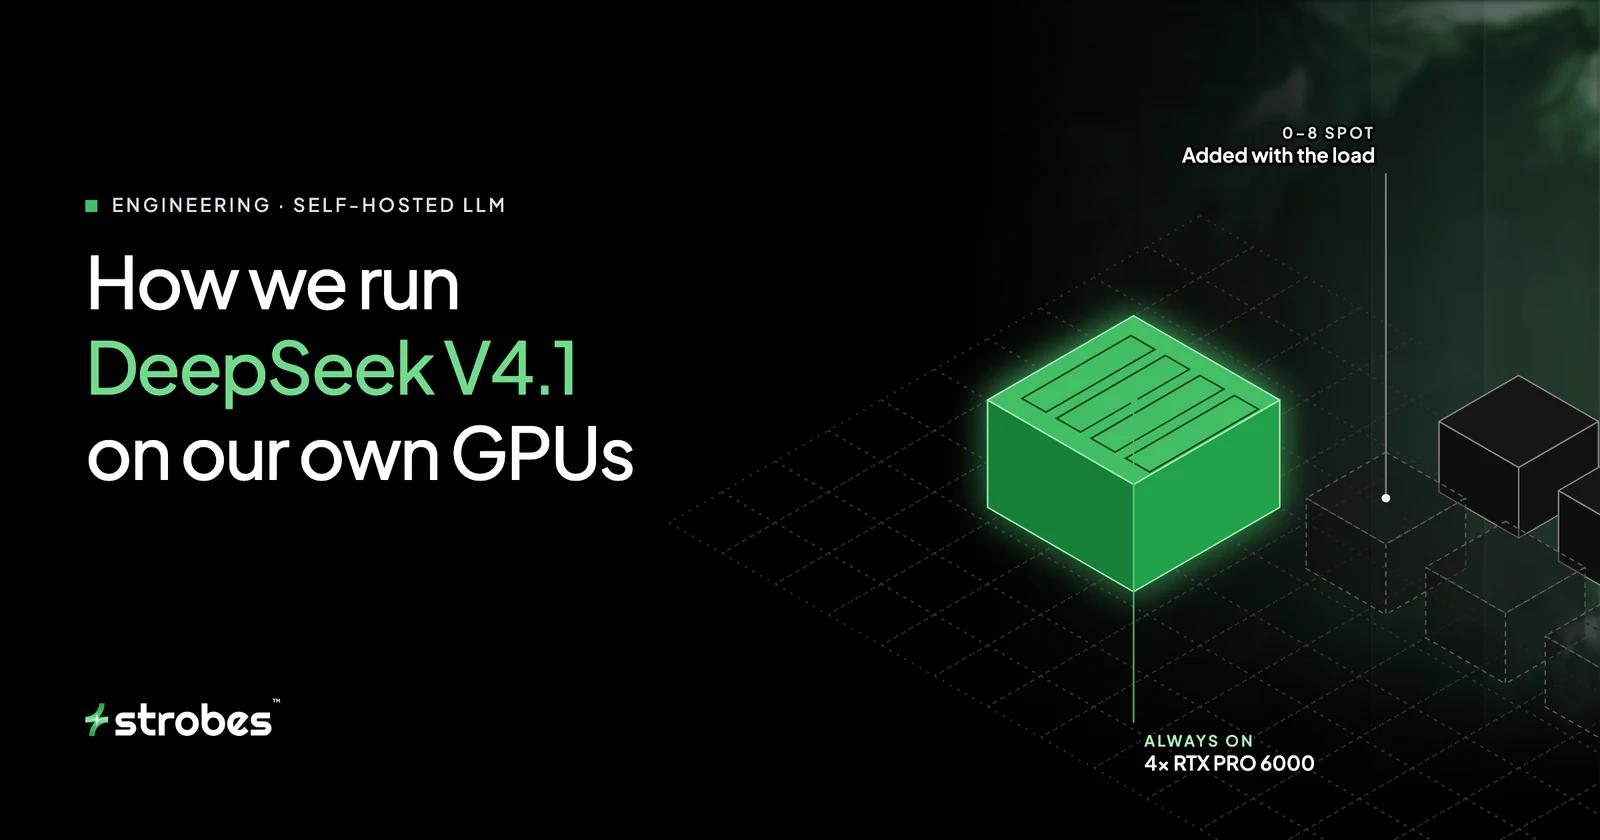
Running DeepSeek V4.1 Flash in production: serving, KV caching and autoscaling on AWS
A technical guide to self-hosting DeepSeek V4.1 Flash for long-context agent workloads: vLLM configuration, a latency model for sizing, tiered and shared KV cache in S3, prefix-aware routing, autoscaling and unit costs.

Top CVEs of June 2026: 5 Critical Flaws to Patch Now
Five CVEs defined June 2026: Check Point VPN bypass, Splunk pre-auth RCE, Windows HTTP.sys kernel RCE, LiteLLM AI-gateway RCE, and Defender BlueHammer. How to fix each.

A Poisoned PyPI Package Quietly Hit 36 Percent of Cloud Environments Through LiteLLM
LiteLLM 1.82.7 and 1.82.8 silently swept AWS credentials, Kubernetes configs, and SSH keys from 3.4 million daily installs. Here is exactly what the payload did and how Strobes AI detects and shuts it down.

Building an AI Harness for Offensive Security: What It Takes to Turn LLMs Into Reliable Pentest and Validation Operators
The model is 20% of the problem. Here is the engineering story behind the orchestration, tooling, middleware, and infrastructure that turns a capable LLM into a reliable penetration testing operator.
OWASP Top 10 for LLMs: Key Risks & Mitigation Strategies
The rapid advancement of AI, particularly in large language models (LLMs), has led to transformative capabilities in numerous industries. However, with great power comes significant security challenges. The OWASP Top 10 for LLMs addresses evolving threats. This article explores what's new, what’s ch
Cybersecurity Trends in 2025: Lessons from 2023 & Predictions to Watch Out for!
2024 has seen the AI boom with LLM models taking all over the internet and thousands of organizations fine-tuning it into their existing processes. Well, the cybersecurity world hasn’t been left behind either. Organizations are incorporating AI models into their anti-malware systems and leveraging e