Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
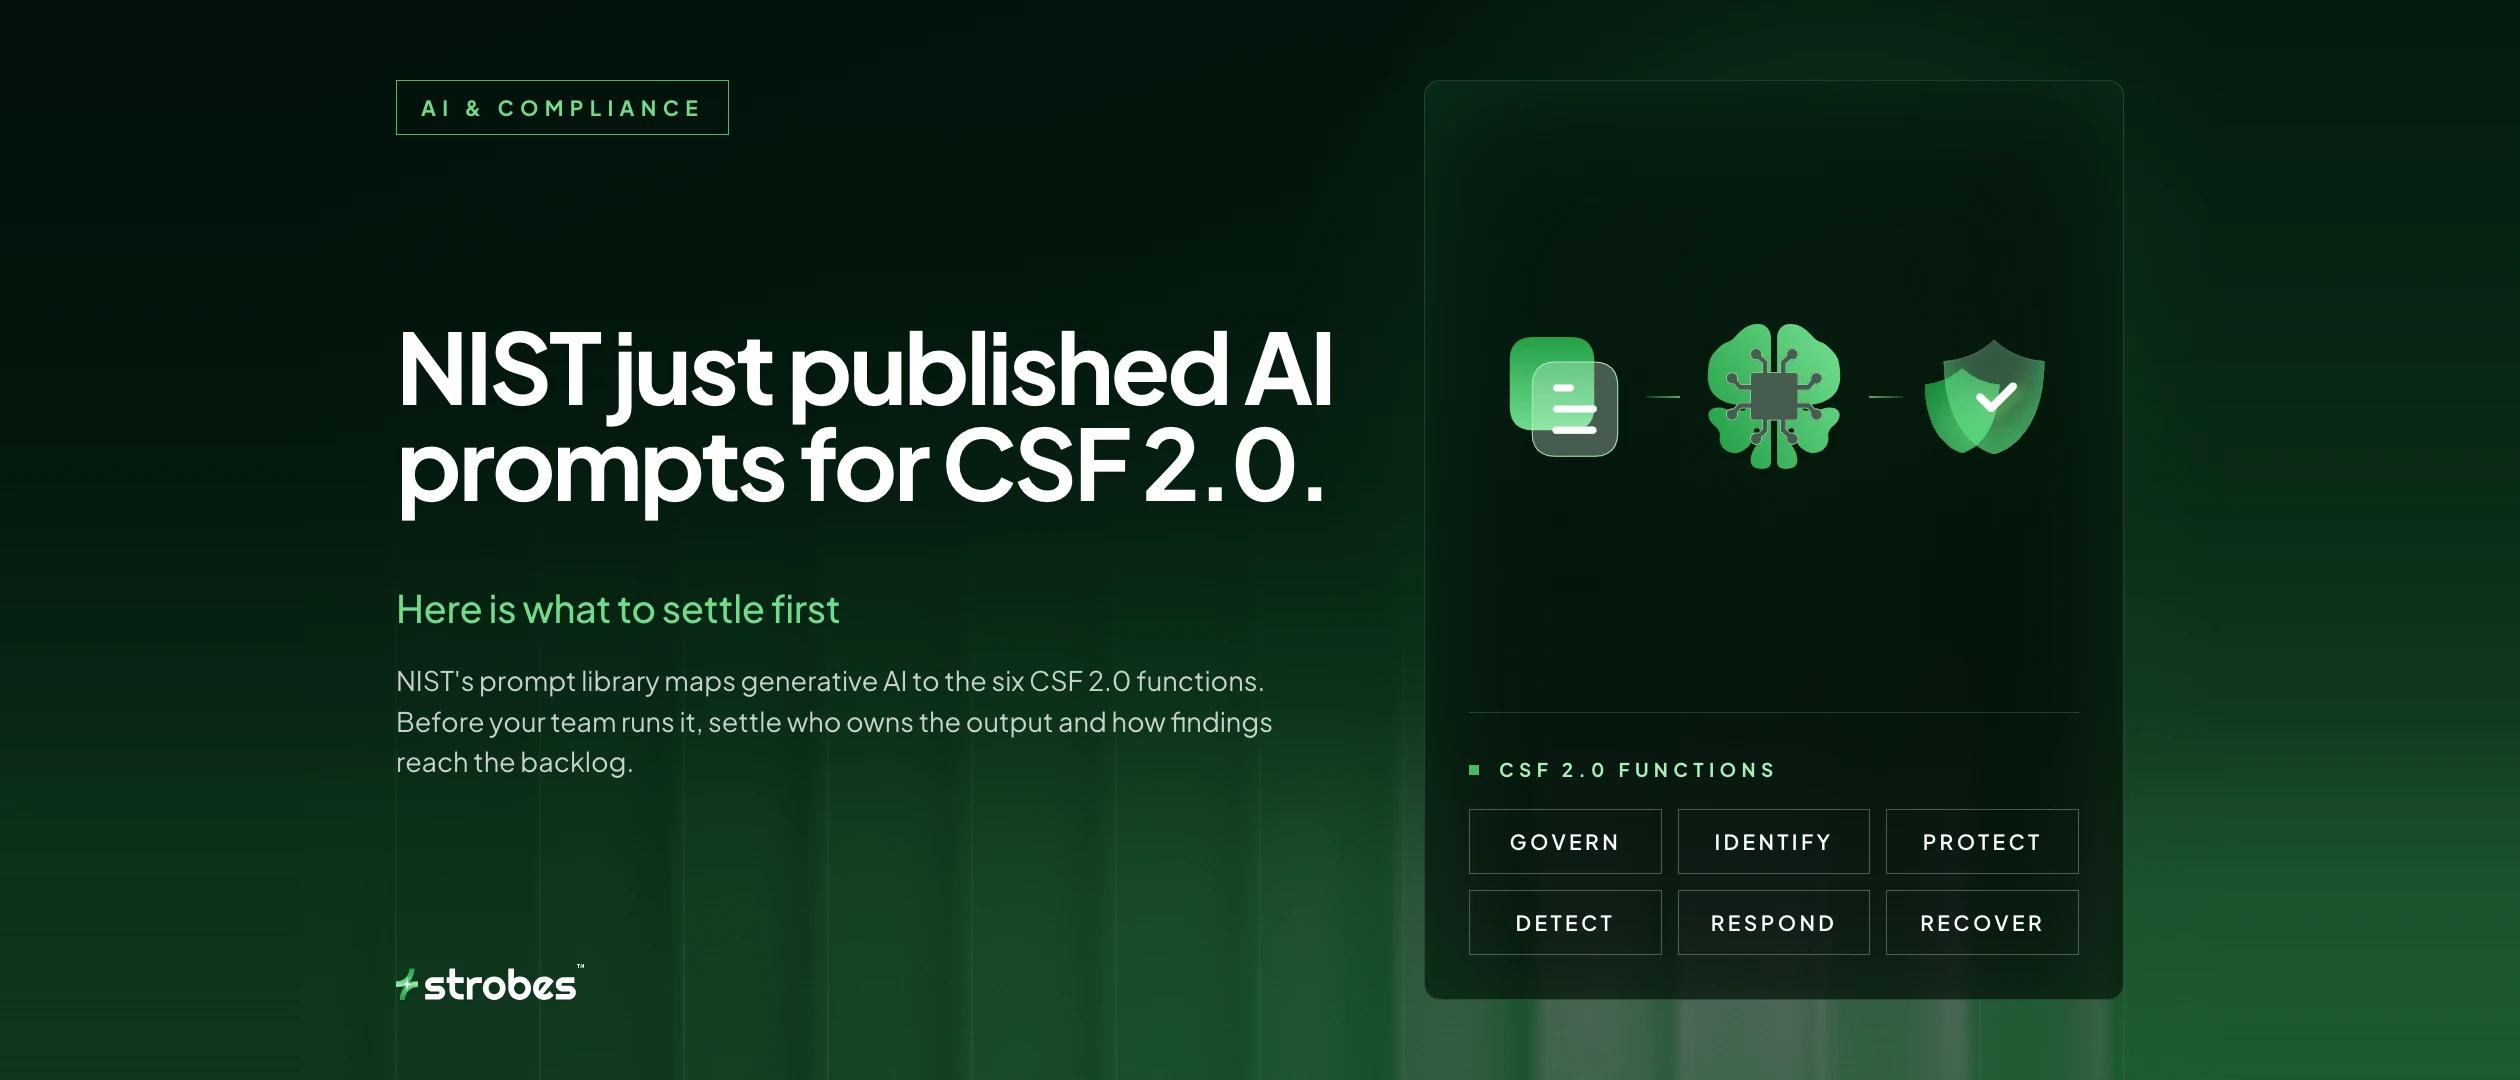
NIST's draft SP 1353 provides AI prompts for three CSF 2.0 tasks and says weeks of drafting compresses into hours. Here is what the prompts can draft, what only humans can validate, and the four things to settle before anyone opens a model.
Red team vs blue team is the wrong question for a CISO. The right one is how fast the gap between what red gets away with and what blue catches is closing. Here is how to run both.
“Let’s buy one more tool,” - isn’t it something you have heard before? The CISO tools box is so jam-packed that it’s even tough to remember the work of each tool. The biggest question for CISO is not how many tools are required but whether the tools offer real-time and actionable security. When ever
In the ever-evolving landscape of cybersecurity, organizations face a constant battle against hackers and data breaches. The role of the Chief Information Security Officer (CISO) is crucial in safeguarding digital assets and mitigating risks. However, it is an unfortunate reality that when an organi
As corporate and public sector companies continue to become more digital, there are an increasing number of security risks. It is difficult for any security team to promptly fix every one of those vulnerabilities without a major increase in resources. Chief information security officers (CISOs) must
Cyber threat monitoring, repellence, and response while meeting compliance requirements are established duties for Chief Information Security Officers (CISOs) or their equivalents. However, the business landscape is continually shifting. According to a commonly cited statistic, 90% of the world's da
