
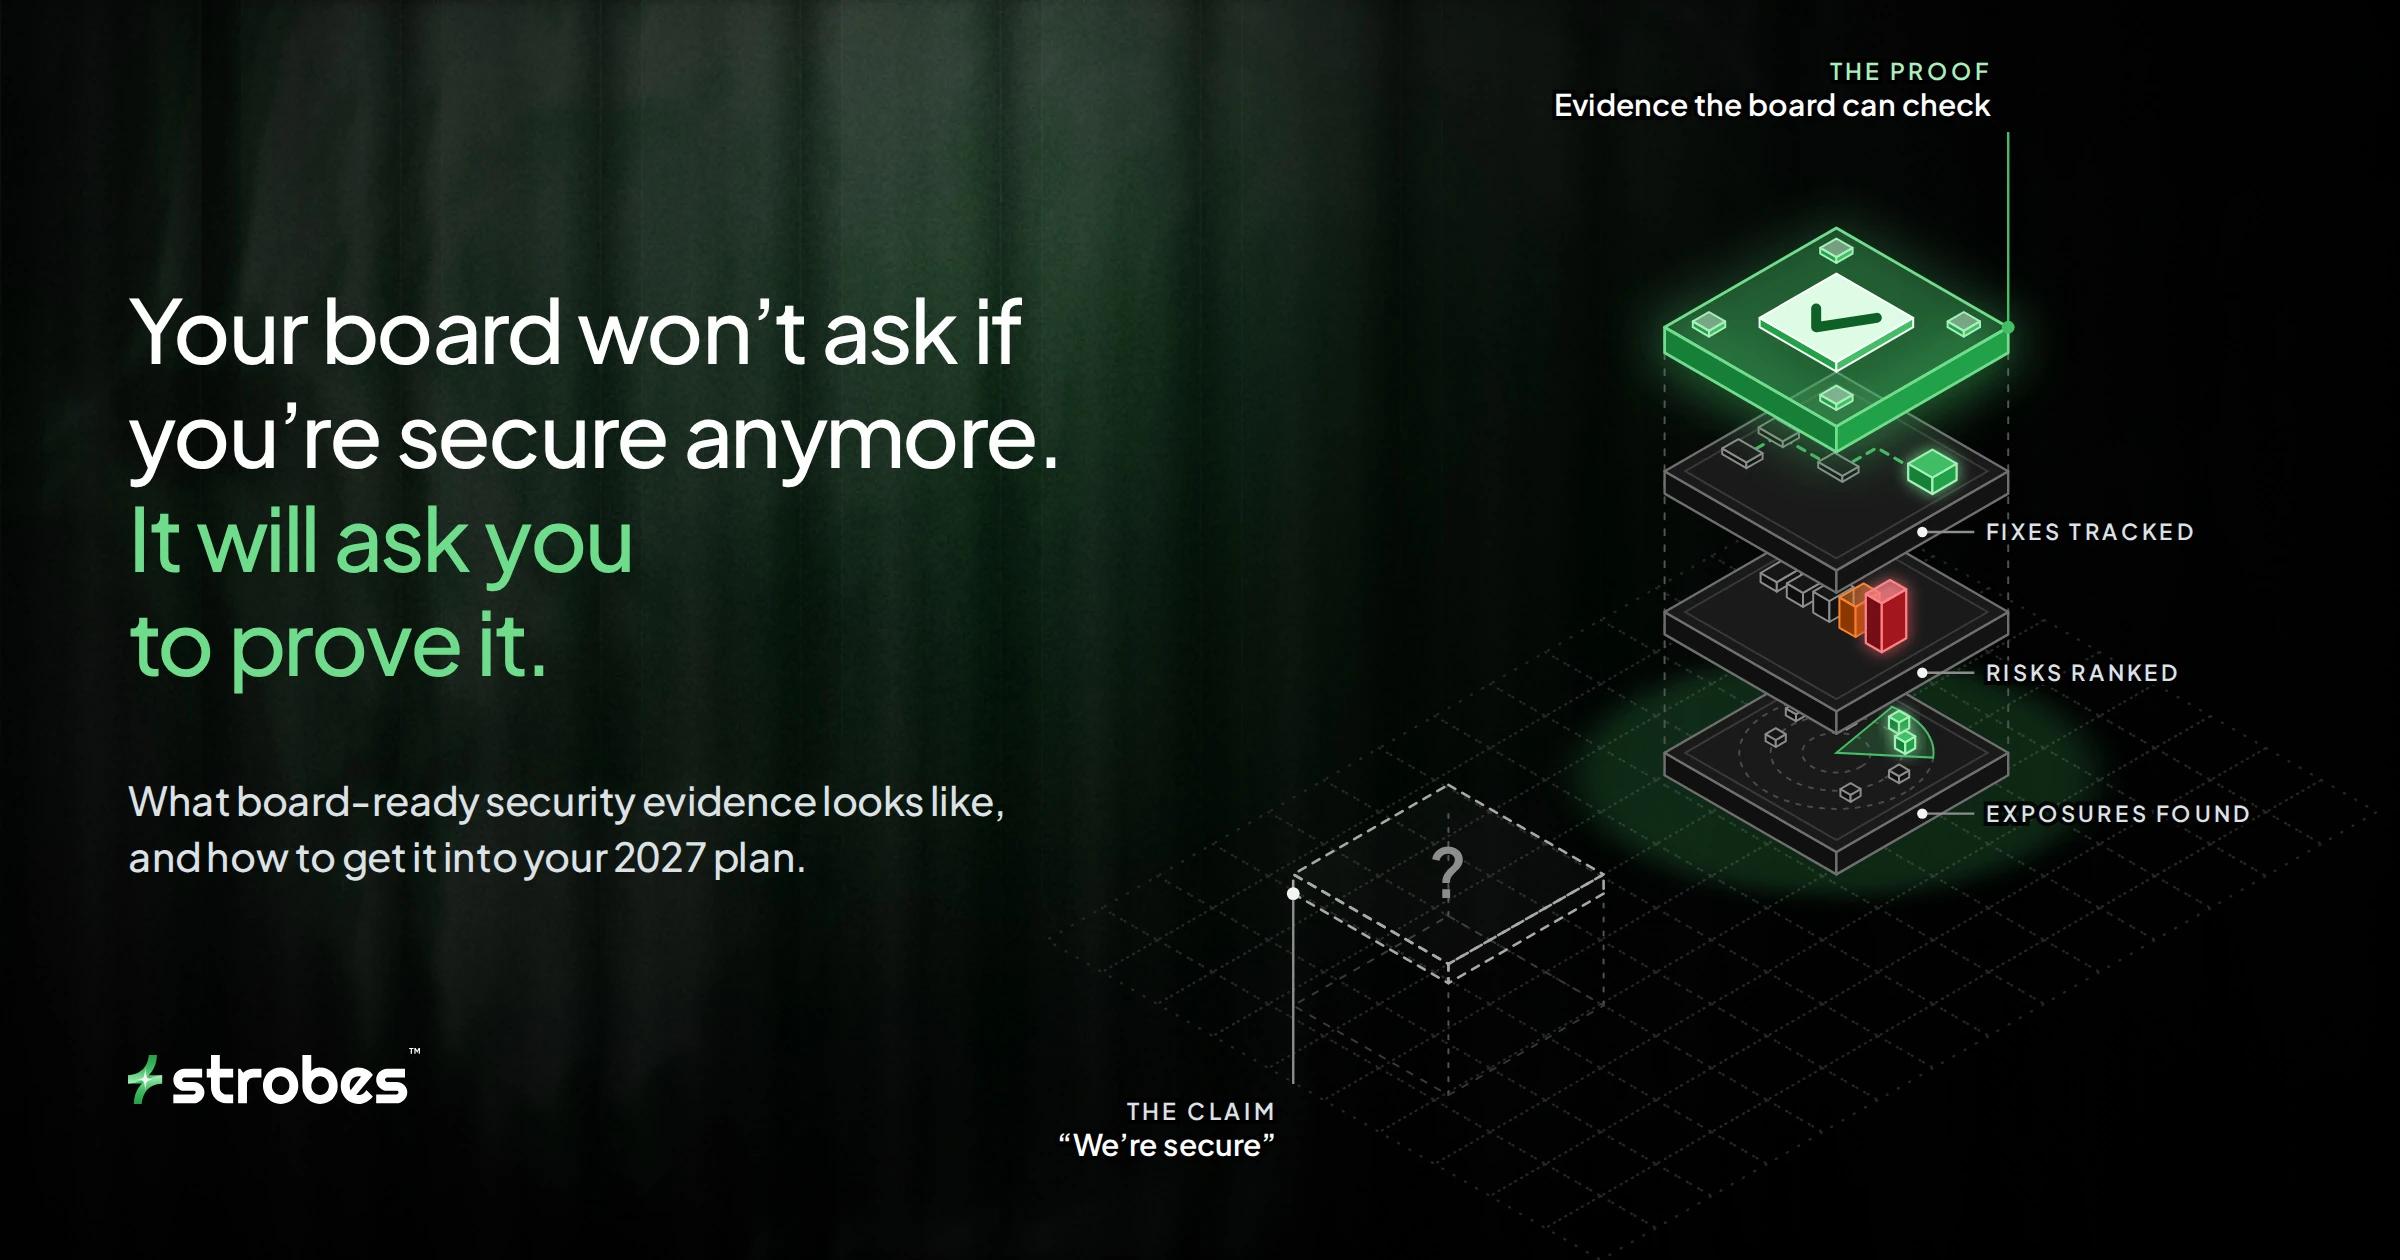
Your board won't ask if you're secure anymore. It will ask you to prove it.
Boards now ask for evidence that cyber risk is within appetite. What board-ready security evidence looks like, how to govern autonomous testing, and how to get it into your 2027 plan.
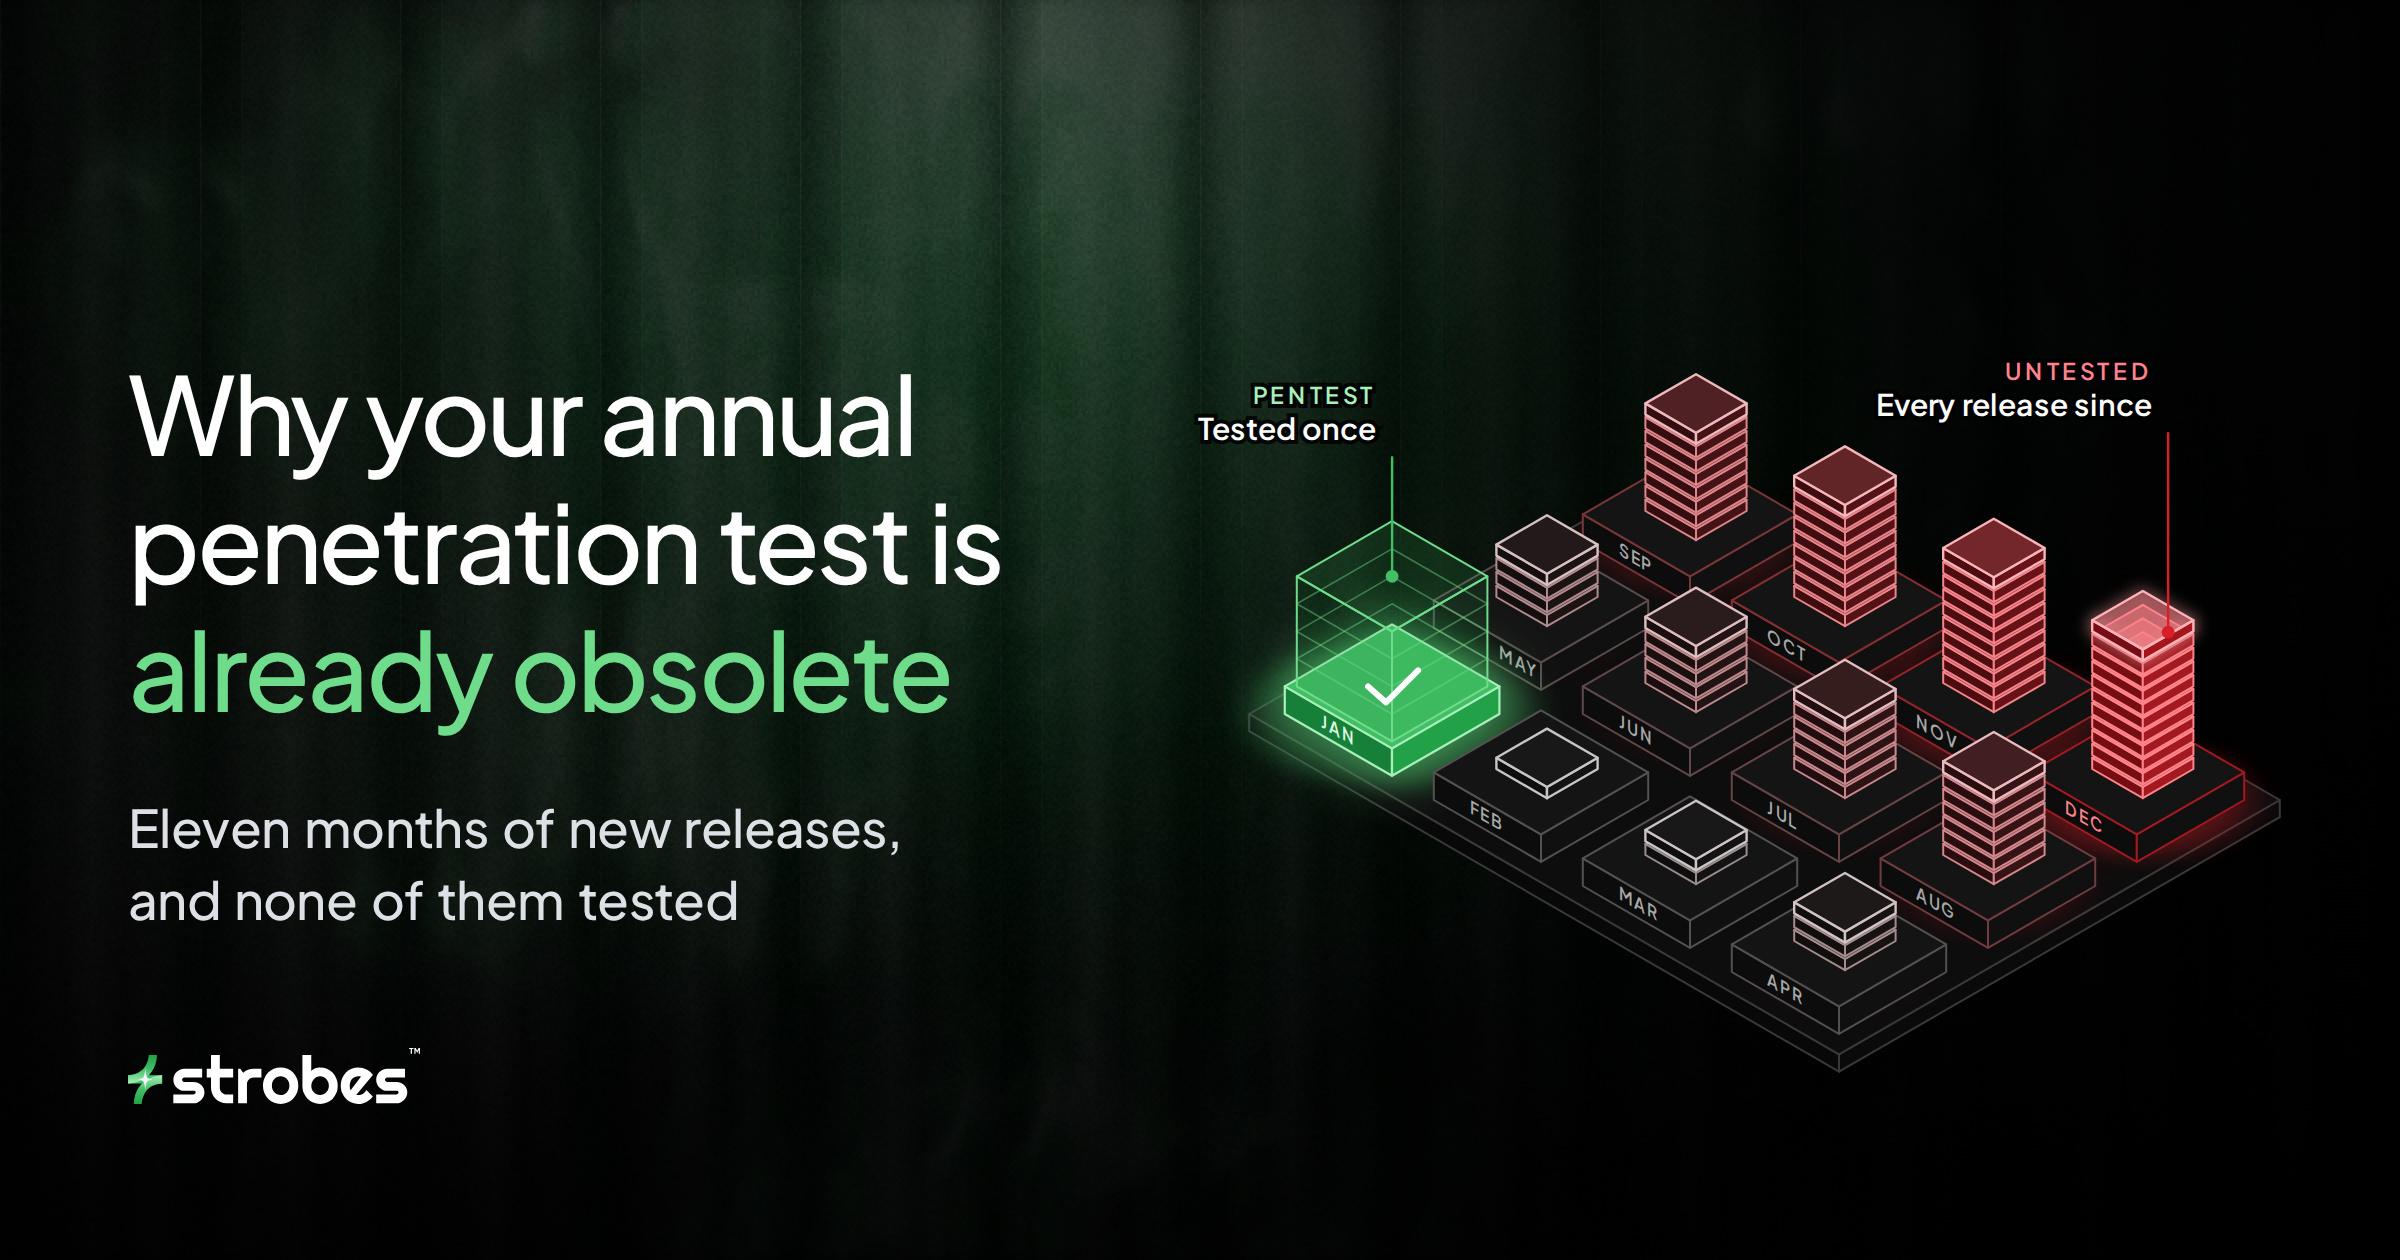
Why your annual penetration test is already obsolete
Your annual pentest describes an environment that no longer exists. Here is how continuous offensive security testing closes the gap, and what it takes to run one.
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
Biggest data breaches of September 2026
153 million driver's licenses claimed, 23.6 million Gyazo records confirmed. September 2026's biggest breaches, with every number sourced.
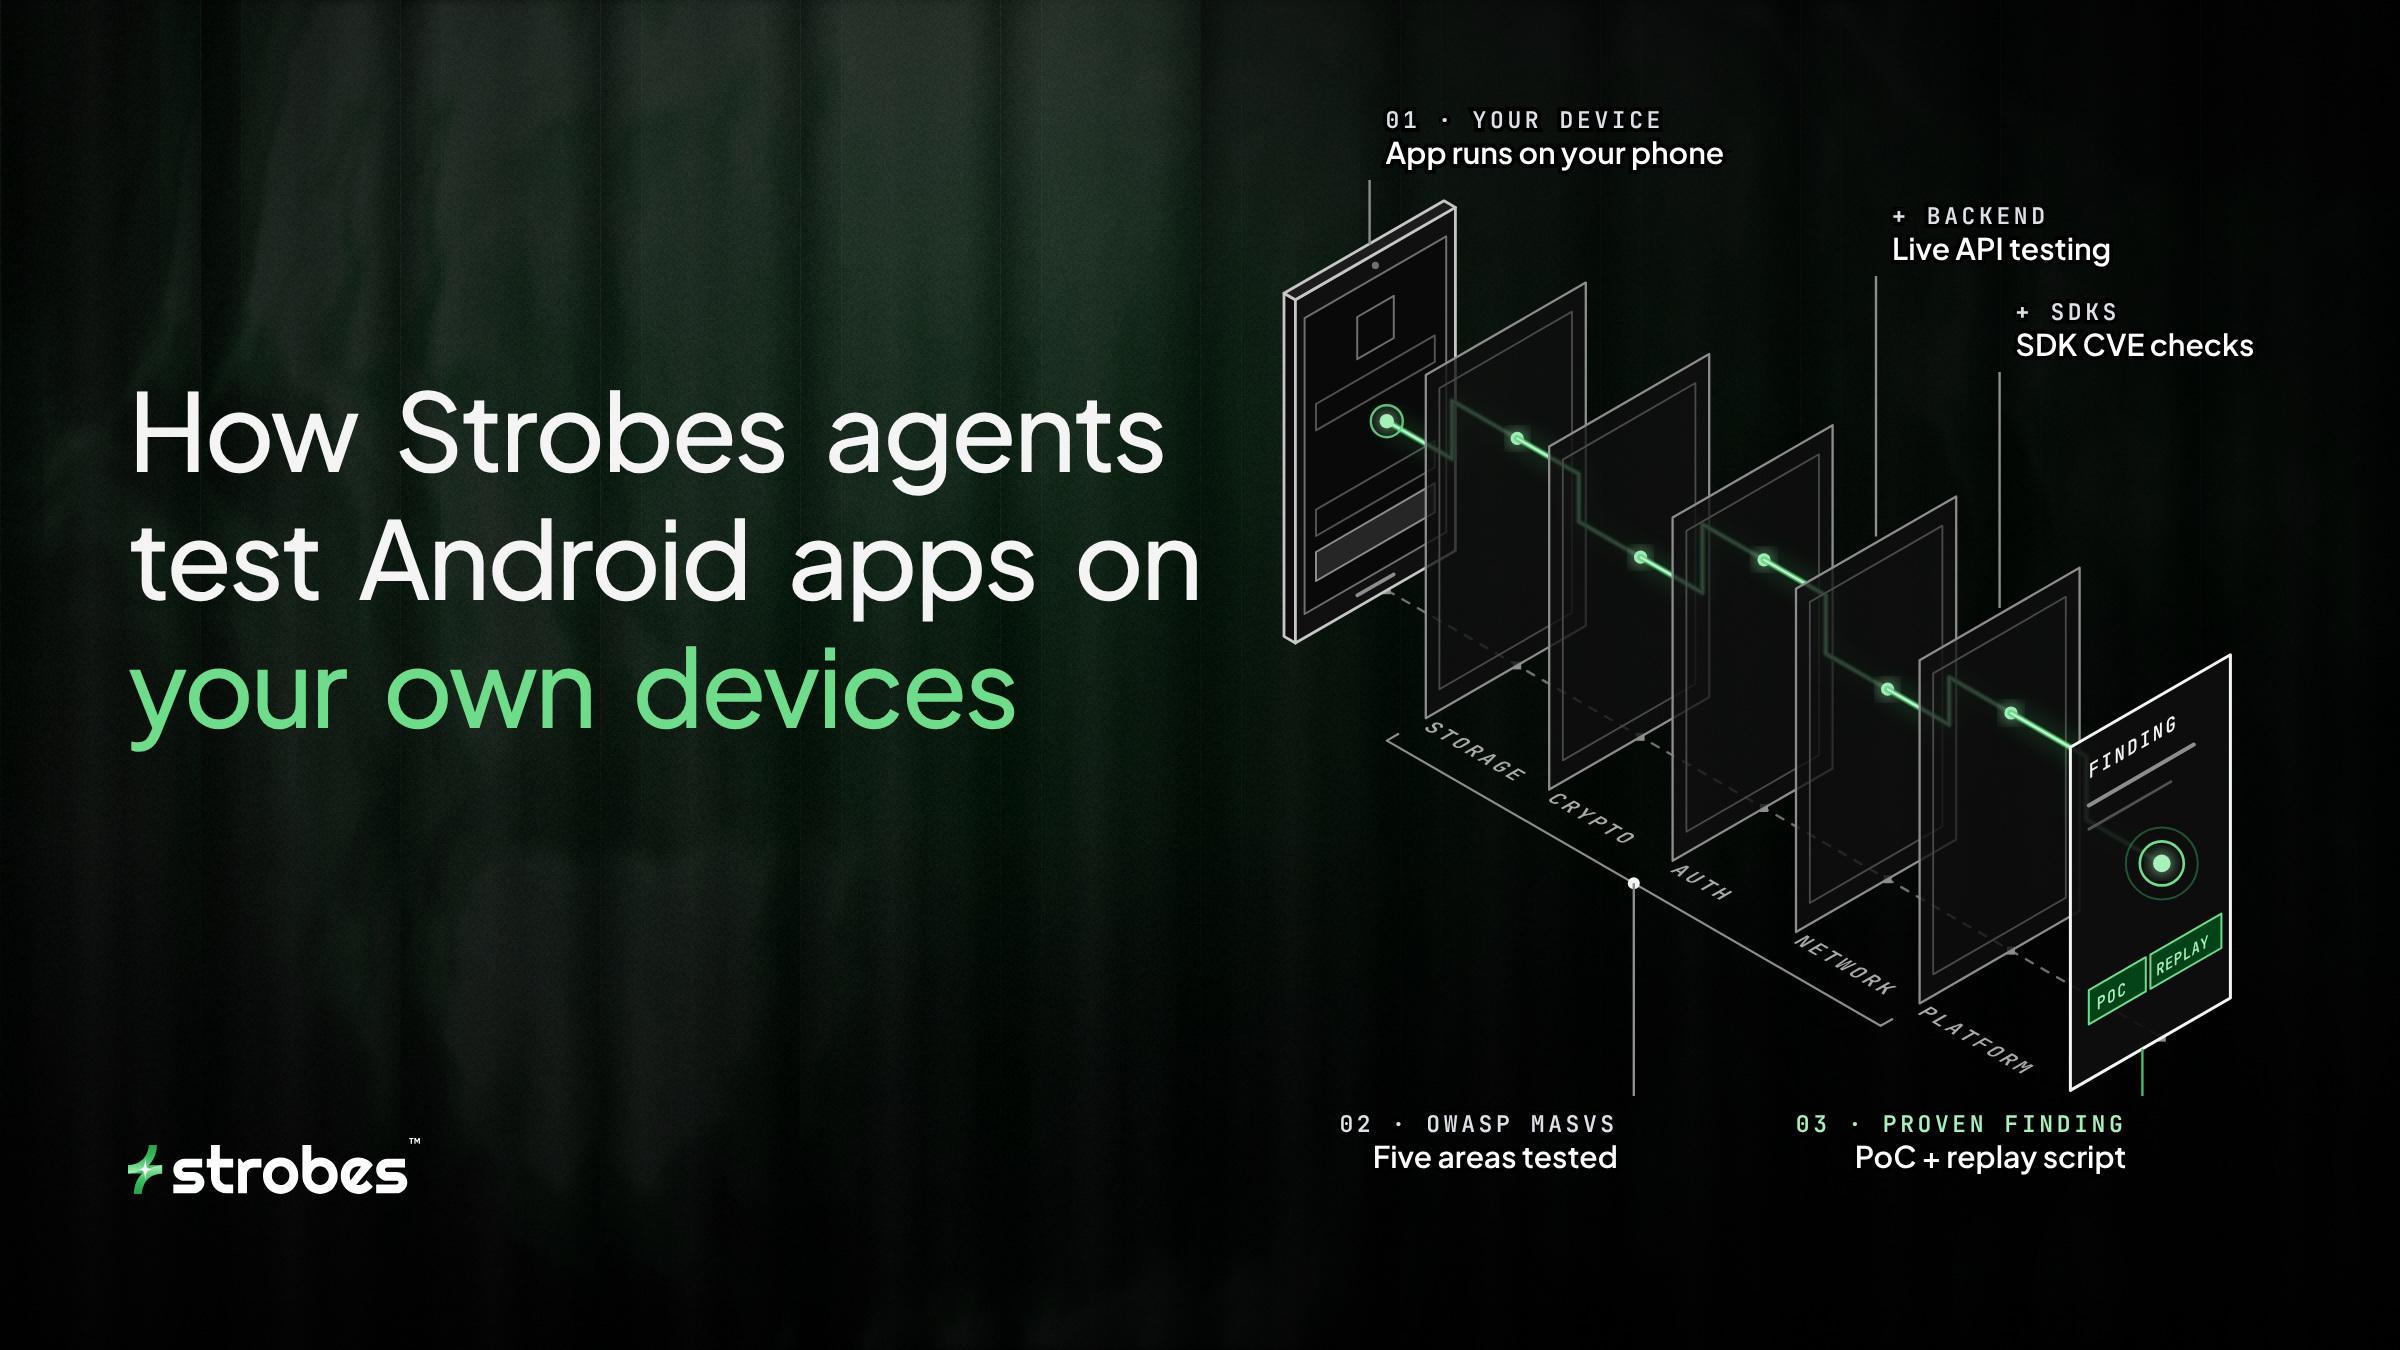
Strobes Agentic Pentesting Now Tests Android Apps on Your Own Devices
Strobes Agentic Pentesting now runs Android app pentesting on your own phones and emulators: live crawling, traffic interception, Frida instrumentation, and verified findings.
Top CVEs of September 2026: Four Zero-Days, and Patching Wasn’t the Fix
Four of September 2026’s top five CVEs were exploited before a patch existed. Fix order, fixed builds, and the compromise check each one needs.
Strobes joins OpenAI's Daybreak program
OpenAI gates its cyber models behind an application, identity checks, and workspace scoping. Strobes is now verified for Daybreak.
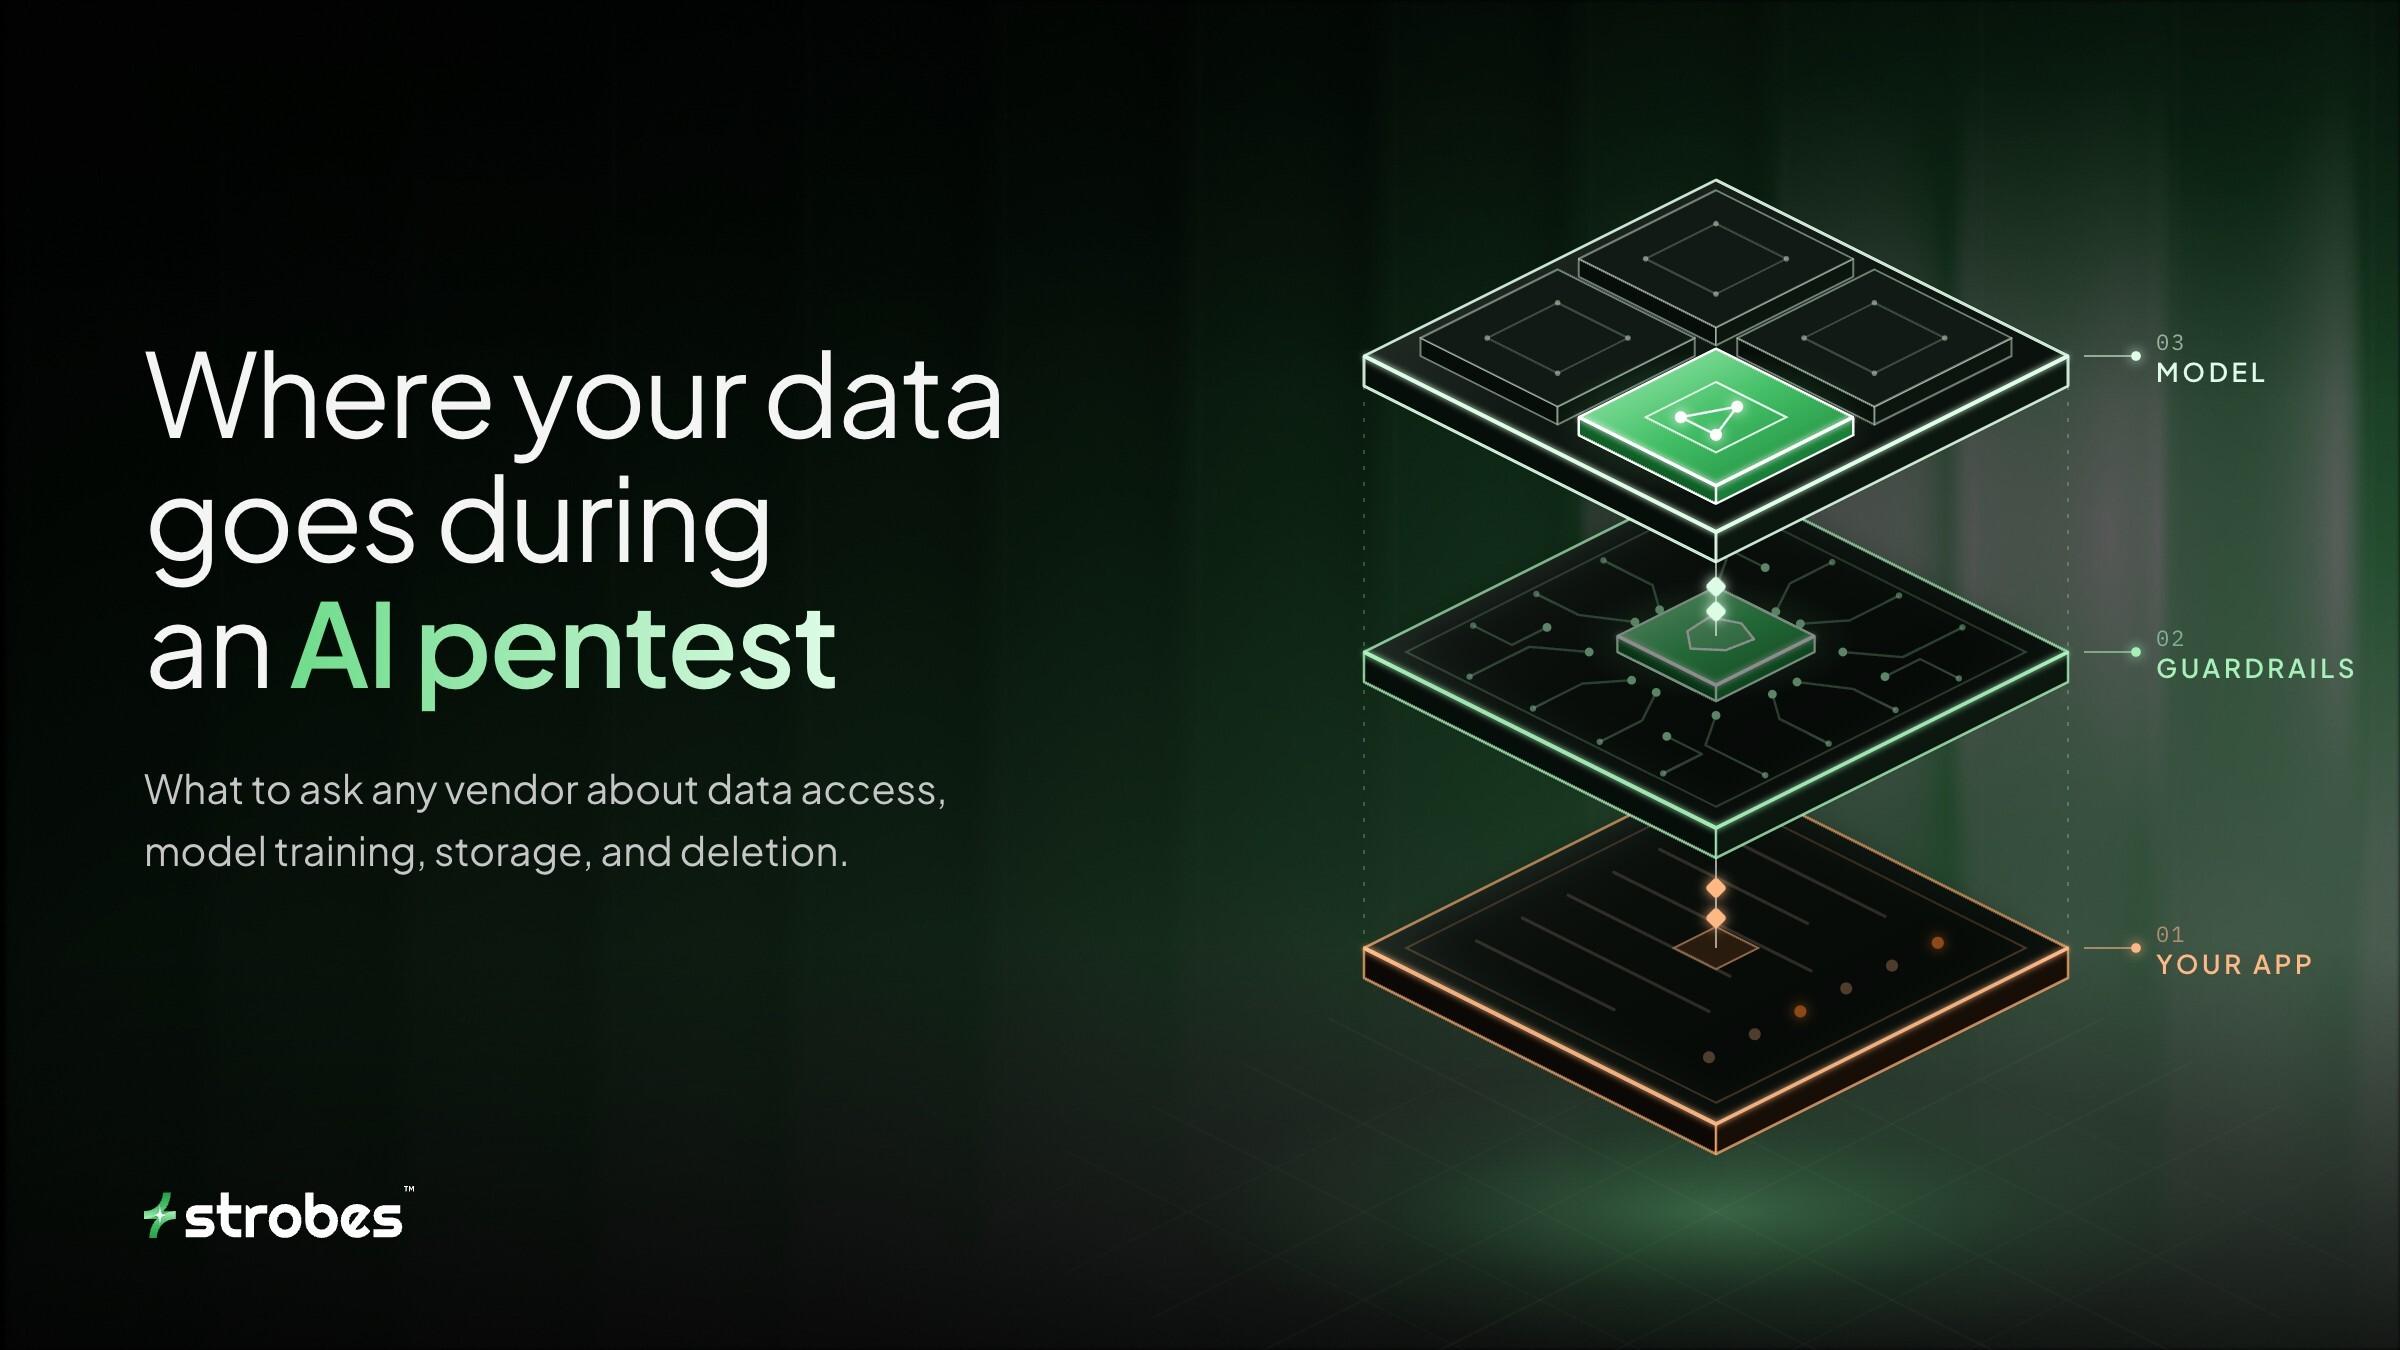
Where your data goes during an AI pentest
Session tokens, customer records, error traces. Here's exactly where that data goes during an agentic pentest, and what to ask any vendor.
Three months inside Anthropic's Cyber Verification Program at Strobes
Strobes has run Claude-powered agentic pentests under Anthropic's Cyber Verification Program since June 2026. Here's what the program gates and what changed in three months.
Are security practitioners actually ready for autonomous pentesting?
We asked 50+ security leaders one open question about autonomous pentesting. Here is the readiness spectrum that came back, and what vendors get wrong.
NIST just published AI prompts for CSF 2.0. Here is what to settle first
NIST's draft SP 1353 provides AI prompts for three CSF 2.0 tasks and says weeks of drafting compresses into hours. Here is what the prompts can draft, what only humans can validate, and the four things to settle before anyone opens a model.
Top CVEs of August 2026
August's CVSS 7.0 was a Lazarus zero-day exploited for five weeks. Its CVSS 10.0 needed no patch at all. The top CVEs of August 2026, ranked by exploitation evidence rather than severity, with remediation steps for all five.
Biggest data breaches of August 2026
284 million records claimed at McKesson, 12.9 million verified at Carhartt. The eight biggest data breaches of August 2026, with every number checked against a company statement, filing, or named outlet.