
Strobes joins OpenAI's Daybreak program
OpenAI gates its cyber models behind an application, identity checks, and workspace scoping. Strobes is now verified for Daybreak.
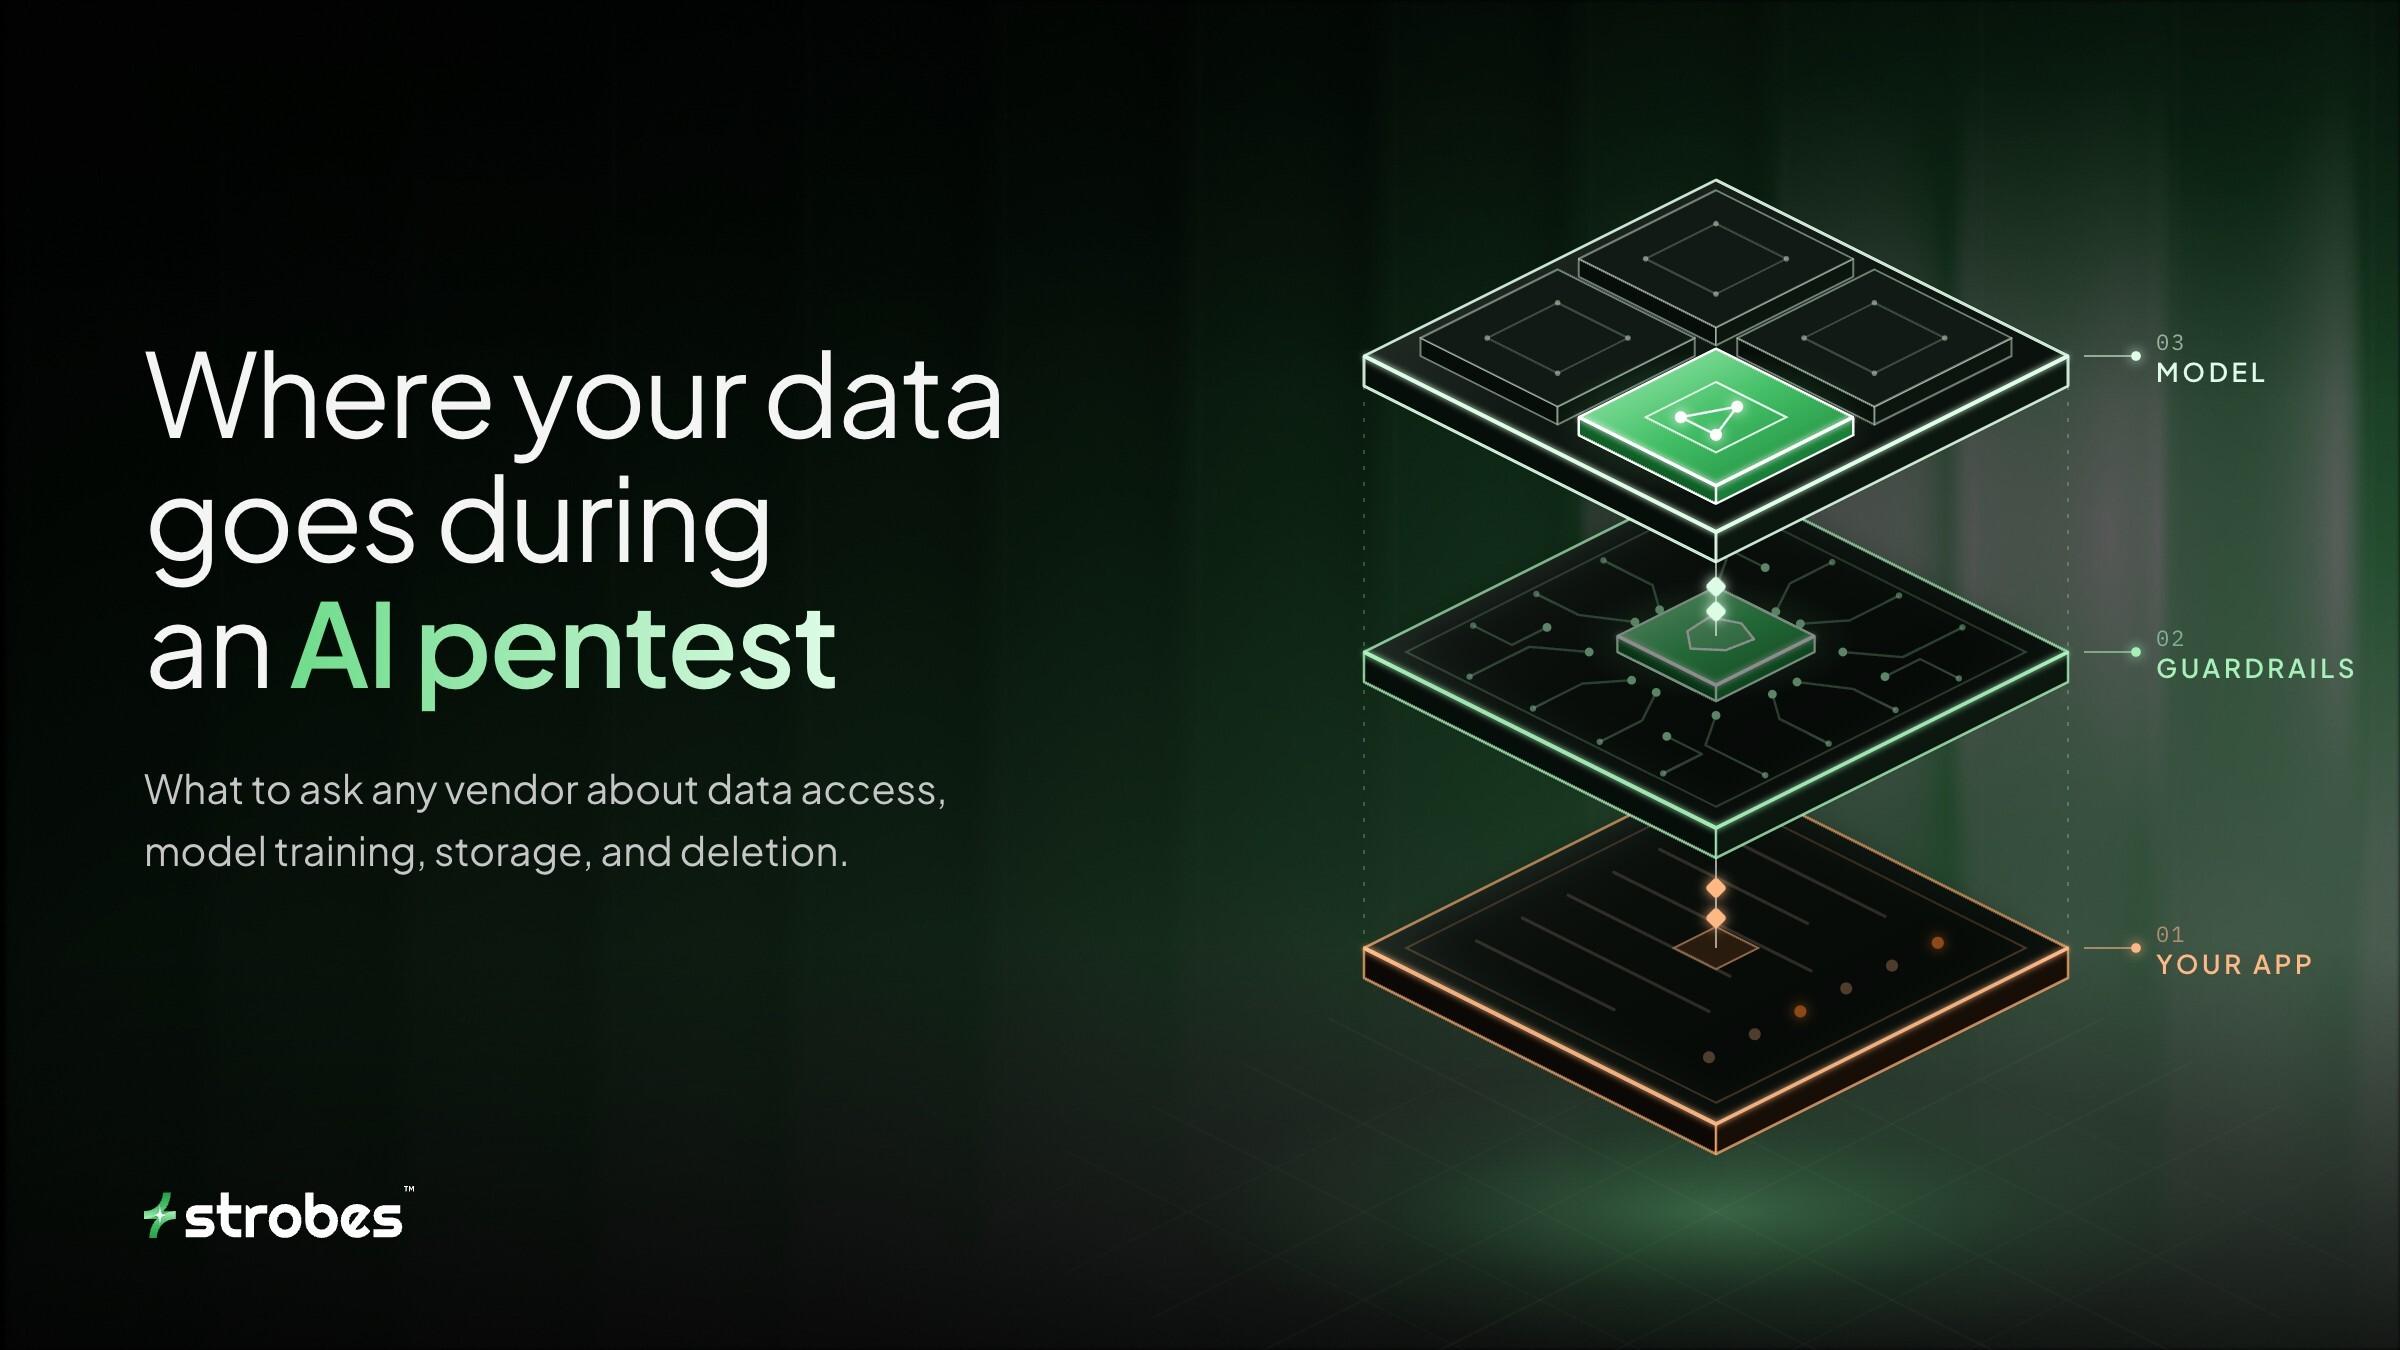
Where your data goes during an AI pentest
Session tokens, customer records, error traces. Here's exactly where that data goes during an agentic pentest, and what to ask any vendor.
Security Insights
Deep dives, expert analysis, and practical guidance on exposure management, adversarial validation, and the future of AI-driven exposure management.
Three months inside Anthropic's Cyber Verification Program at Strobes
Strobes has run Claude-powered agentic pentests under Anthropic's Cyber Verification Program since June 2026. Here's what the program gates and what changed in three months.
Are security practitioners actually ready for autonomous pentesting?
We asked 50+ security leaders one open question about autonomous pentesting. Here is the readiness spectrum that came back, and what vendors get wrong.
NIST just published AI prompts for CSF 2.0. Here is what to settle first
NIST's draft SP 1353 provides AI prompts for three CSF 2.0 tasks and says weeks of drafting compresses into hours. Here is what the prompts can draft, what only humans can validate, and the four things to settle before anyone opens a model.
Top CVEs of August 2026
August's CVSS 7.0 was a Lazarus zero-day exploited for five weeks. Its CVSS 10.0 needed no patch at all. The top CVEs of August 2026, ranked by exploitation evidence rather than severity, with remediation steps for all five.
Biggest data breaches of August 2026
284 million records claimed at McKesson, 12.9 million verified at Carhartt. The eight biggest data breaches of August 2026, with every number checked against a company statement, filing, or named outlet.
How to automate pentest reporting without losing report quality
Report quality is decided before the reporting layer runs. Here's the pipeline, the gates that stop bad output shipping, and what a real automated report contains.
Build vs Buy Agentic Pentesting and What the DIY Path Costs
Everyone can build a working pentest agent in a weekend. Owning it for two years is the hard part: the four costs nobody adds up, and the seven requirements a demo never has to meet.
How to Achieve Cheaper, Faster and Accurate Pentests
Cheaper, faster and accurate pentests were never a real tradeoff. Context removes it: one graph of assets, code and cloud that every engagement reads from and writes back to.
How to run an agentic pentesting POC
A 10-day testing playbook to evaluate agentic pentesting vendors: what to test each day, the red flags to watch for, and a scorecard that works with any vendor.
Tooling as Code and Structured Scratchpads
The two changes that moved our AI security agents furthest this year had nothing to do with the model. Here is how tooling as code and structured scratchpads reshaped how the agents act, and how they prove a finding is real.